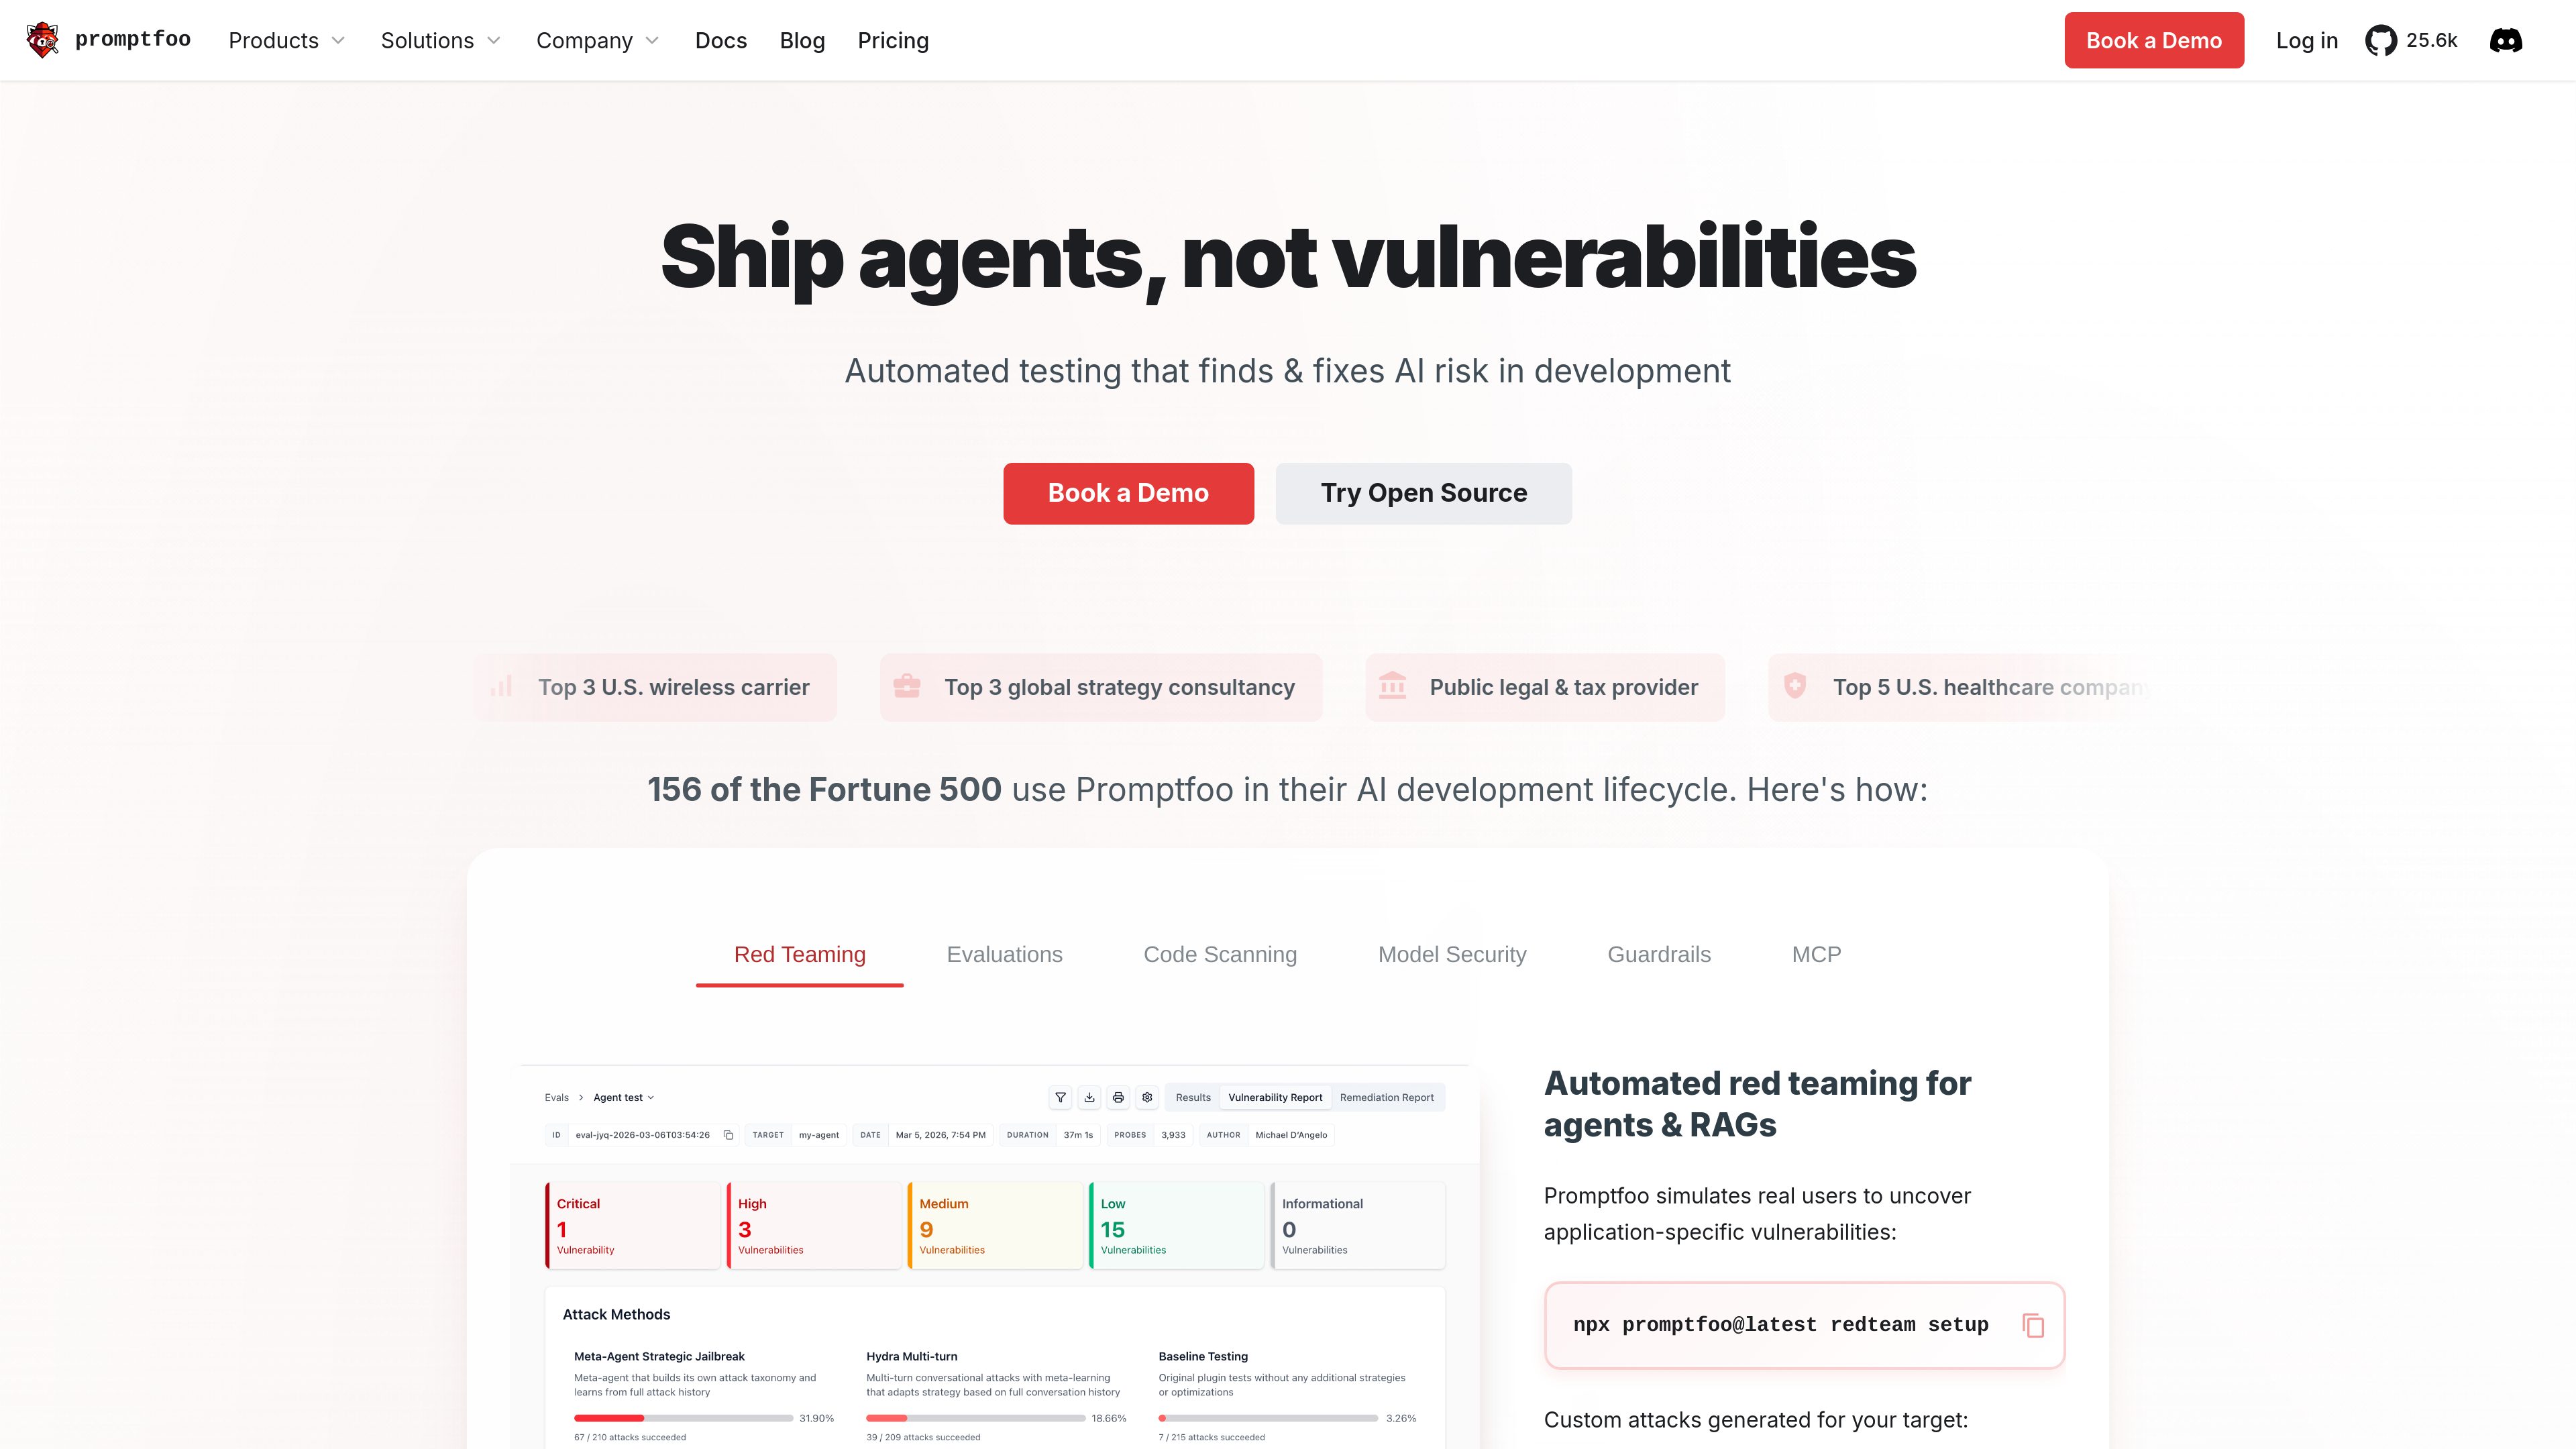
Promptfoo is an AI security and testing platform for evaluating LLM applications, agents, models, and workflows. It helps developers and security teams find vulnerabilities, validate guardrails, map findings to security frameworks, and track remediation through development and deployment.
Promptfoo is an AI security and testing platform for LLM applications, agents, models, and related workflows. Its core workflow connects to an application, generates context-aware attacks and evaluations, and returns vulnerability findings with remediation guidance. Testing can be used during development, in CI/CD pipelines, or as part of ongoing monitoring.
The platform combines application red teaming, guardrail validation, model-file screening, behavioral testing, and compliance mapping. It is intended for developers and security teams that need to evaluate AI systems before and after deployment rather than rely only on static prompt or model tests.
Promptfoo 能做什么?
01
Application-specific red teaming
Generates dynamic attacks tailored to an application instead of relying only on static jailbreak tests. Coverage includes more than 50 vulnerability types, such as prompt injection, RAG document exfiltration, PII leaks, unauthorized data access, and tool or function discovery.
02
Vulnerability reports and remediation guidance
Returns detailed findings after testing and provides actionable remediation steps. Enterprise workflows can surface security findings in pull requests, track fixes across teams, and maintain a searchable history of scans.
03
Adaptive guardrail validation
Tests existing guardrail systems independently and uses red-team attack data to improve defenses over time. Guardrails can be deployed with minimal code changes on cloud or on-premises environments and work with major LLM providers and custom models.
04
Model file and behavioral security testing
Screens model files for malicious code, backdoors, suspicious operations, and risky configurations, with listed support for PyTorch, TensorFlow, Keras, Pickle, and JSON/YAML. It also tests foundation and fine-tuned models against jailbreaks, injections, and other real-world attack scenarios.
05
Compliance and continuous monitoring
Maps findings to OWASP, NIST, the EU AI Act, MITRE ATLAS, or custom policies. CI/CD integration, scheduled testing, real-time alerts, and automated evaluations support ongoing visibility into an application's security posture.
使用场景
“Test an AI application before release”
Development and security teams can connect an application, agent, or workflow and run context-aware attacks against its business logic, RAG setup, integrations, and tools. The resulting findings help teams address vulnerabilities before deployment.
“Add security testing to CI/CD”
Teams can run evaluations in development pipelines and use pull-request findings and remediation guidance to review security changes alongside code. Scheduled or continuous testing can maintain a risk timeline as the application evolves.
“Validate an existing guardrail system”
Organizations that already use a guardrail product can use Promptfoo's red-teaming capabilities as an independent validation layer. Attack results provide evidence of gaps and data for refining defenses against emerging threats.
“Screen and compare AI models”
Model teams can inspect model files before deployment, test behavioral resilience against injections and jailbreaks, and compare the security of foundation or fine-tuned models before selecting one for an AI pipeline.
“Document security and compliance posture”
Security and compliance teams can map assessment results to OWASP, NIST, EU AI Act, MITRE ATLAS, or organization-specific policies, then use reports and centralized dashboards for review and tracking.
常见问题
What does Promptfoo test?
Promptfoo tests AI applications, agents, workflows, and models for vulnerabilities including prompt injection, jailbreaks, RAG document exfiltration, system prompt override, malicious resource fetching, PII leaks, harmful content generation, unauthorized data access, and tool or function discovery. The site also describes model-file security scanning and behavioral testing.
How does a typical red-team assessment work?
The documented workflow is to describe or connect the application, let Promptfoo generate application-specific attacks, review detailed vulnerability reports, and apply the suggested remediations. Testing can be integrated into CI/CD or run on a schedule.
Can Promptfoo validate guardrails from another provider?
Yes. Promptfoo describes third-party guardrail validation as an independent testing layer. Its red-teaming capabilities can test an existing guardrail system and use observed attack data to help improve defenses.
Which deployment and plan options are available?
The open-source Community version supports local testing and self-hosting and includes core evaluation features, integrations, and vulnerability scanning. Enterprise adds collaboration, monitoring, dashboards, SSO, permissions, API access, and managed cloud or on-premises options. Enterprise and Enterprise On-Premise pricing is customized.
Are there limits on Community red teaming?
The Community offering includes up to 10,000 red-team probes per month. The pricing page explains that some plugins require inference for dynamic test generation and grading; Enterprise customers can purchase additional probes for larger-scale testing.
快速信息
Product type
AI security and testing platform
Primary users
AI developers, security teams, and model teams
Core workflow
Connect, attack, review findings, and fix
Security coverage
More than 50 AI vulnerability types
Deployment
Local, self-hosted, managed cloud, or on-premises options depending on plan
Community plan
Open source and free, with up to 10,000 red-team probes per month
Promptfoo 替代品
D
DeepEval
deepeval.com
DeepEval is an open-source LLM evaluation framework for testing and benchmarking AI applications. It helps developers run pytest-native evaluations, score outputs and agent traces, and iterate on systems across text, image, audio, and voice workflows.
G
Galileo
www.galileo.ai
Galileo is an AI observability and evaluation platform for testing, debugging, and governing LLM and agent systems across development and production. It helps teams turn evaluation results into production guardrails and monitor AI behavior at scale.
J
Jev State
jev-state.vercel.app
Jev State is a workspace for defining, testing, and regression-checking conversational decisions powered by Jev. It helps teams inspect why an agent takes a step and export runnable TypeScript and tests for an application.
G
Giskard
www.giskard.ai
Giskard is an AI security and evaluation platform for testing conversational LLM agents before and after deployment. It combines automated red teaming, quality evaluation, runtime guardrails, and remediation workflows for teams responsible for reliable AI systems.
M
MCPJam
www.mcpjam.com
MCPJam is a testing and evaluation platform for MCP servers. It helps developers inspect servers locally, run user and model-based tests, and add behavior checks to CI/CD workflows.
Q
QAgent
qagent.in
QAgent is an AI agent testing and quality assurance platform for developers and agile teams. It connects to an agent through a webhook or endpoint, runs automated test cases, and evaluates responses for groundedness, policy adherence, prompt compliance, and related quality dimensions.