
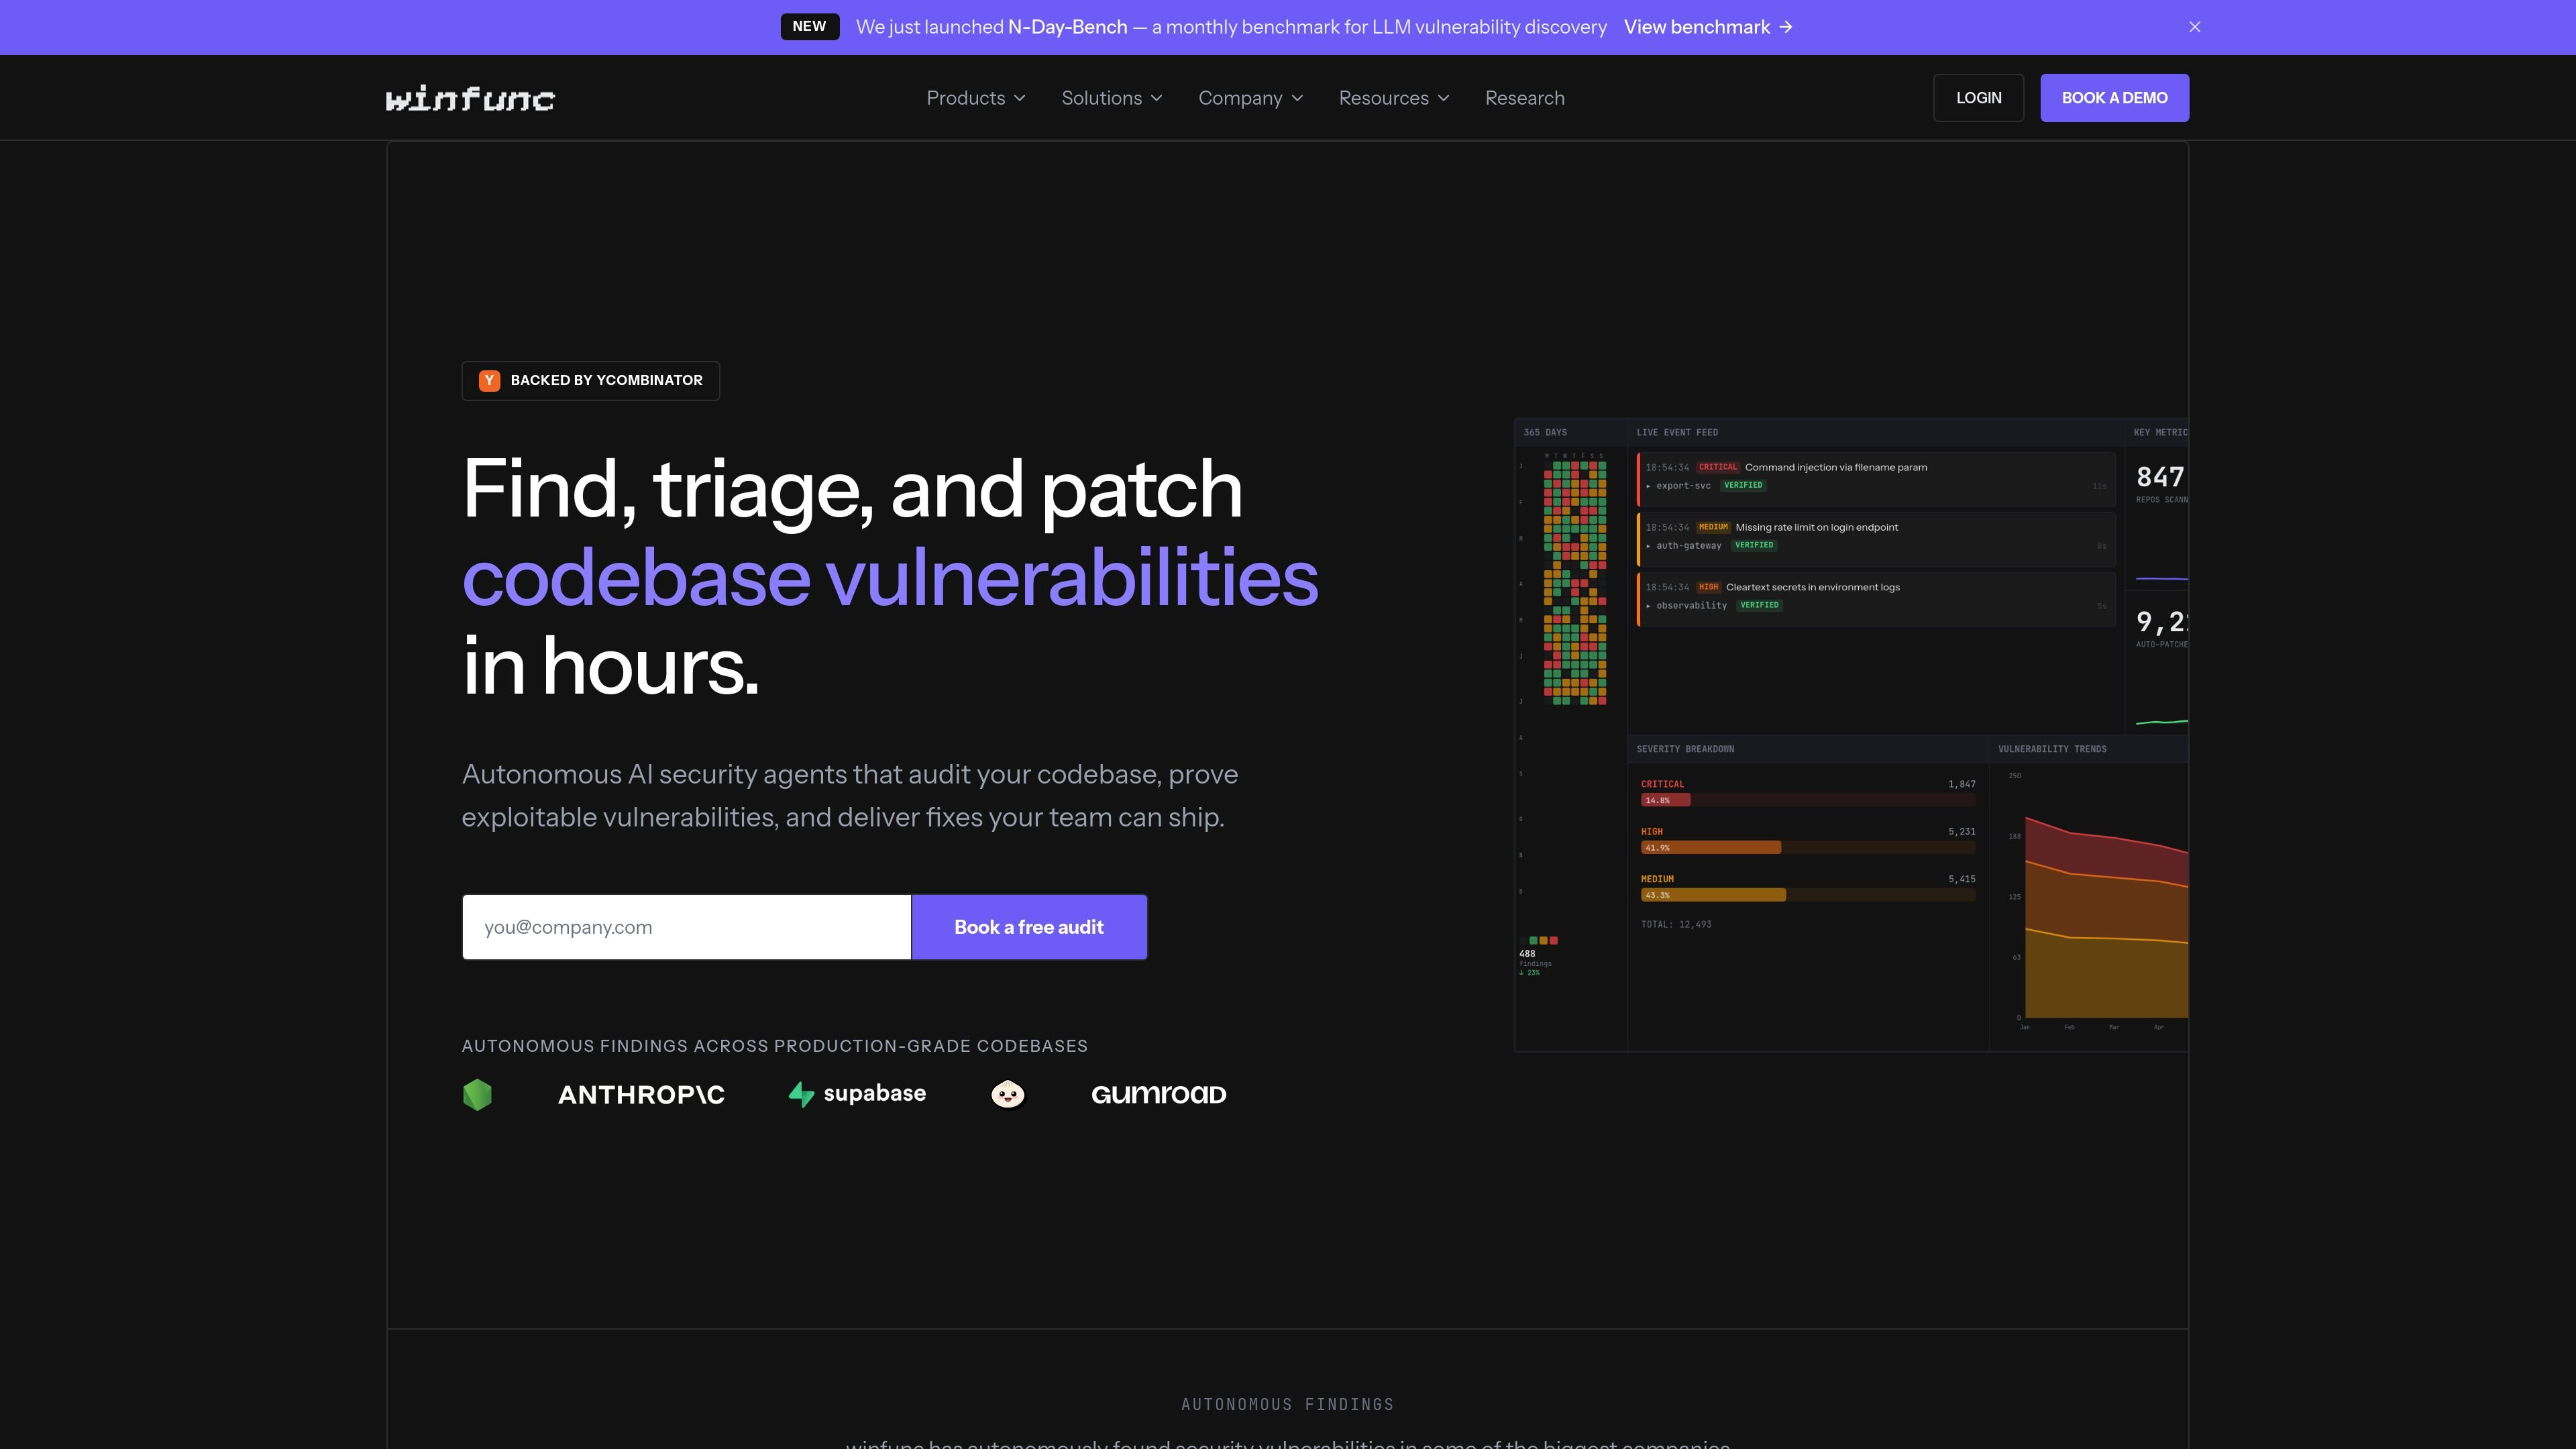
Secure codebase connection
Link GitHub repositories securely so the platform can map the codebase architecture before analysis begins.
AI-native security platform that finds, validates, and fixes code vulnerabilities
winfunc is an AI-native security engineering platform for finding, triaging, and patching codebase vulnerabilities. The homepage describes it as software that automates the full cycle, from initial audit through fix delivery, with the goal of compressing security review work into hours rather than a longer manual process.
The published workflow starts by connecting a GitHub repository, then runs an autonomous audit that produces proof-of-concept evidence for vulnerabilities it finds. After that, winfunc can generate patches through pull requests and continue scanning commits to maintain protection over time. The MCP product page adds an editor-based workflow for scanning snippets and verifying changes inside Cursor, Claude, Windsurf, and Cline.
Link GitHub repositories securely so the platform can map the codebase architecture before analysis begins.
Run an autonomous security audit that looks for vulnerabilities across the connected codebase and reports findings without requiring manual scanning of each file.
Produce proof-of-concept validation for vulnerabilities, so findings are tied to exploitable behavior rather than static flags alone.
Deliver automated fixes through pull requests, giving teams a patch path instead of only a report.
Scan every commit for ongoing protection and surface issues as the codebase changes.
Work inside Cursor, Claude, Windsurf, and Cline through Winfunc MCP for real-time vulnerability scanning in the editor.
Security and platform teams can connect a GitHub repository to get an autonomous audit that identifies vulnerabilities and attaches proof-of-concept evidence for review.
Developers working in supported editors can scan snippets and verify code changes before they land, which helps catch issues during active implementation.
Teams that want a patch path, not just findings, can use the PR-based workflow to turn audit output into reviewable fixes.
Organizations that need ongoing protection can keep scanning commits so new changes are checked after the initial audit.
The site presents winfunc as an AI-native security engineering platform that finds, triages, and patches codebase vulnerabilities in hours. It is positioned around autonomous audits, proof-of-concept validation, and patch delivery through pull requests.
The homepage says you connect a GitHub codebase securely, then winfunc performs an autonomous audit and continuously scans commits for ongoing protection. The research page and product pages reinforce that the workflow centers on codebase analysis and patch generation.
The product page says Winfunc MCP provides real-time vulnerability scanning inside Cursor, Claude, Windsurf, and Cline, letting users scan snippets, verify changes, and audit codebases without leaving their editor flow.
The provided pages do not show pricing numbers or clear plan tiers. The pricing page confirms a pricing area exists, but the source text available here does not expose the actual pricing structure.
Traffic data is for reference only.
fx.sh
fx is a tiny, open, native coding agent and CLI for working with code from the terminal. It is designed for research, embeddability, and use as part of larger systems, with support for local or cloud inference.

balsa-ui.com
Balsa UI is an agent-native, open-code component system for Vue and React. It helps teams create design systems and build interfaces with agent-assisted workflows.

vice-platform.com
VICE runs web security audits for indie builders, with public light scans, verified full audits, Supabase RLS deep scans, AI fixes, and CI checks.