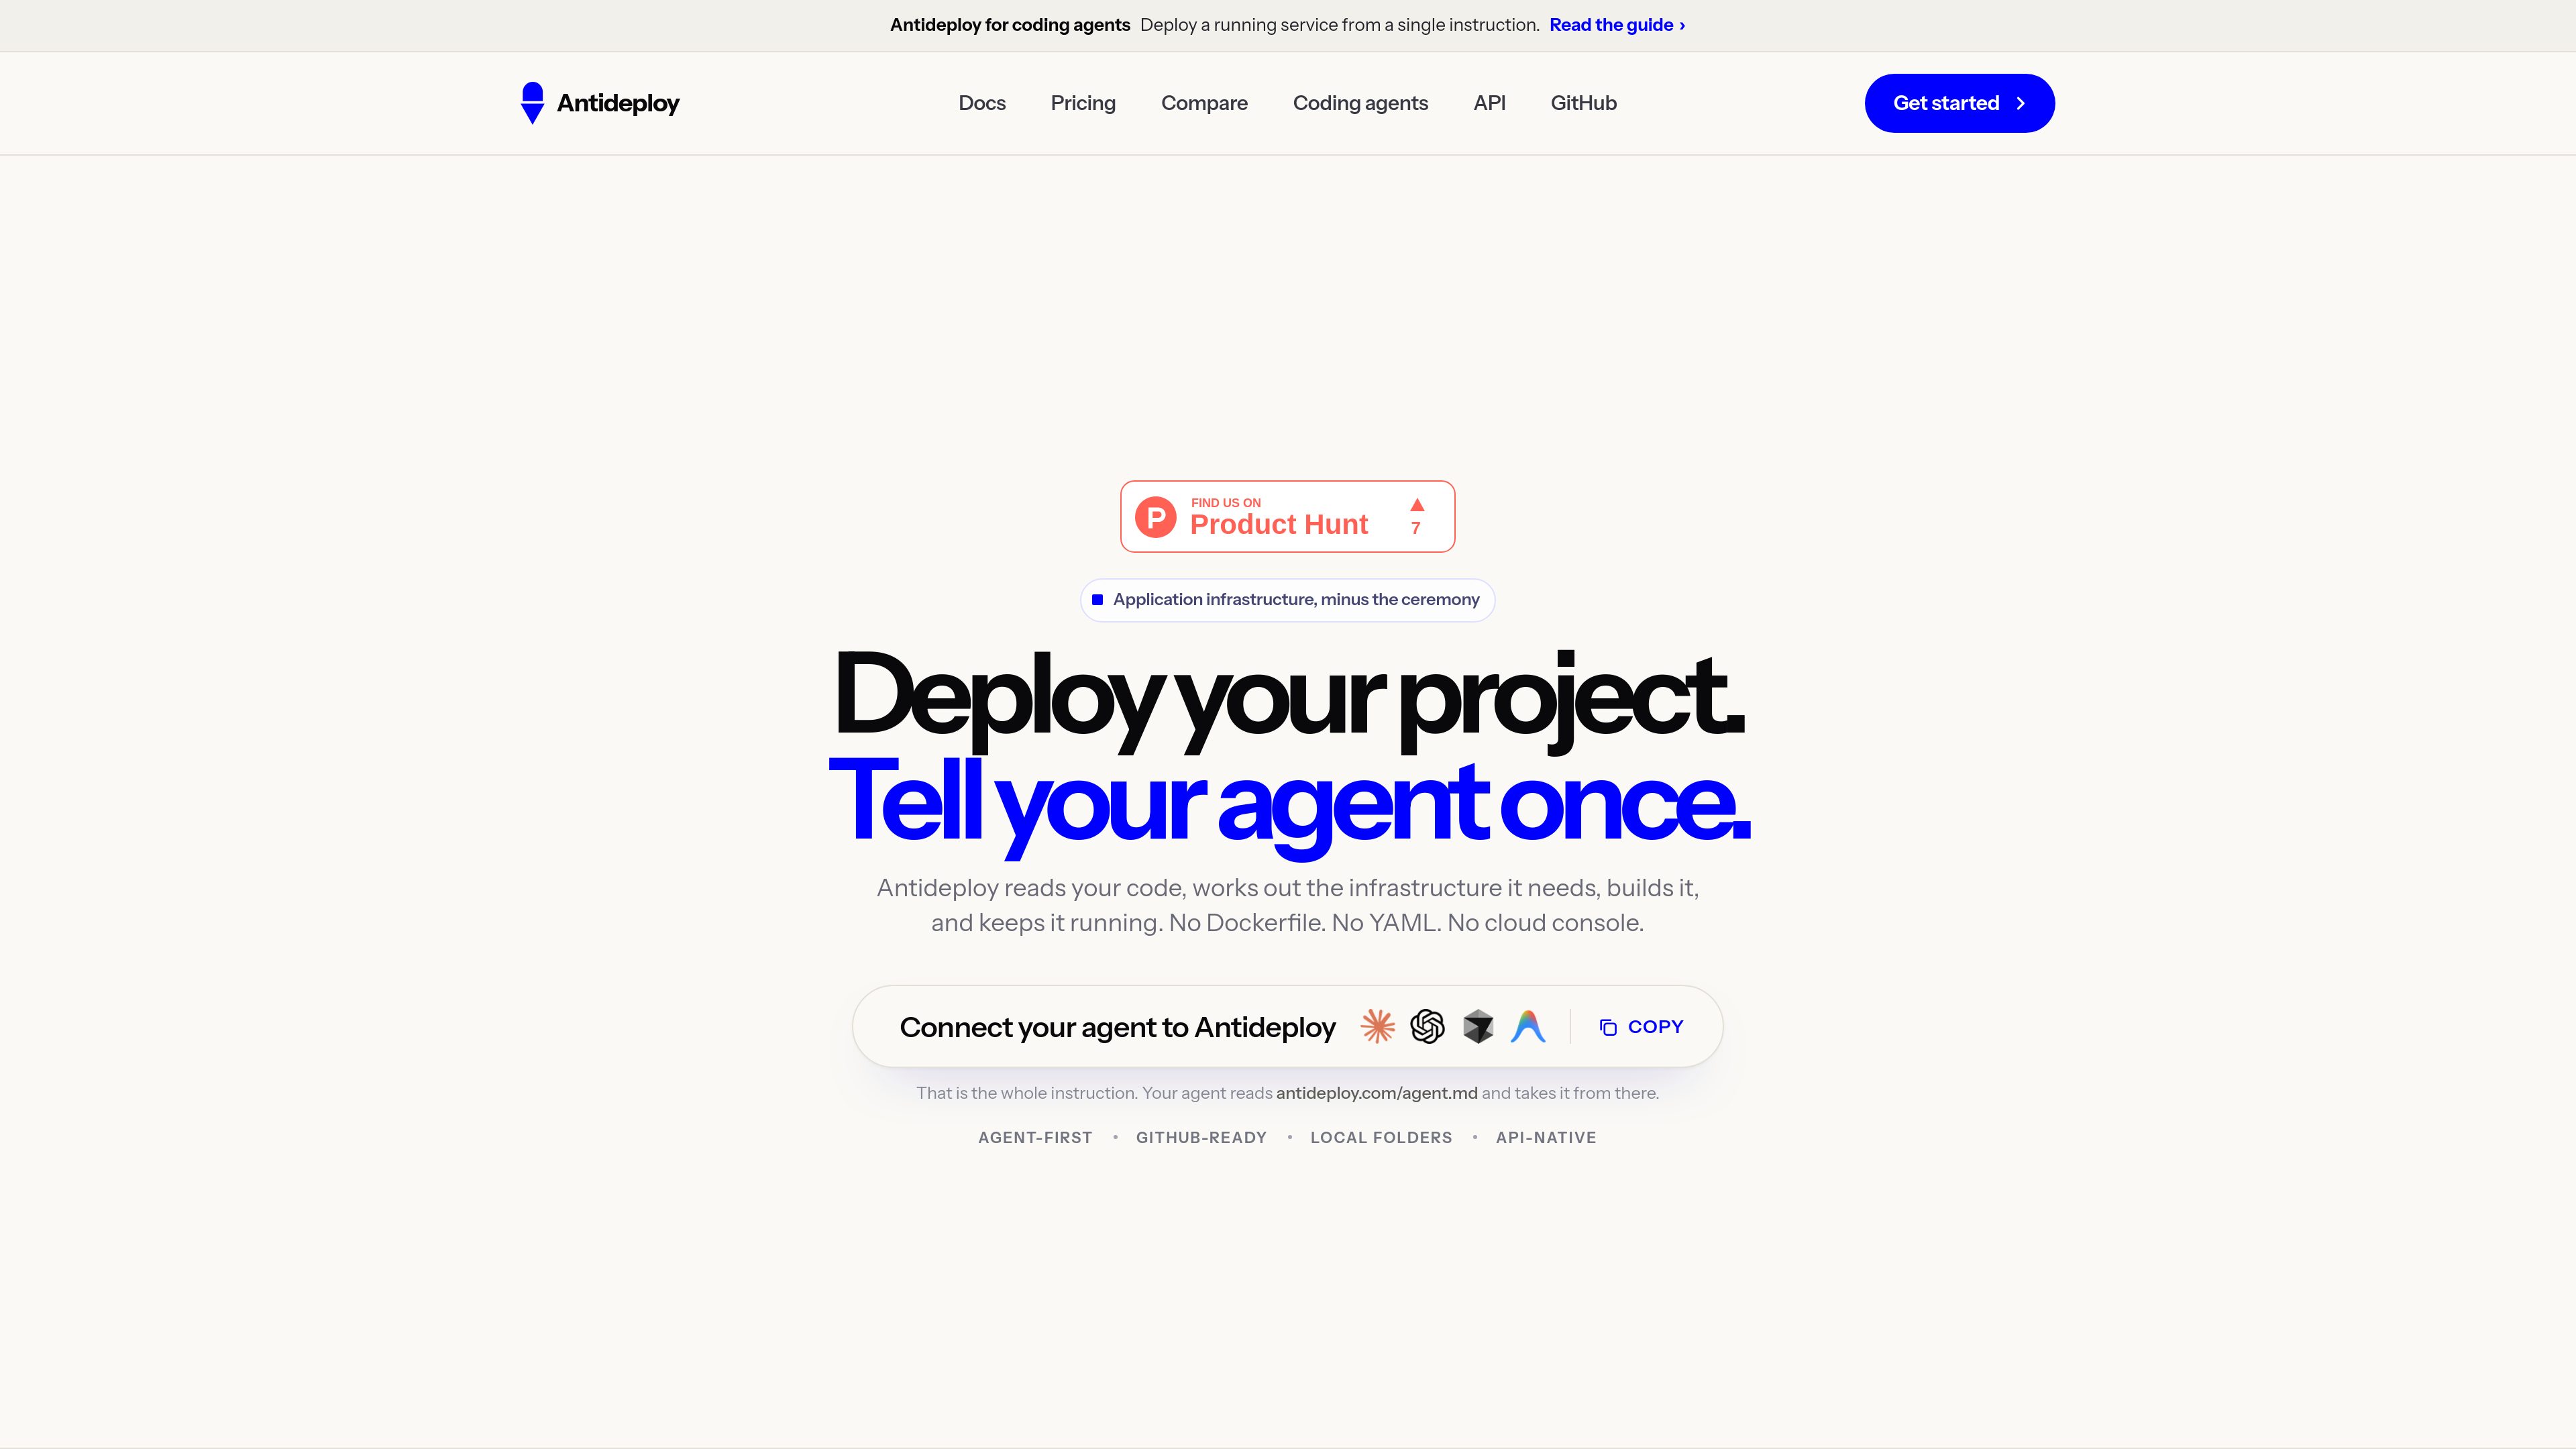
Antideploy reads an application’s source code, identifies its runtime and infrastructure requirements, builds it, and deploys it behind HTTPS. It replaces manual Dockerfile, YAML, and cloud-console setup with an analysis step that shows the files supporting its conclusions.
Developers can deploy from GitHub, a local folder, the API, or supported coding-agent workflows. The result includes a live URL, deployment history, logs, and health checks, with PostgreSQL, encrypted secrets, and S3-compatible storage available for supported application needs.