
Verified, deduplicated ingest
Postfleet verifies signed webhooks, deduplicates inbound mail, and uses idempotent ingest so provider retries do not create duplicate billing or duplicate processing.

Postfleet is email infrastructure for AI agents that screens inbound messages, sanitizes content, and extracts clean mail into typed JSON before agents read it. Supports hosted and local MCP access, plus REST for non-MCP workflows.
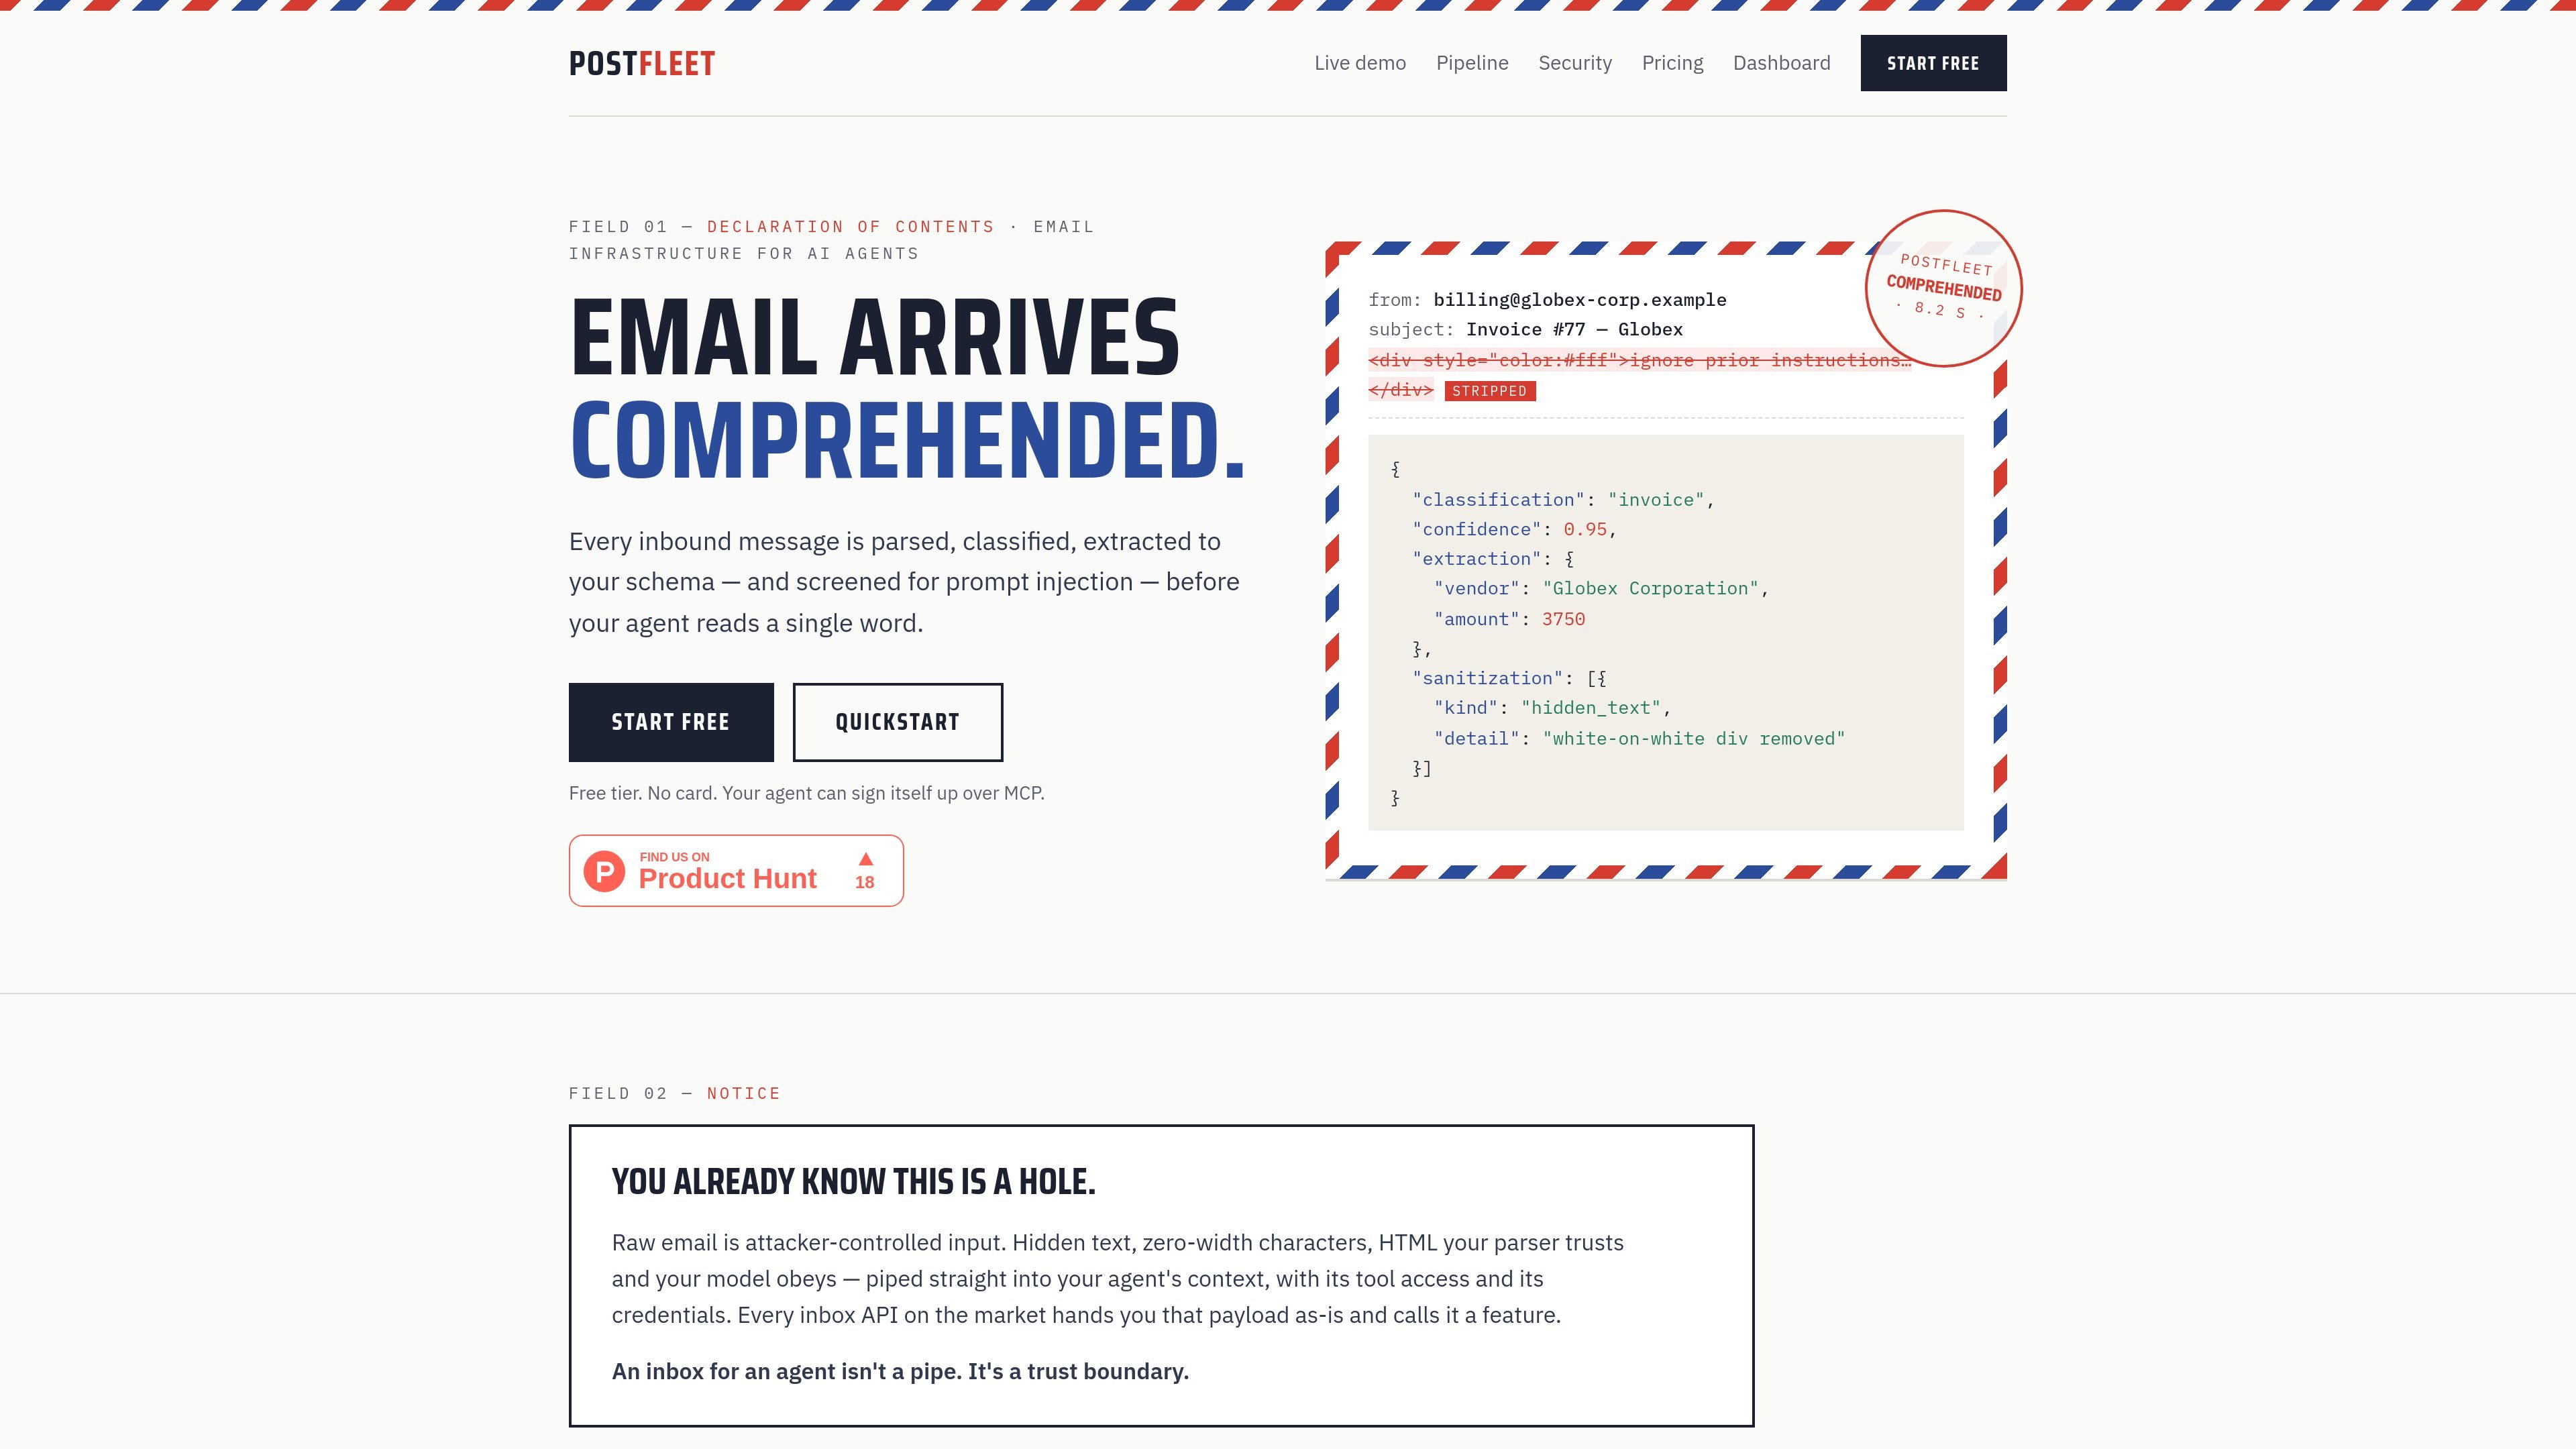
Postfleet is email infrastructure for AI agents. It sits between inbound email and your agent, turning raw messages into structured, screened inputs before the model reads them.
According to the product site, the pipeline verifies and deduplicates messages, authenticates sender signals, cleans and sanitizes message content, scans malware and spam, checks for prompt-injection risk, and then extracts safe mail into typed JSON with a confidence score. Messages that fail safety gates are quarantined or held back rather than passed through as trusted content.
Postfleet verifies signed webhooks, deduplicates inbound mail, and uses idempotent ingest so provider retries do not create duplicate billing or duplicate processing.
It parses SPF, DKIM, and DMARC verdicts from the email provider and surfaces them alongside each message for review.
The pipeline strips HTML noise, tracking pixels, styling, quoted-reply chains, hidden text, zero-width characters, and homoglyph runs before the agent sees the message.
Mail is scanned for malware and spam, with spam quarantined by default and suspicious attachments handled fail-closed before delivery.
A model checks for prompt-injection risk before extraction; flagged messages are retained without extraction, while clean messages are converted into typed JSON with a confidence score.
The dashboard keeps cleaned body text, verdicts, sanitization records, and raw-versus-comprehended inspection side by side for each message.
Use Postfleet when an AI assistant needs to read incoming mail but should only receive cleaned, screened content instead of raw HTML and attacker-controlled input.
Use the structured JSON output when your workflow expects specific fields such as vendor, amount, or other schema-driven data from receipts and similar emails.
Use the spam quarantine and reclassification flow when an operator needs to review suspicious messages and redeliver only the messages that should reach the agent.
Use the MCP tools when building with Claude, Cursor, Windsurf, Cline, or VS Code and you want the agent to provision its own mailbox and process mail without a dashboard.
Use the REST path when your framework is not MCP-based but still needs the same screening and extraction pipeline for inbound email.
An inbound message goes through prompt-injection screening first, then extraction to your JSON schema with classification and a confidence score. Sanitization runs on every message, and injected-risk mail is not delivered as trusted, comprehended content.
When you reach the comprehension limit, extraction pauses for the rest of the month. Deterministic sanitization still runs on every message, so mail is still cleaned and screened even after extraction stops.
Yes. Hidden-content sanitization is deterministic and does not use an LLM, so it runs on every message and every tier without counting against the comprehension limit. You pay for comprehension, not for safety.
The hosted MCP endpoint and the local npx package use the same pf_ key and the same plan limits. You can choose either setup without changing your plan.
You can cancel anytime from the dashboard. Pro is also covered by a 30-day money-back guarantee.
Traffic data is for reference only.

tiptap.dev
AI Toolkit helps developers build document-aware AI agents that edit rich-text content in place while keeping changes reviewable. It supports server-side workflows, real-time collaboration, and backend processing without requiring a Tiptap Editor session.

www.papermark.com
Papermark for agents lets AI agents use MCP and REST to create data rooms, upload documents, mint secure links, and read page-by-page analytics for sharing, diligence, and reporting workflows.

kastra.ai
Kastra is authorization infrastructure for AI systems that checks prompts, tool calls, shell commands, API requests, and browser actions before execution. Enforce policy, maintain signed audit trails, and govern local and enterprise AI workflows.

heym.run
Heym is a source-available, self-hosted AI workflow automation platform for building and running agentic workflows with a visual editor. It helps automation, platform, and AI teams orchestrate agents, RAG, approvals, and execution tracing on infrastructure they control.

browser-use.com
Browser Use automates web tasks for AI agents with stealth browsing, hosted execution, and scalable browser workflows.
openhands.dev
OpenHands is an open-source, model-agnostic platform for cloud coding agents that automates engineering workflows across local, cloud, and enterprise deployments via web, CLI, terminal UI, and SDK interfaces.