
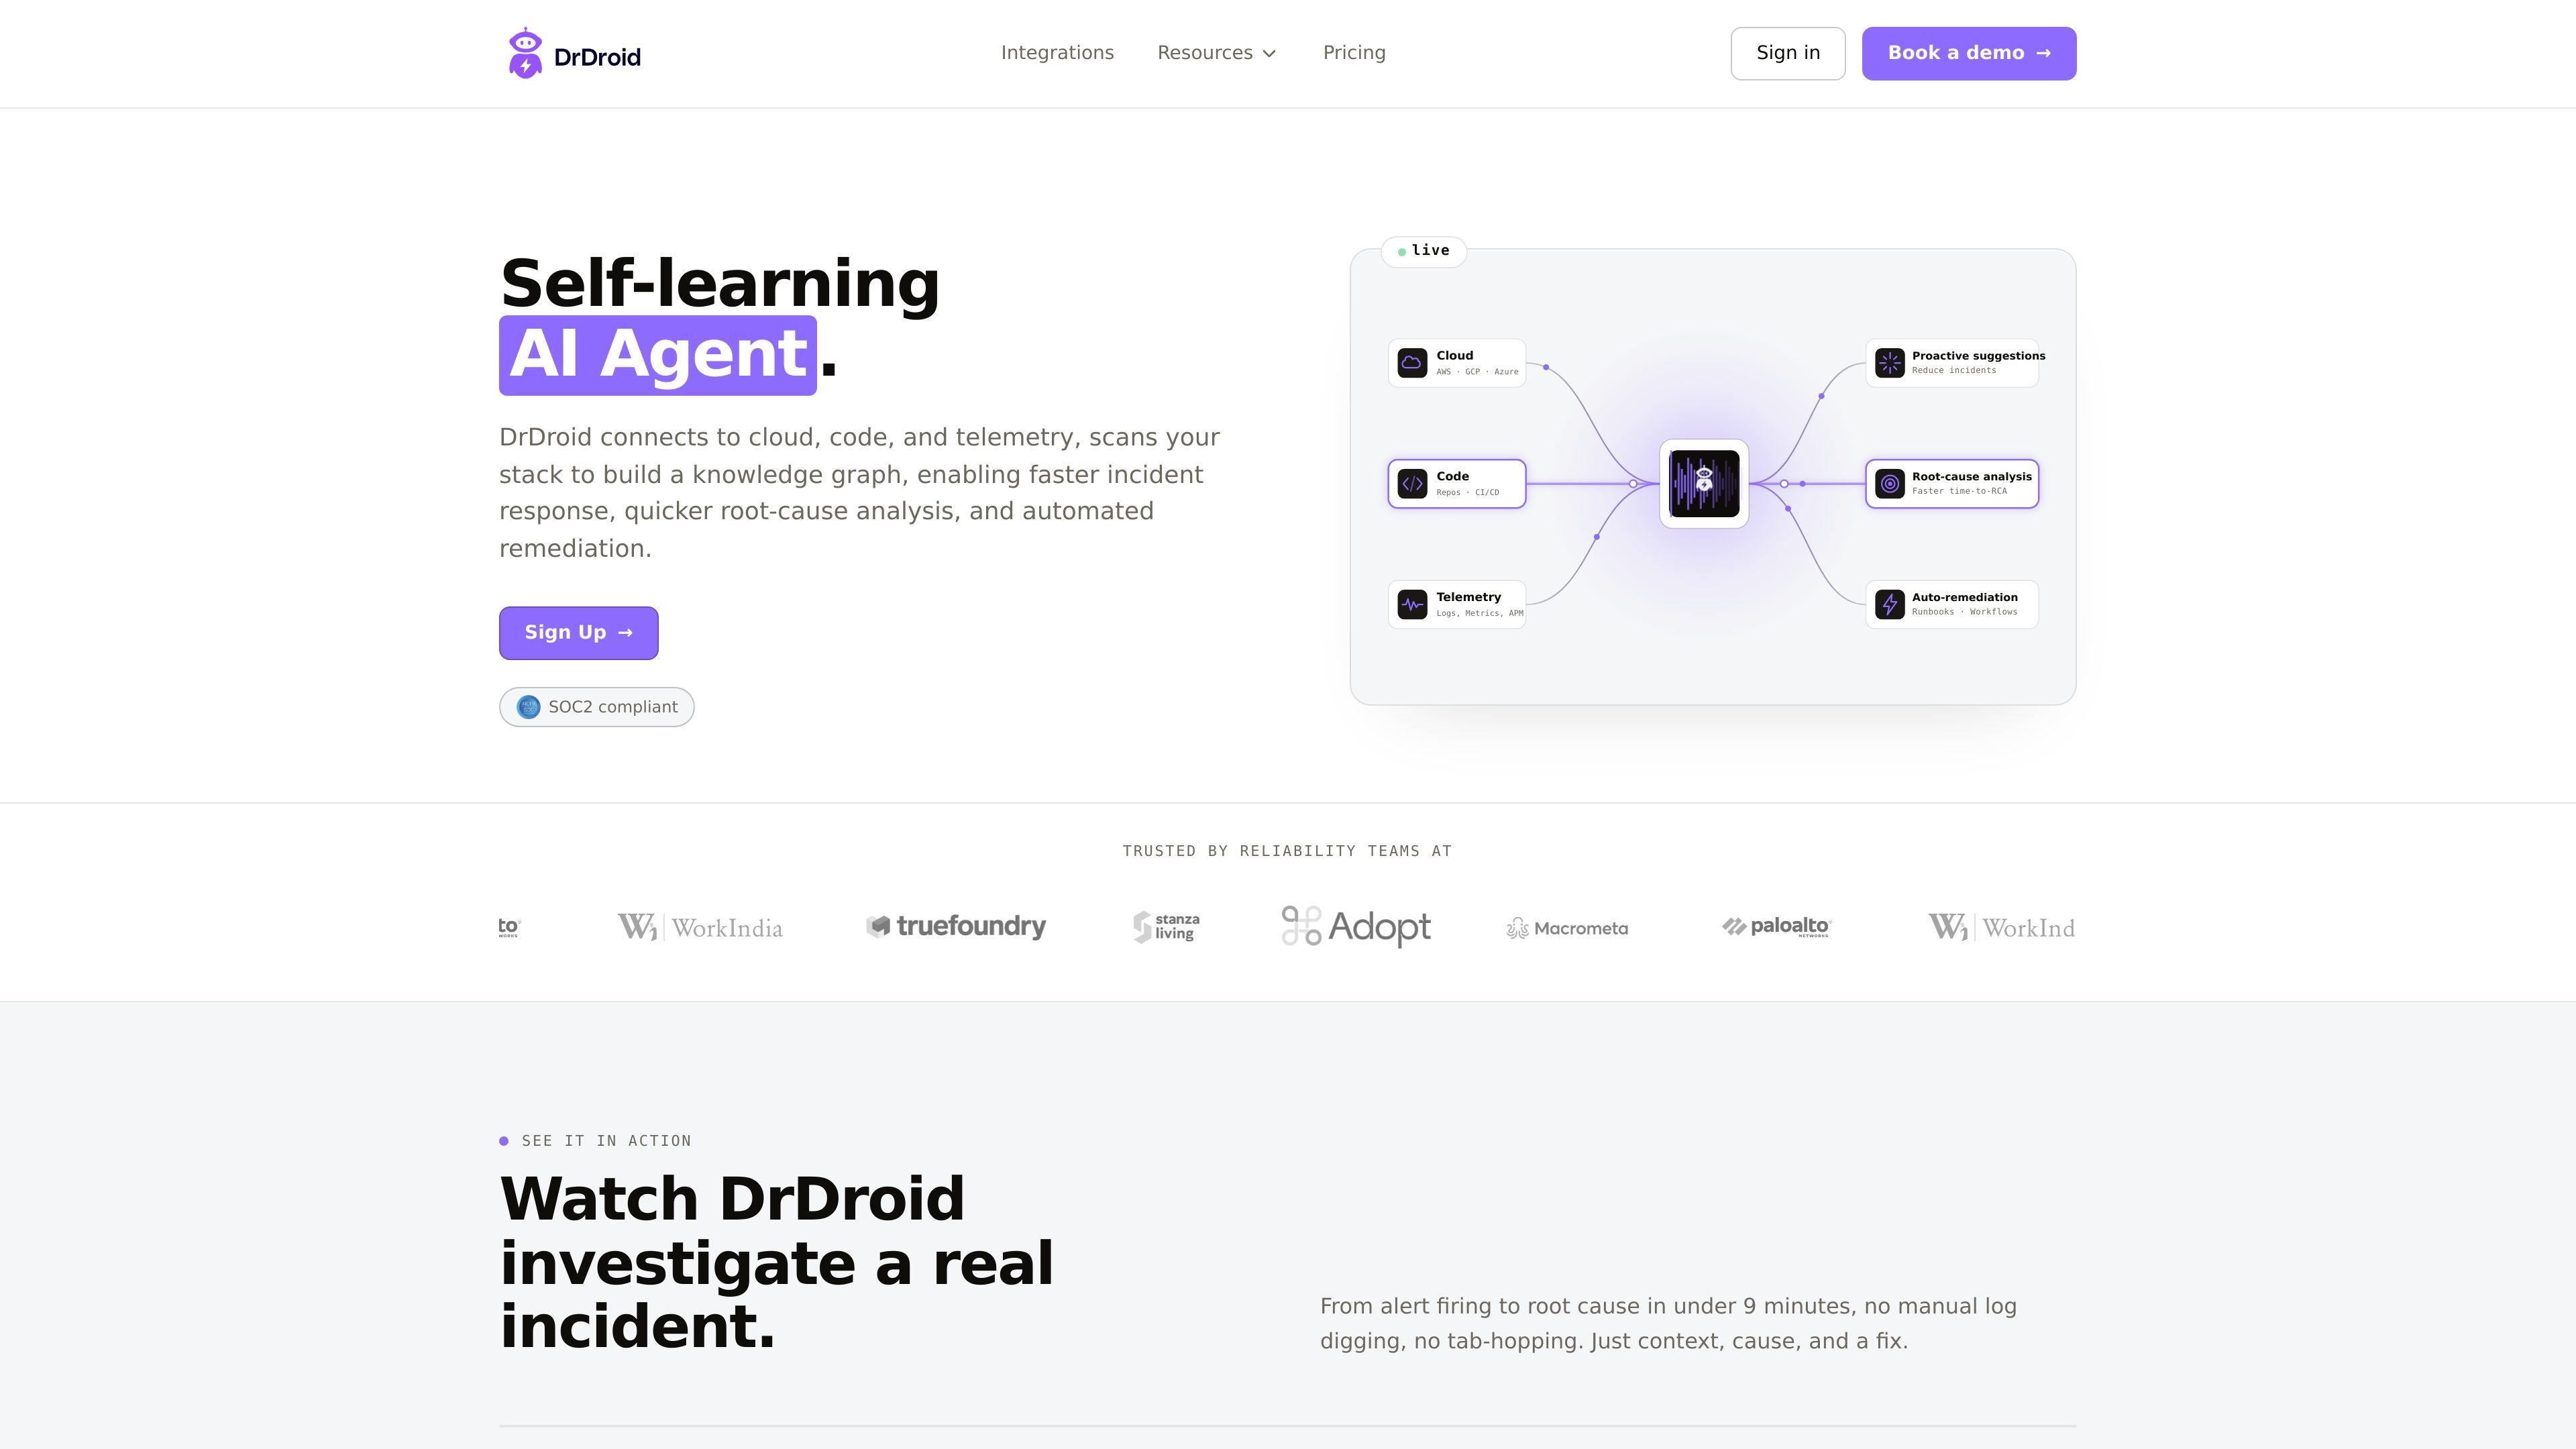
Connect and map the stack
DrDroid connects to cloud, code, CI/CD, and observability tools, then crawls telemetry and related context to build a knowledge graph of the stack.

AI SRE agent connecting tools for incident response and remediation
DrDroid is an AI SRE agent for incident response and reliability work. It connects to cloud, code, CI/CD, and telemetry systems, then scans the stack to build a knowledge graph that helps teams investigate alerts, identify root cause, and act on runbooks or remediation workflows with more context.
The product is positioned for both individual troubleshooting and team operations. The site emphasizes read-only connections, no code changes, and live setup through existing tools, while the pricing page highlights shared investigations, unlimited users, and enterprise options such as self-hosting, SSO/SCIM, and bring-your-own-LLM.
DrDroid connects to cloud, code, CI/CD, and observability tools, then crawls telemetry and related context to build a knowledge graph of the stack.
The graph links entities such as repositories, services, dashboards, pods, infrastructure, alerts, incidents, and runbooks so investigations can follow cross-tool relationships.
When an alert fires, the system uses the graph to trace blast radius, surface likely causes, and support faster root-cause analysis without manual tab-hopping.
The product can surface proactive suggestions and runbook-based actions, including guarded automation for remediation workflows.
A self-learning agent stores correct queries, correlations, tool sequences, and dead-end paths so later investigations can skip repeated mistakes and move faster.
Pricing and plan controls support shared investigations, audit trails, unlimited users, and enterprise deployment options such as self-hosting in a VPC and bring-your-own-LLM.
Use DrDroid when an alert fires and engineers need to move from signal to likely cause without manually checking multiple dashboards, repos, and chat threads.
Use the knowledge graph and pattern memory to narrow down recurring failures, blast radius, and the most relevant evidence for a root-cause analysis.
Use the self-learning behavior to capture corrected queries, tool sequences, and known correlations so repeated incidents are investigated faster over time.
Use shared investigations, audit trails, and unlimited users to standardize how on-call teammates collaborate during incidents and handoffs.
Use enterprise controls such as self-hosting, SSO/SCIM, and bring-your-own-LLM when security, residency, or infrastructure constraints require tighter deployment control.
DrDroid is designed to connect to cloud, code, and telemetry sources, crawl the stack, and build a knowledge graph that helps investigate incidents and trigger remediation or runbooks with more context.
The source describes read-only OAuth connections into cloud, code, CI/CD, and observability tools, with no agents and no code changes, and says teams can be live in about 30 minutes for the core connection workflow.
The Teams plan is aimed at shared on-call rotation and team collaboration, while the site also notes a Mac app for individual use and Teams for shared investigations and centralized integrations.
Pricing is based on investigation credits rather than seats. The Teams plan includes 99 credits per month, shared across unlimited users, with top-ups available at $1 per credit; Enterprise uses custom pricing.
The site positions DrDroid around incident response, root-cause analysis, proactive suggestions, and automated remediation. The exact depth of automation depends on the connected tools, signals, and runbooks in a given stack.
Traffic data is for reference only.

middleware.io
Full-stack observability for logs, metrics, traces, apps, infrastructure, and user experience, with OpsAI for AI-powered issue detection and remediation.

canyontechs.ai
CanyonTechs AI is an LLM-powered auto-remediation product that parses production logs, detects incidents, and delivers fixes as signed pull requests. It offers a workspace-based service with sign-up and login for individual and company users.

mezmo.com
AI-driven telemetry platform for filtering, routing, and analyzing logs, metrics, and traces
www.coldtea.ai
Coldtea is an AI-powered software delivery environment for teams that want to manage QA, production monitoring, bug detection, task creation, and fixes in one place. It runs on your machine to catch regressions and production issues after code is written.

rootly.com
AI-native incident management for engineering teams
coisland.app
CoIsland is a native macOS monitoring app that brings alerts from code, deploys, data tools, tickets, mail, and on-call services into the Mac's notch. Engineers can schedule tool-specific queries, review matching items, and hand an alert's context to Claude Code, Codex, or Cortex Code while retaining approval control.