
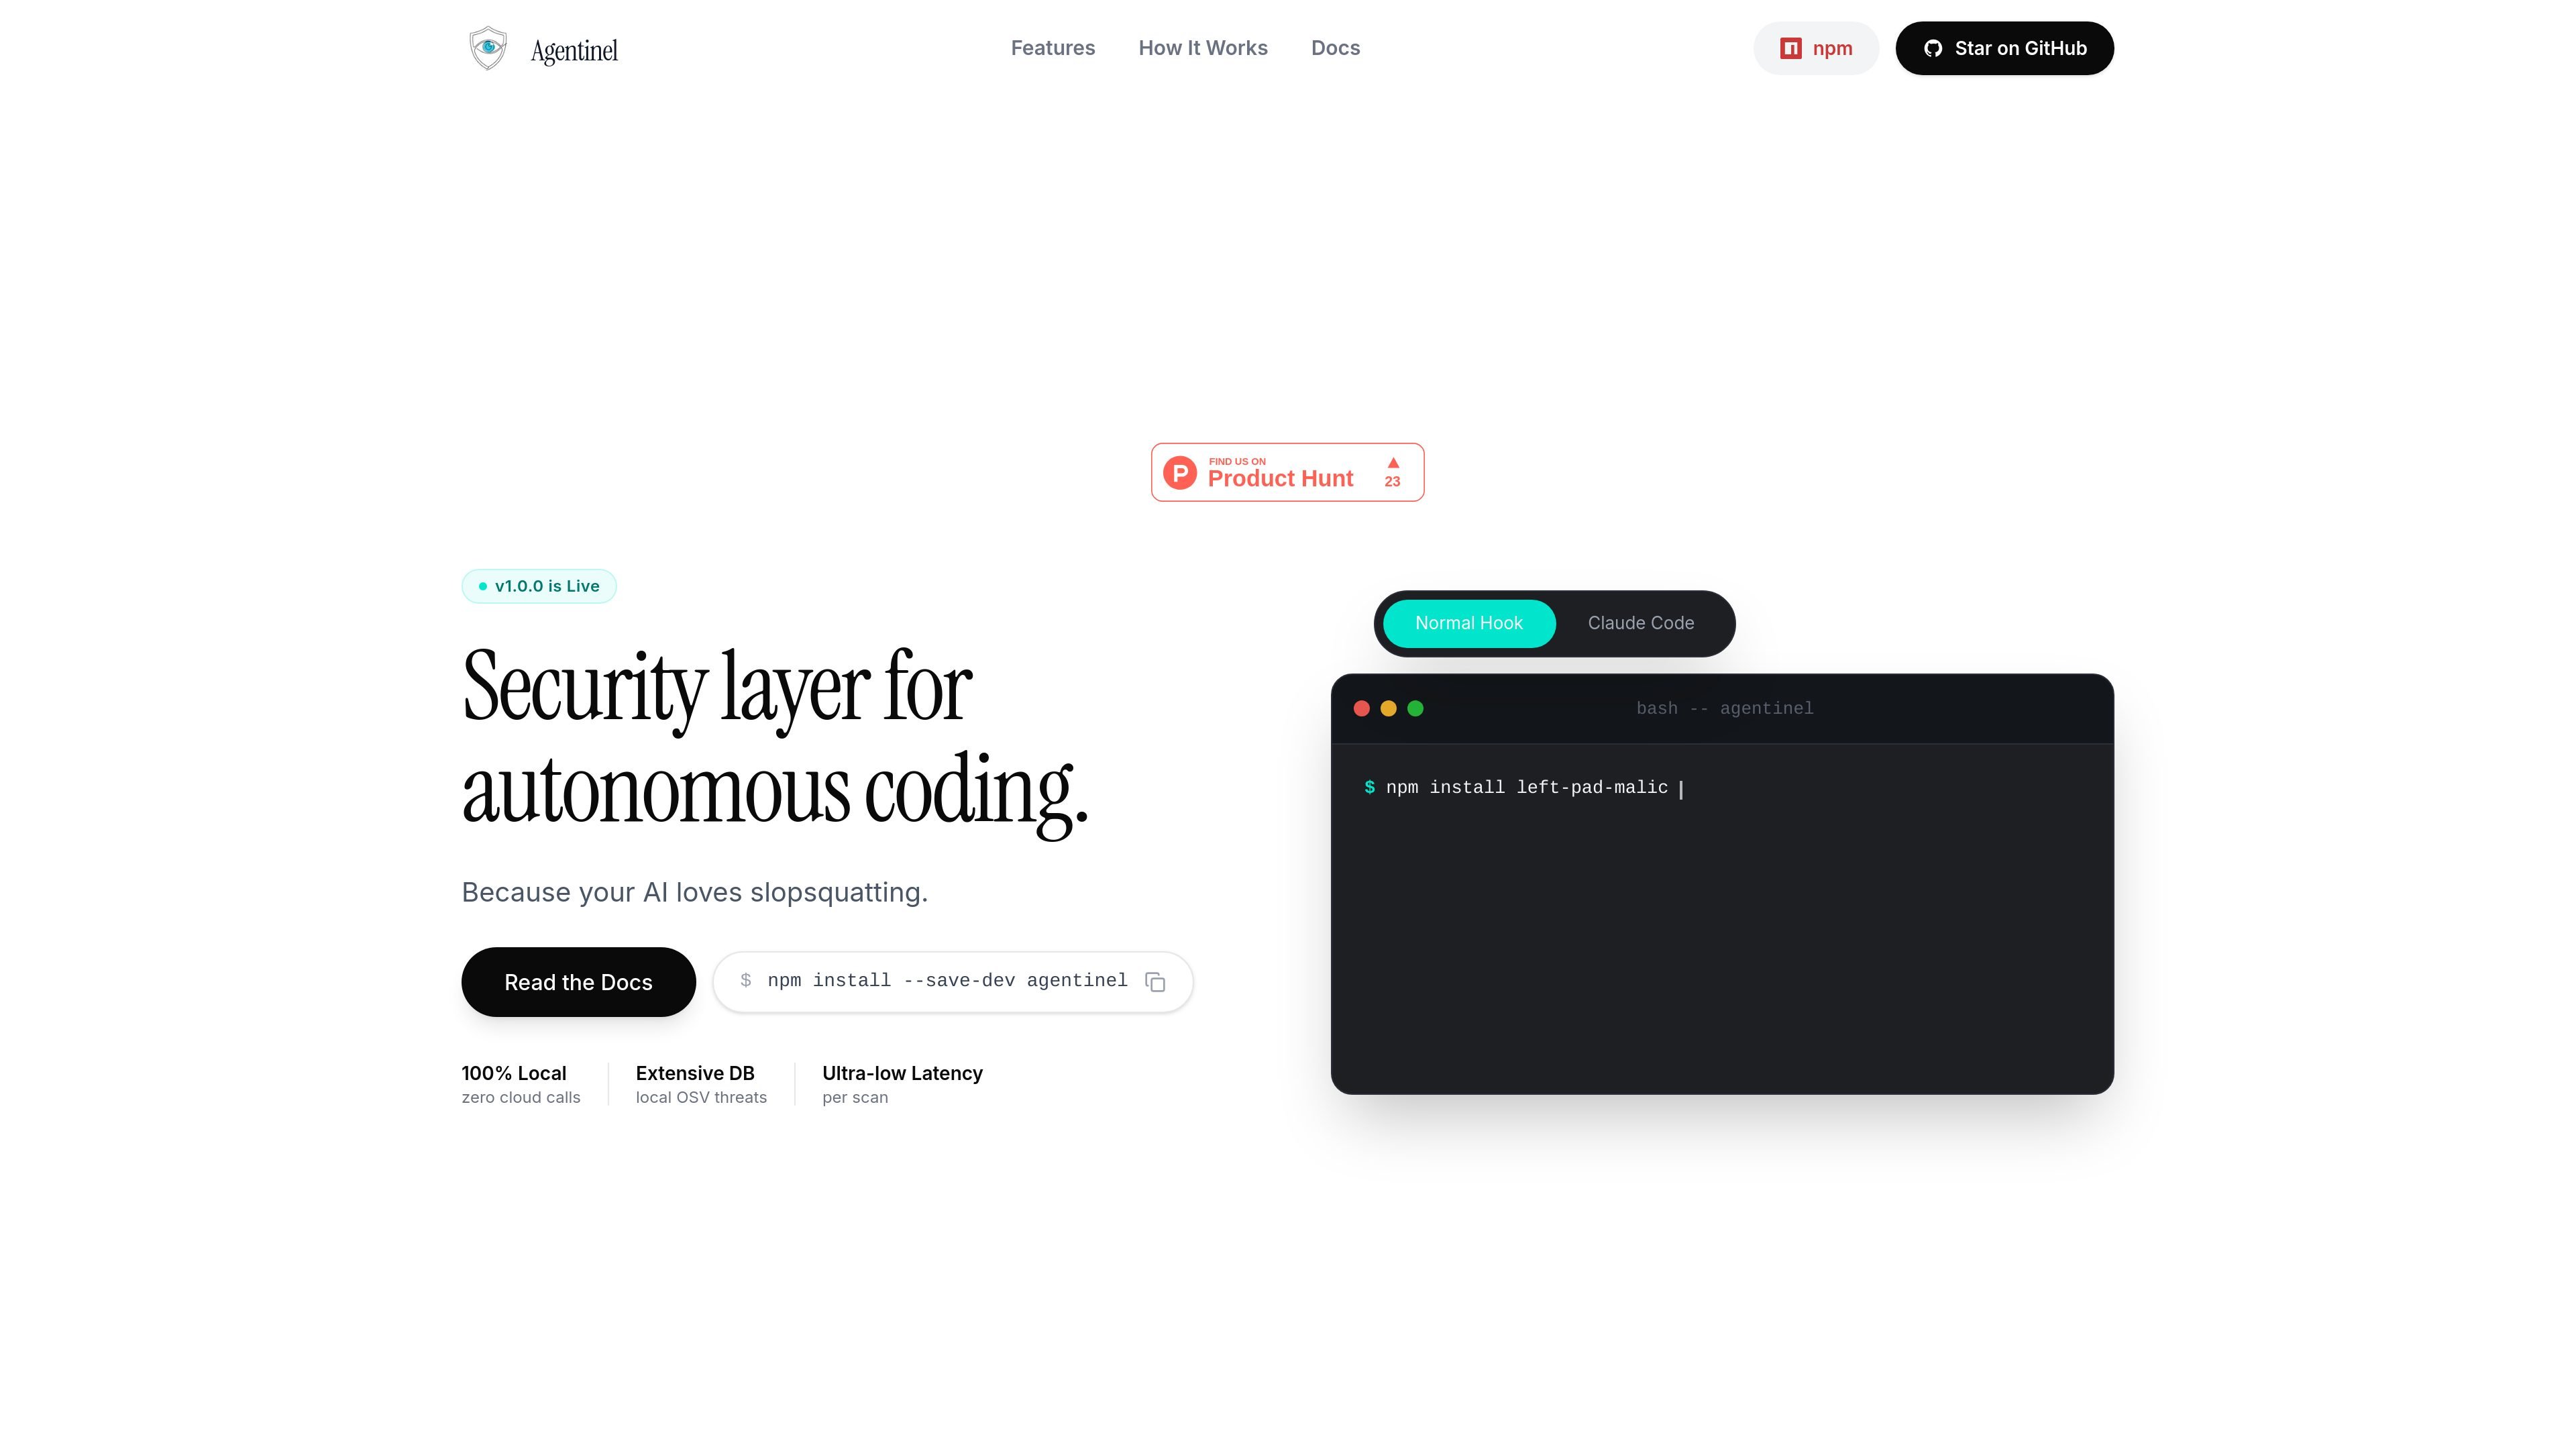
Intercepts install requests before they run
Agentinel registers as a PreToolUse-style hook so the agent's proposed shell command is checked before execution.

Agentinel è un livello di sicurezza locale per agenti di coding autonomi: verifica le richieste di installazione prima dell’esecuzione e blocca i pacchetti npm sospetti usando un database OSV offline ed euristiche, senza chiamate al cloud.
Agentinel is a locally run security guardrail for autonomous coding workflows. It sits between an AI coding agent and the package manager so install commands can be checked before npm runs them, helping catch hallucinated or malicious package names in agent-driven development.
The product is aimed at developers using tools such as Claude Code, GitHub Copilot CLI, OpenAI Codex CLI, or Gemini CLI. According to the site, it runs entirely on-device, uses a bundled OSV database plus heuristic checks, and returns a structured reason to the agent when a package is blocked.
Agentinel registers as a PreToolUse-style hook so the agent's proposed shell command is checked before execution.
It checks the requested package against a bundled local copy of the OSV database and heuristic rules for slopsquatting and hallucinated package names.
When a package is blocked, the tool returns a structured JSON payload to the agent so it can understand what failed and why.
The docs describe a fail-open design: if scanning cannot complete because of an internal error, the install is allowed to proceed with a warning.
All checks run on-device with no network calls at scan time, which keeps package names and scan activity local to the machine.
The site says it can scan dependency trees and also act as a gate in CI or CD workflows by checking manifests before deployment.
Use Agentinel when an AI coding assistant proposes an npm install command and you want to stop hallucinated or slopsquatted package names before they reach disk.
Use it in local development when you want package checks to happen without sending telemetry or scan data to a cloud service.
Use it with autonomous CLI agents so blocked installs are explained back to the model and it can try a safer command automatically.
Use the local scan and manifest checks in CI/CD pipelines to gate builds or deployments before a risky package is introduced.
Agentinel is installed as a local package and sits between an AI coding agent and the package manager. The docs describe it as zero-config and run entirely on-device, with no account, API key, or network calls required at scan time.
It intercepts package-install decisions from autonomous coding agents before npm executes them. The docs mention support for agent runtimes such as Claude Code, GitHub Copilot CLI, OpenAI Codex CLI, and Gemini CLI, using their hook or pre-execution events.
When a package is flagged, Agentinel blocks it, logs the reason, and returns a structured payload back to the agent so the agent can adjust its next action. The homepage also describes warn mode and strict mode behavior.
Agentinel is designed to fail open. If it cannot scan because of an internal error or a corrupted database, it allows the install to proceed and logs a warning instead of silently breaking the workflow.
The documentation describes Agentinel as a local security guardrail for AI coding agents rather than a team management platform. The source does not describe shared dashboards, accounts, or centralized policy management.
I dati sul traffico sono solo a scopo di riferimento.

kastra.ai
Kastra è un’infrastruttura di autorizzazione per sistemi di IA che verifica prompt, chiamate agli strumenti, comandi shell, richieste API e azioni del browser prima dell’esecuzione. Aiuta i team ad applicare le policy, mantenere audit trail firmati e governare i workflow di IA locali ed enterprise.

www.phinq.co
Phinq è un livello open source di governance a runtime per agenti AI. Intercetta le chiamate agli strumenti, le classifica in base al rischio e mette in pausa le azioni più rischiose per ottenere l’approvazione umana prima dell’esecuzione.

panguard.ai
Panguard AI è una piattaforma di sicurezza open source per agenti AI che analizza skill e server MCP prima dell’esecuzione e protegge le azioni degli agenti a runtime, offrendo controlli self-hosted e prove di conformità firmate a sviluppatori, fornitori AI e team soggetti a regolamentazione.

postfleet.ai
Postfleet è un’infrastruttura email per agenti AI che filtra i messaggi in arrivo, ne sanifica il contenuto ed estrae email pulite in JSON tipizzato prima che l’agente le legga. Supporta MCP in hosting e locale, oltre a REST per flussi senza MCP.

voidleap.com
Voidleap Code è un IDE desktop per sviluppatori professionisti e ingegneri AI che creano software con agenti AI. Funziona in locale su Mac e Windows, supporta account di provider cloud o modelli locali e consente di esaminare e controllare prompt, chiamate agli strumenti, contesto e modifiche ai file.
cekura.ai
Cekura è una piattaforma di valutazione vocale e osservabilità per i team che sviluppano agenti vocali AI. Consente di simulare chiamate prima del lancio, monitorare le conversazioni in tempo reale e analizzare gli indicatori di qualità nei flussi di lavoro in produzione.