
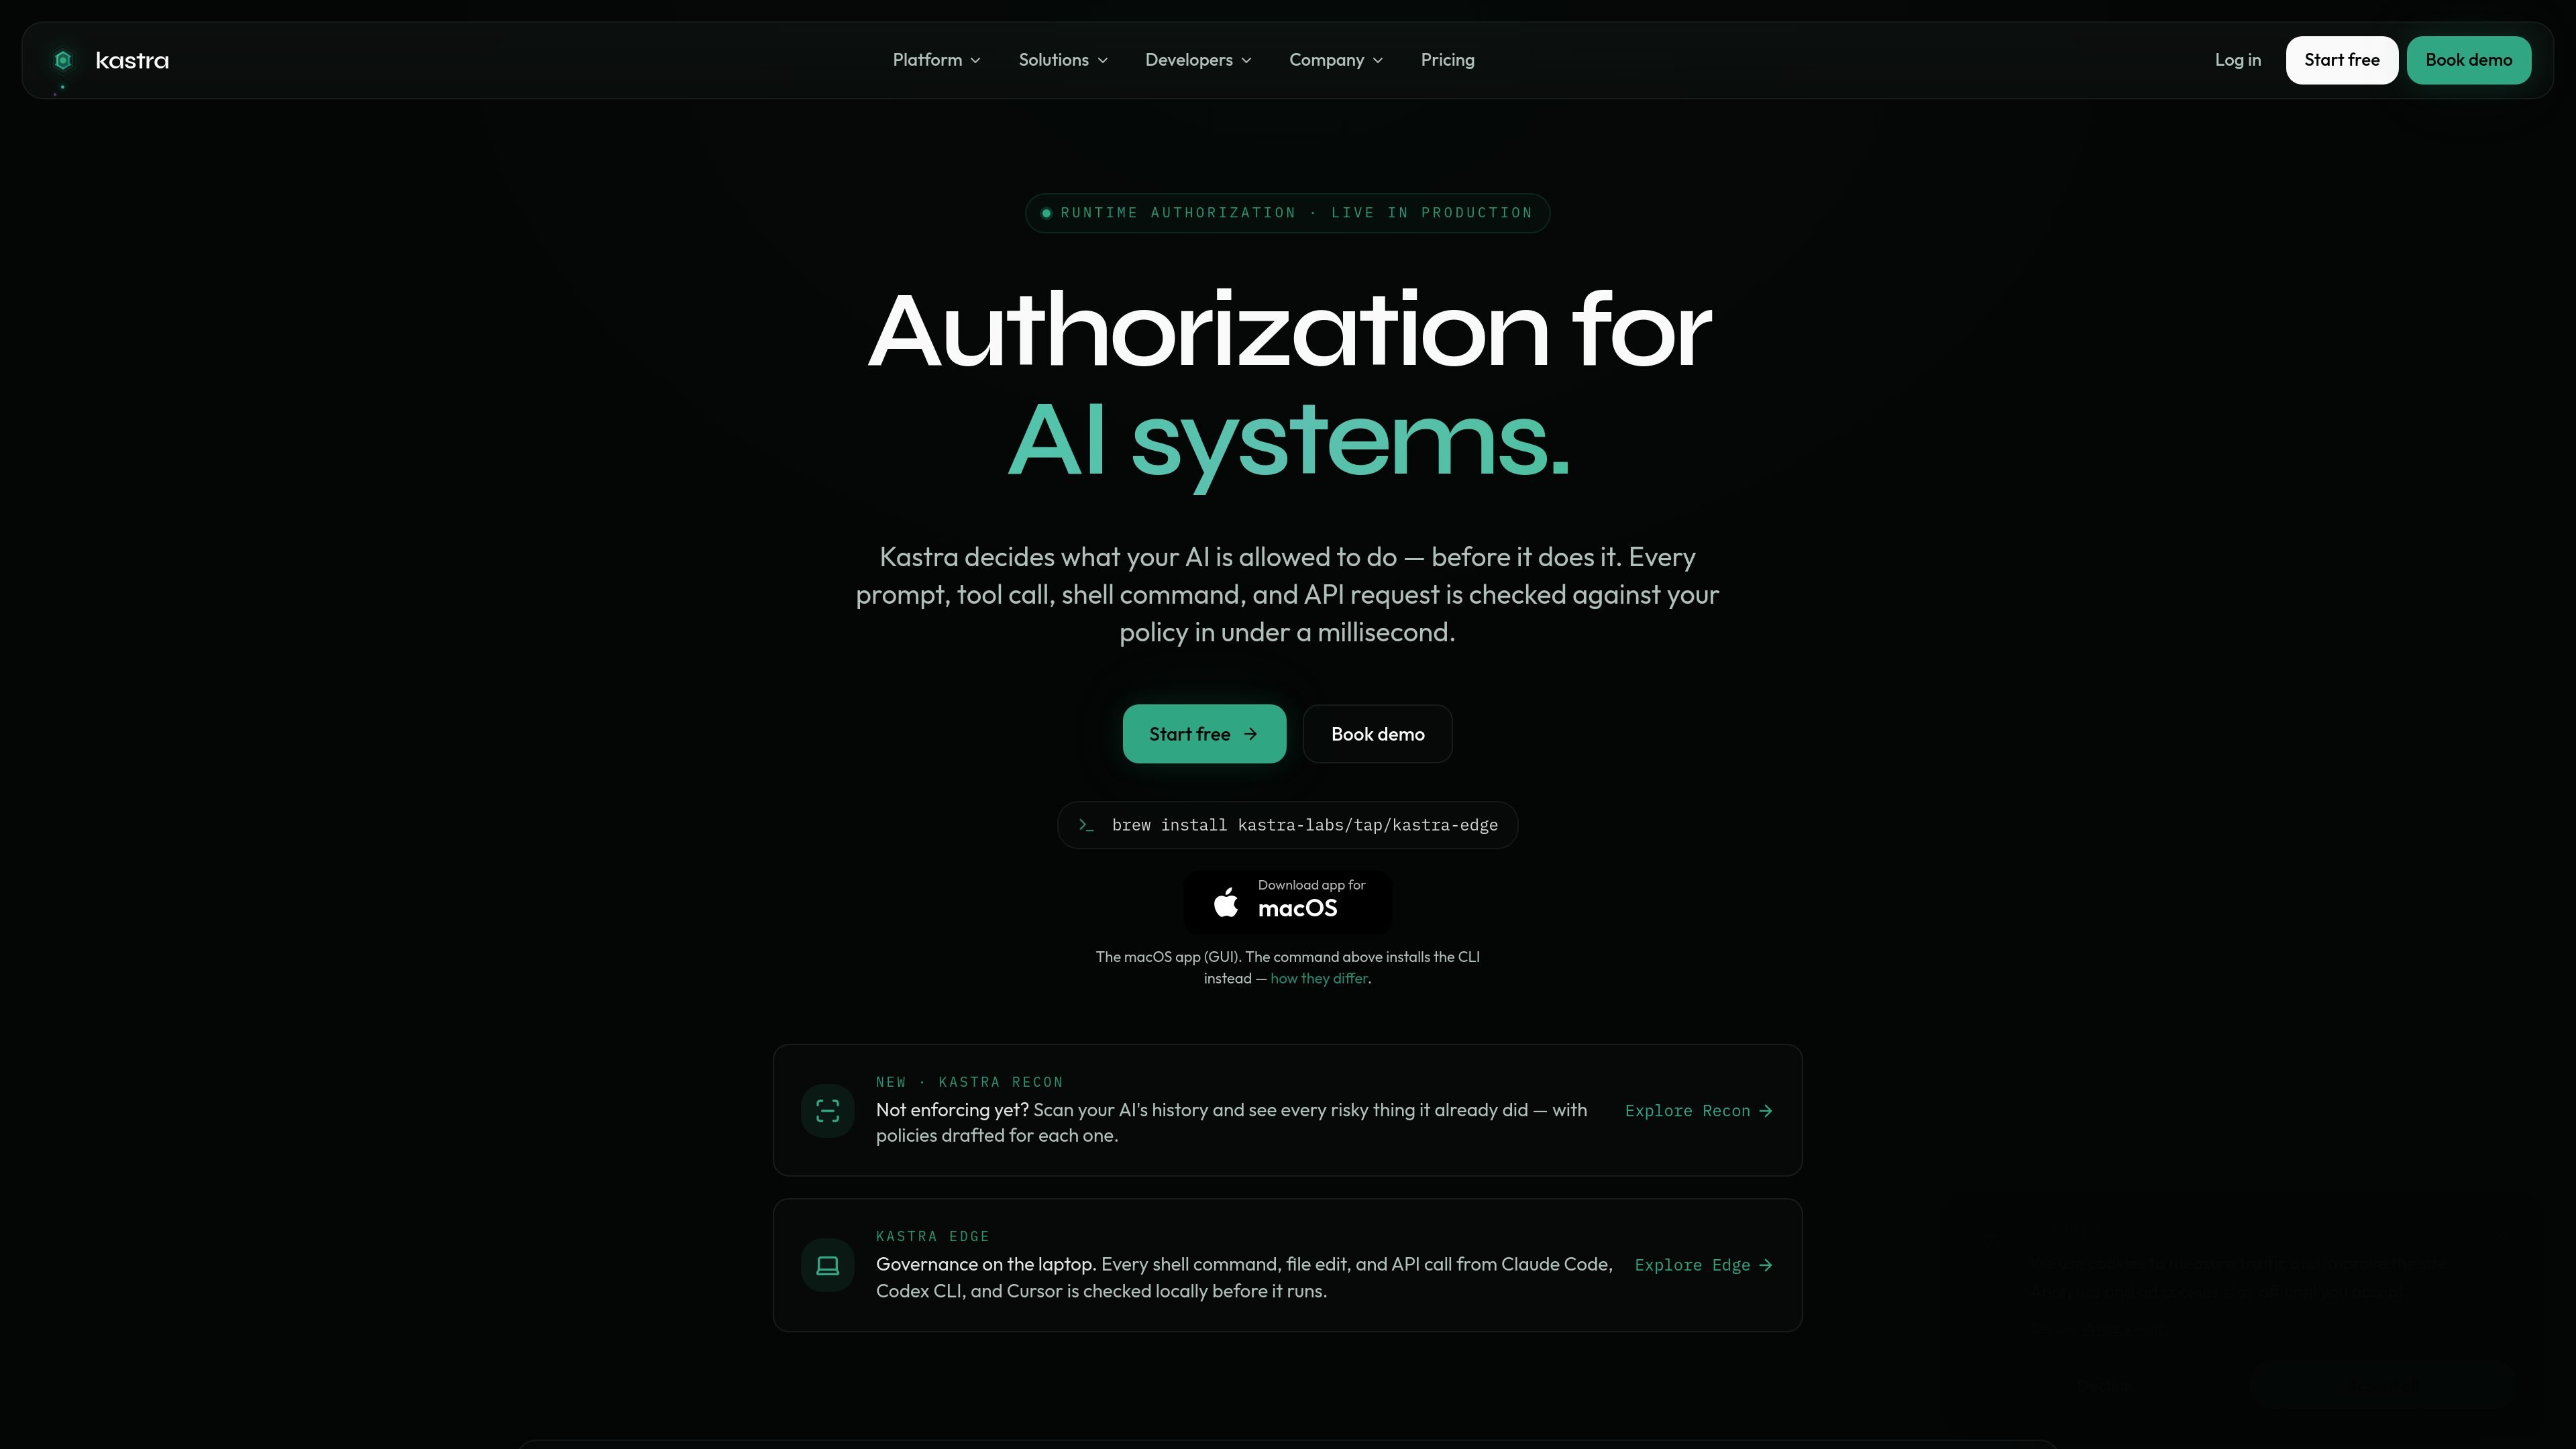
Runtime authorization at the action boundary
Checks prompts, tool calls, shell commands, and API requests before execution, with the site describing sub-millisecond decision latency.

Kastra è un’infrastruttura di autorizzazione per sistemi di IA che verifica prompt, chiamate agli strumenti, comandi shell, richieste API e azioni del browser prima dell’esecuzione. Aiuta i team ad applicare le policy, mantenere audit trail firmati e governare i workflow di IA locali ed enterprise.
Kastra is authorization infrastructure for AI systems. Its main job is to decide what an AI is allowed to do before the action runs, rather than recording or analyzing behavior after the fact.
The product checks prompts, tool calls, shell commands, API requests, and browser actions against policy in under a millisecond. The same policy layer can be used across local coding agents, autonomous workflows, and enterprise deployments, with deployment options that include cloud, self-hosted, and air-gapped environments.
Checks prompts, tool calls, shell commands, and API requests before execution, with the site describing sub-millisecond decision latency.
Lets teams write policies in Kastra Policy Language, a typed DSL that lives in git, is reviewed in pull requests, and can be tested against fixtures.
Supports allow, deny, redact, and escalate or approval-based outcomes depending on the policy and surface being evaluated.
Runs enforcement on developer laptops, browser agents, backend services, and other AI surfaces using the same policy model.
Produces signed, append-only audit traces that can be replayed and exported to SIEM tools such as Datadog, Splunk, and S3.
Includes Kastra Recon, which scans historical agent activity, surfaces risky actions already taken, and drafts policies for them.
Use Kastra on a developer laptop to gate destructive commands, file edits, and local API calls from coding assistants before they run.
Apply the same policy layer to autonomous agent workflows so each step is checked and sensitive steps can require human approval.
Govern browser-based agents by intercepting clicks, navigation, form fills, and downloads before they fire in the DOM.
Review historical agent activity with Recon to find risky actions already taken and draft policies before turning on enforcement.
Run authorization in enterprise environments where teams want signed evidence, audit exports, and deployment models that include self-hosted or air-gapped setups.
Kastra is positioned as authorization infrastructure for AI systems. It sits in the path of prompts, tool calls, shell commands, API requests, browser actions, and other AI-generated actions, then allows, denies, or in some cases requires approval before the action runs.
The source describes deployment models including cloud, self-hosted, and air-gapped. The pricing page also says Enterprise can run in self-hosted, BYOC, or air-gapped environments.
Kastra’s pricing page lists support for Claude Code, Codex CLI, Cursor, OpenClaw, and any OpenAI-compatible runtime, plus custom agents through SDKs.
Yes. The pricing page includes Shadow Mode for observing activity before enforcement, and the policy-engine page describes replaying historical actions against policy versions to see what would have changed.
The site says decisions and audit records can be streamed to SIEM destinations including Datadog, Splunk, and S3. The policy-engine page also notes first-party SDKs for TypeScript, Python, Go, Rust, Java, and Swift.
I dati sul traffico sono solo a scopo di riferimento.
| apr | 0 |
|---|---|
| mag | 0 |
| giu | 2782 |

www.phinq.co
Phinq è un livello open source di governance a runtime per agenti AI. Intercetta le chiamate agli strumenti, le classifica in base al rischio e mette in pausa le azioni più rischiose per ottenere l’approvazione umana prima dell’esecuzione.
arcade.dev
Arcade è un runtime MCP per agenti AI in produzione che combina autorizzazione degli agenti, strumenti affidabili e governance. Aiuta i team a collegare gli agenti ai sistemi reali, con opzioni di deployment flessibili e piani tariffari dal gratuito all’enterprise.

agentinel.habitwala.in
Agentinel è un livello di sicurezza locale per agenti di coding autonomi: verifica le richieste di installazione prima dell’esecuzione e blocca i pacchetti npm sospetti usando un database OSV offline ed euristiche, senza chiamate al cloud.

panguard.ai
Panguard AI è una piattaforma di sicurezza open source per agenti AI che analizza skill e server MCP prima dell’esecuzione e protegge le azioni degli agenti a runtime, offrendo controlli self-hosted e prove di conformità firmate a sviluppatori, fornitori AI e team soggetti a regolamentazione.

caveman.so
Caveman è uno stack per l’efficienza dei token destinato agli agenti AI e ai flussi di lavoro in produzione. Aiuta i team a ridurre il contesto idoneo, instradare il traffico e misurare i risparmi verificati tramite strumenti locali, un SDK TypeScript e un livello cloud gestito.

mino.ai
TinyFish è una piattaforma enterprise per agenti web AI che combina ricerca in tempo reale, recupero delle pagine, automazione del browser e workflow a più passaggi. Aiuta i team a lavorare su larga scala con siti dinamici o autenticati.