
Native n8n workflow node
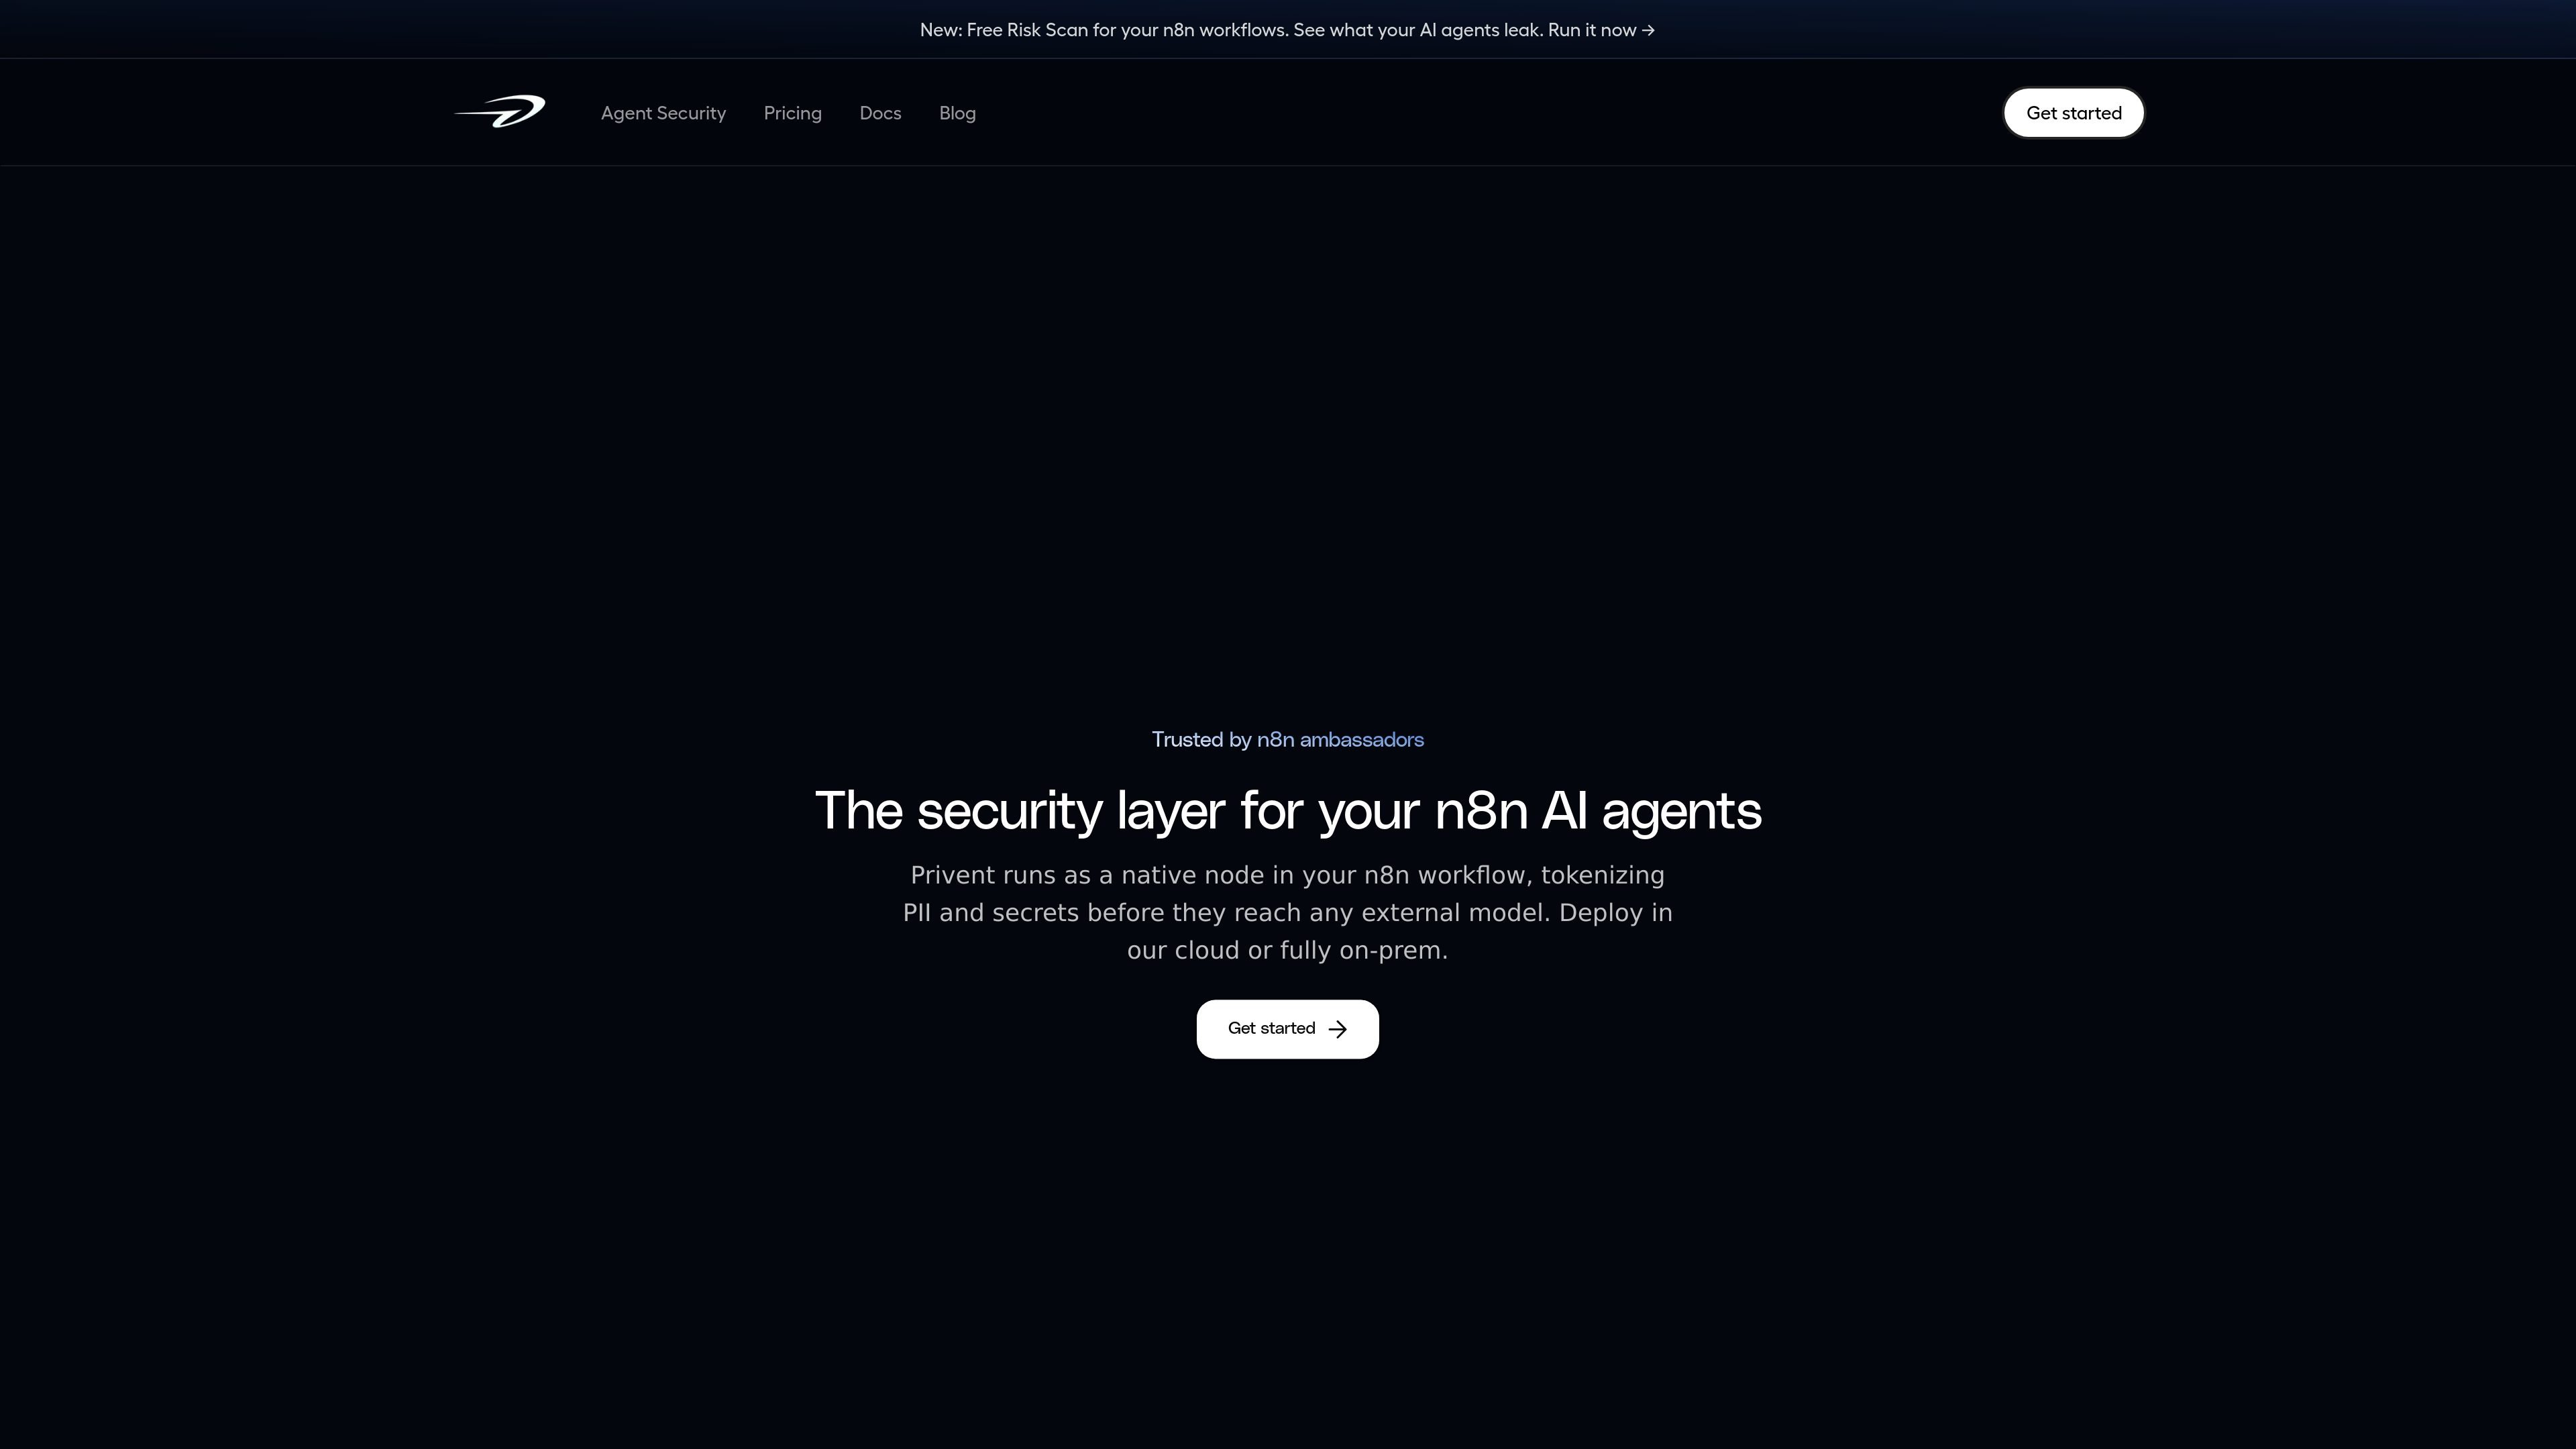
Privent runs as a native n8n node inside the workflow canvas, so security checks happen between steps rather than around the agent. The product is positioned as a drop-in addition with no proxy or rewrites.
Privent est une couche de sécurité à l’exécution pour l’IA agentique, notamment les workflows n8n. Elle masque les données sensibles avant leur transmission aux modèles externes, conserve une trace des décisions de risque et surveille l’usage organisationnel de ChatGPT, Claude et Gemini.
Privent is a runtime security layer for agentic AI, with a particular focus on n8n workflows. It embeds as a native node in the workflow so sensitive data can be detected, masked, and restored at trusted destinations before it reaches external models.
The product is built around two related workflows: Agent Security for protecting data moving through n8n agent flows, and AI Monitoring for observing AI usage across an organization. The site says Privent can run in Privent Cloud, a dedicated environment, or fully on-prem/private cloud, including deployments where the full stack and ML inference stay inside the customer network.
Privent runs as a native n8n node inside the workflow canvas, so security checks happen between steps rather than around the agent. The product is positioned as a drop-in addition with no proxy or rewrites.
The ACARS engine scores data in the context of the whole agent session, using signals such as entity sensitivity, semantic risk, contextual amplification, destination risk, behavioral velocity, and policy overrides.
The APE engine can mask, swap, or route sensitive data based on risk level. Supported responses include tokenization and re-injection, semantic substitution, noise injection, org identity decoupling, structural decomposition, and risk-conditioned routing.
Privent’s n8n package includes Session, Tokenize, Detokenize, Handoff, and Audit Event nodes, along with a credential type. The docs say tokenization handles kinds such as EMAIL, SSN, CREDIT_CARD, IBAN, AWS_KEY, JWT, and API_KEY.
The product supports multiple deployment modes, including Privent Cloud, a dedicated environment, and fully on-prem / private cloud deployment. The docs also describe a self-hosted n8n setup and cloud-based monitoring extension deployment.
The monitoring docs say Privent can be rolled out to browser environments via MDM and can surface detection events in the dashboard in real time. The site also mentions AI Monitoring for organization-wide usage with ChatGPT, Claude, and Gemini.
Teams using n8n to build intake, triage, scheduling, or similar agent flows can mask sensitive fields before prompts reach an external LLM. The workflow keeps running while the model receives a tokenized or substituted version of the data.
Organizations that want to track how employees use ChatGPT, Claude, or Gemini can roll out the monitoring extension and feed detection events into the dashboard. The docs say deployment can be managed through MDM tools such as Google Workspace or Intune.
Security and compliance teams can use the audit trail to review detections, decisions, timestamps, risk categories, and policy snapshots. The source says raw prompt text is not stored, while audit evidence can be exported for review.
Teams handling patient or other regulated data can use masking and trusted-destination controls to reduce exposure before AI calls and restore values only at approved sinks. The site specifically references PHI and HIPAA-oriented workflows.
Teams coordinating multiple agents can track handoffs and see when data moves between agents or sinks. The integration notes that handoff events and trust-score changes are surfaced in the Trust Map.
Privent is installed as a native n8n community node. The docs describe installing the package, adding a Privent API credential, and placing Session, Tokenize, and Detokenize nodes into the workflow so data can be transformed before it reaches external models.
No. The n8n integration page says Privent is audit-only for the workflow: it does not proxy traffic, use a sidecar, or require orchestration changes, and the workflow keeps running while Privent watches and transforms sensitive data.
Privent’s documentation says raw prompt or agent payload text is processed only in-memory during scoring and is never written to disk or used for model training. The stored data is limited to audit and policy metadata such as scores, decisions, timestamps, and workflow identifiers.
The product site says Privent supports n8n today, with LangGraph, CrewAI, MCP, and SDK integrations listed as coming soon in the docs.
Yes. The site states that Privent can be deployed in the cloud, in a dedicated environment, or fully on-prem / private cloud, including a fully on-prem stack with ML inference inside your network.
Les données de trafic sont fournies à titre indicatif uniquement.
| avr. | 0 |
|---|---|
| mai | 0 |
| juin | 0 |
Les analyses de trafic ne sont pas encore disponibles.

www.phinq.co
Phinq est une couche open source de gouvernance à l’exécution pour les agents IA. Elle intercepte leurs appels d’outils, les classe selon leur niveau de risque et suspend les actions les plus risquées pour obtenir une approbation humaine avant exécution.

kastra.ai
Kastra est une infrastructure d’autorisation pour les systèmes d’IA qui vérifie les prompts, appels d’outils, commandes shell, requêtes API et actions du navigateur avant leur exécution. Elle aide les équipes à appliquer les politiques, conserver des journaux d’audit signés et gouverner les workflows d’IA locaux et d’entreprise.

panguard.ai
Panguard AI est une plateforme de sécurité open source pour les agents IA. Elle analyse les skills et les serveurs MCP avant leur exécution et protège les actions des agents à l’exécution, avec des contrôles auto-hébergés et des preuves de conformité signées pour les développeurs, fournisseurs d’IA et équipes réglementées.
openmemory.dev
Mem0 est une couche de mémoire IA pour les agents et les applications. Elle conserve le contexte entre les sessions, retrouve les souvenirs pertinents et personnalise les réponses pour les workflows IA en production.

www.coolplugz.com
CoolPlugz est une couche d’orchestration pour Claude Code qui rassemble le contexte, exécute des workflows structurés et aide à mener à bien des tâches de programmation avec moins de supervision constante. Elle s’adresse aux développeurs qui souhaitent limiter les changements de contexte entre Jira, GitHub, Slack, Notion et CI.

agentinel.habitwala.in
Agentinel est une couche de sécurité locale pour les agents de programmation autonomes. Il vérifie les demandes d’installation avant exécution et bloque les paquets npm suspects grâce à une base OSV hors ligne et à des heuristiques, sans appel cloud.