
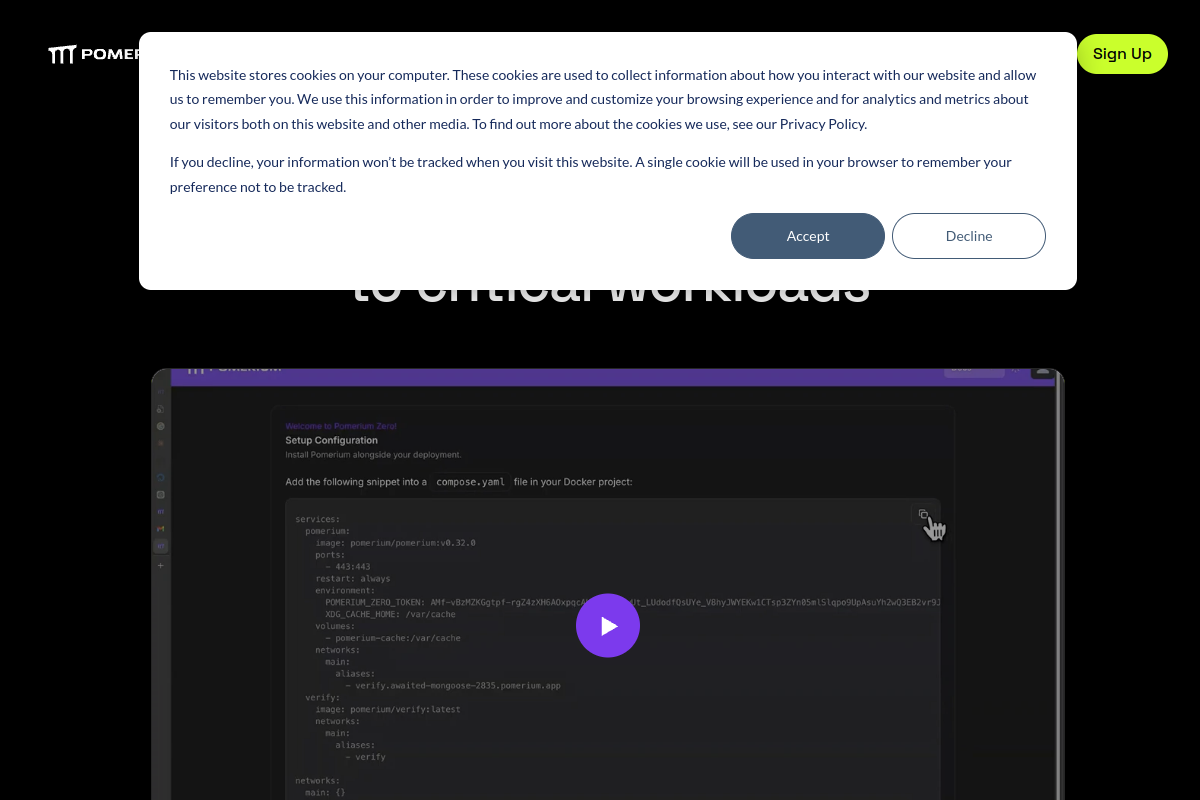
Clientless application access
Provides web-based access to protected applications without a VPN or client-side software, reducing the need to distribute and maintain an access client.
Pomerium is a zero-trust, identity-aware proxy that provides clientless access to web applications and critical workloads without a VPN. It helps security, development, and operations teams authenticate, authorize, and audit requests across human, machine, and agentic identities.
Pomerium is a Layer 7, identity-aware reverse proxy for clientless access to web applications and critical workloads. It provides secure connections without a VPN or client-side software by authenticating requests, applying authorization policies, and proxying approved traffic to upstream applications.
Pomerium integrates with OIDC-compliant identity providers and can incorporate device context into access decisions. Its zero-trust model authenticates and authorizes every request rather than granting implicit trust after a user signs in. Policies can be managed through a builder UI or expressed as YAML-style policy as code.
The platform centralizes routes, policies, users, sessions, service accounts, and operational data. It logs requests and sessions for auditing, supports continuous policy enforcement, and can pass cryptographically signed JWTs to upstream applications.
Provides web-based access to protected applications without a VPN or client-side software, reducing the need to distribute and maintain an access client.
Authenticates through an OIDC-compliant identity provider and enforces fine-grained, policy-based authorization for requests to upstream applications.
Supports YAML-style authorization policies as well as a policy builder UI for defining access rules, including conditions based on identity and available device context.
Brings users, routes, policies, sessions, service accounts, events, and runtime data into a common administrative interface, with request and session logging for review.
Connects approved requests to upstream applications through cryptographically signed JWTs, supporting application-level authentication and additional request context.
Re-evaluates policy during an established session and logs requests, rather than treating the initial sign-in as the only access decision.
Protect Kubernetes ingress, kubectl, Gateway API, and upstream applications without requiring a client, using identity-aware access policies at the gateway.
Give remote employees and distributed teams access to internal applications through browser-based connections instead of relying on a VPN workflow.
Apply scoped or just-in-time permissions for contractors and other non-permanent users, with centralized policy changes, revocation, and audit records.
Place internal APIs, secure service access, and other application-to-application connections behind a common authorization layer with service-account support.
Use Pomerium as a gateway for AI agents, prompts, autonomous workflows, and model endpoints so agent actions can be authorized and logged per request.
No. The product is described as providing web-based, clientless access to applications without a VPN or client-side software.
Pomerium integrates with an existing OIDC-compliant identity provider. The site specifically names Okta, Entra ID, and Google as examples, and also references a hosted authentication service or bringing your own provider.
Access rules can be written as YAML-style policy as code or managed through Pomerium’s policy builder UI. The site describes fine-grained, identity-aware policies and support for device context where available.
Yes. The business offering uses a self-hosted data plane with a hosted control plane, while Enterprise is described as a fully self-hosted, on-premise solution. The free personal offering also includes a self-hosted reverse proxy.
The pricing page lists a free personal plan, a business plan priced per user, and an Enterprise plan with custom pricing. The business plan offers a free trial, while Enterprise uses a contact-sales flow; exact limits vary by plan.

manageengine.com
Enterprise IT management software for IT operations, security, identity, endpoints, and service delivery teams.

immuta.com
Immutaは、接続されたデータシステム全体でアクセス制御、データ要求への対応、監査証跡の作成を支援するデータプロビジョニング・ガバナンスプラットフォームです。

wald.ai
Context-aware AI data security for enterprises governing employee use of LLMs and AI applications.

checkr.com
Background checks and identity verification for hiring, lending, housing, and platform trust workflows.
abnormal.ai
Behavioral security for organizational email, identities, and AI governance.

nightfall.ai
Data loss prevention for security teams governing data across AI, endpoints, SaaS, and email.