
Pre-execution tool-call decisions
AIF analyzes supported coding-agent tool calls before they run and can allow, ask for approval, make an action safe, block it, or record it.

Agentic Integrity Foundation is a local endpoint-security product for coding agents. It evaluates supported tool calls before execution and can allow, approve, make safe, block, or record actions on a developer’s machine.
Agentic Integrity Foundation (AIF) is Harden’s endpoint-security product for coding agents. It runs cybersecurity-focused models locally on a developer’s device and evaluates supported tool calls before they execute.
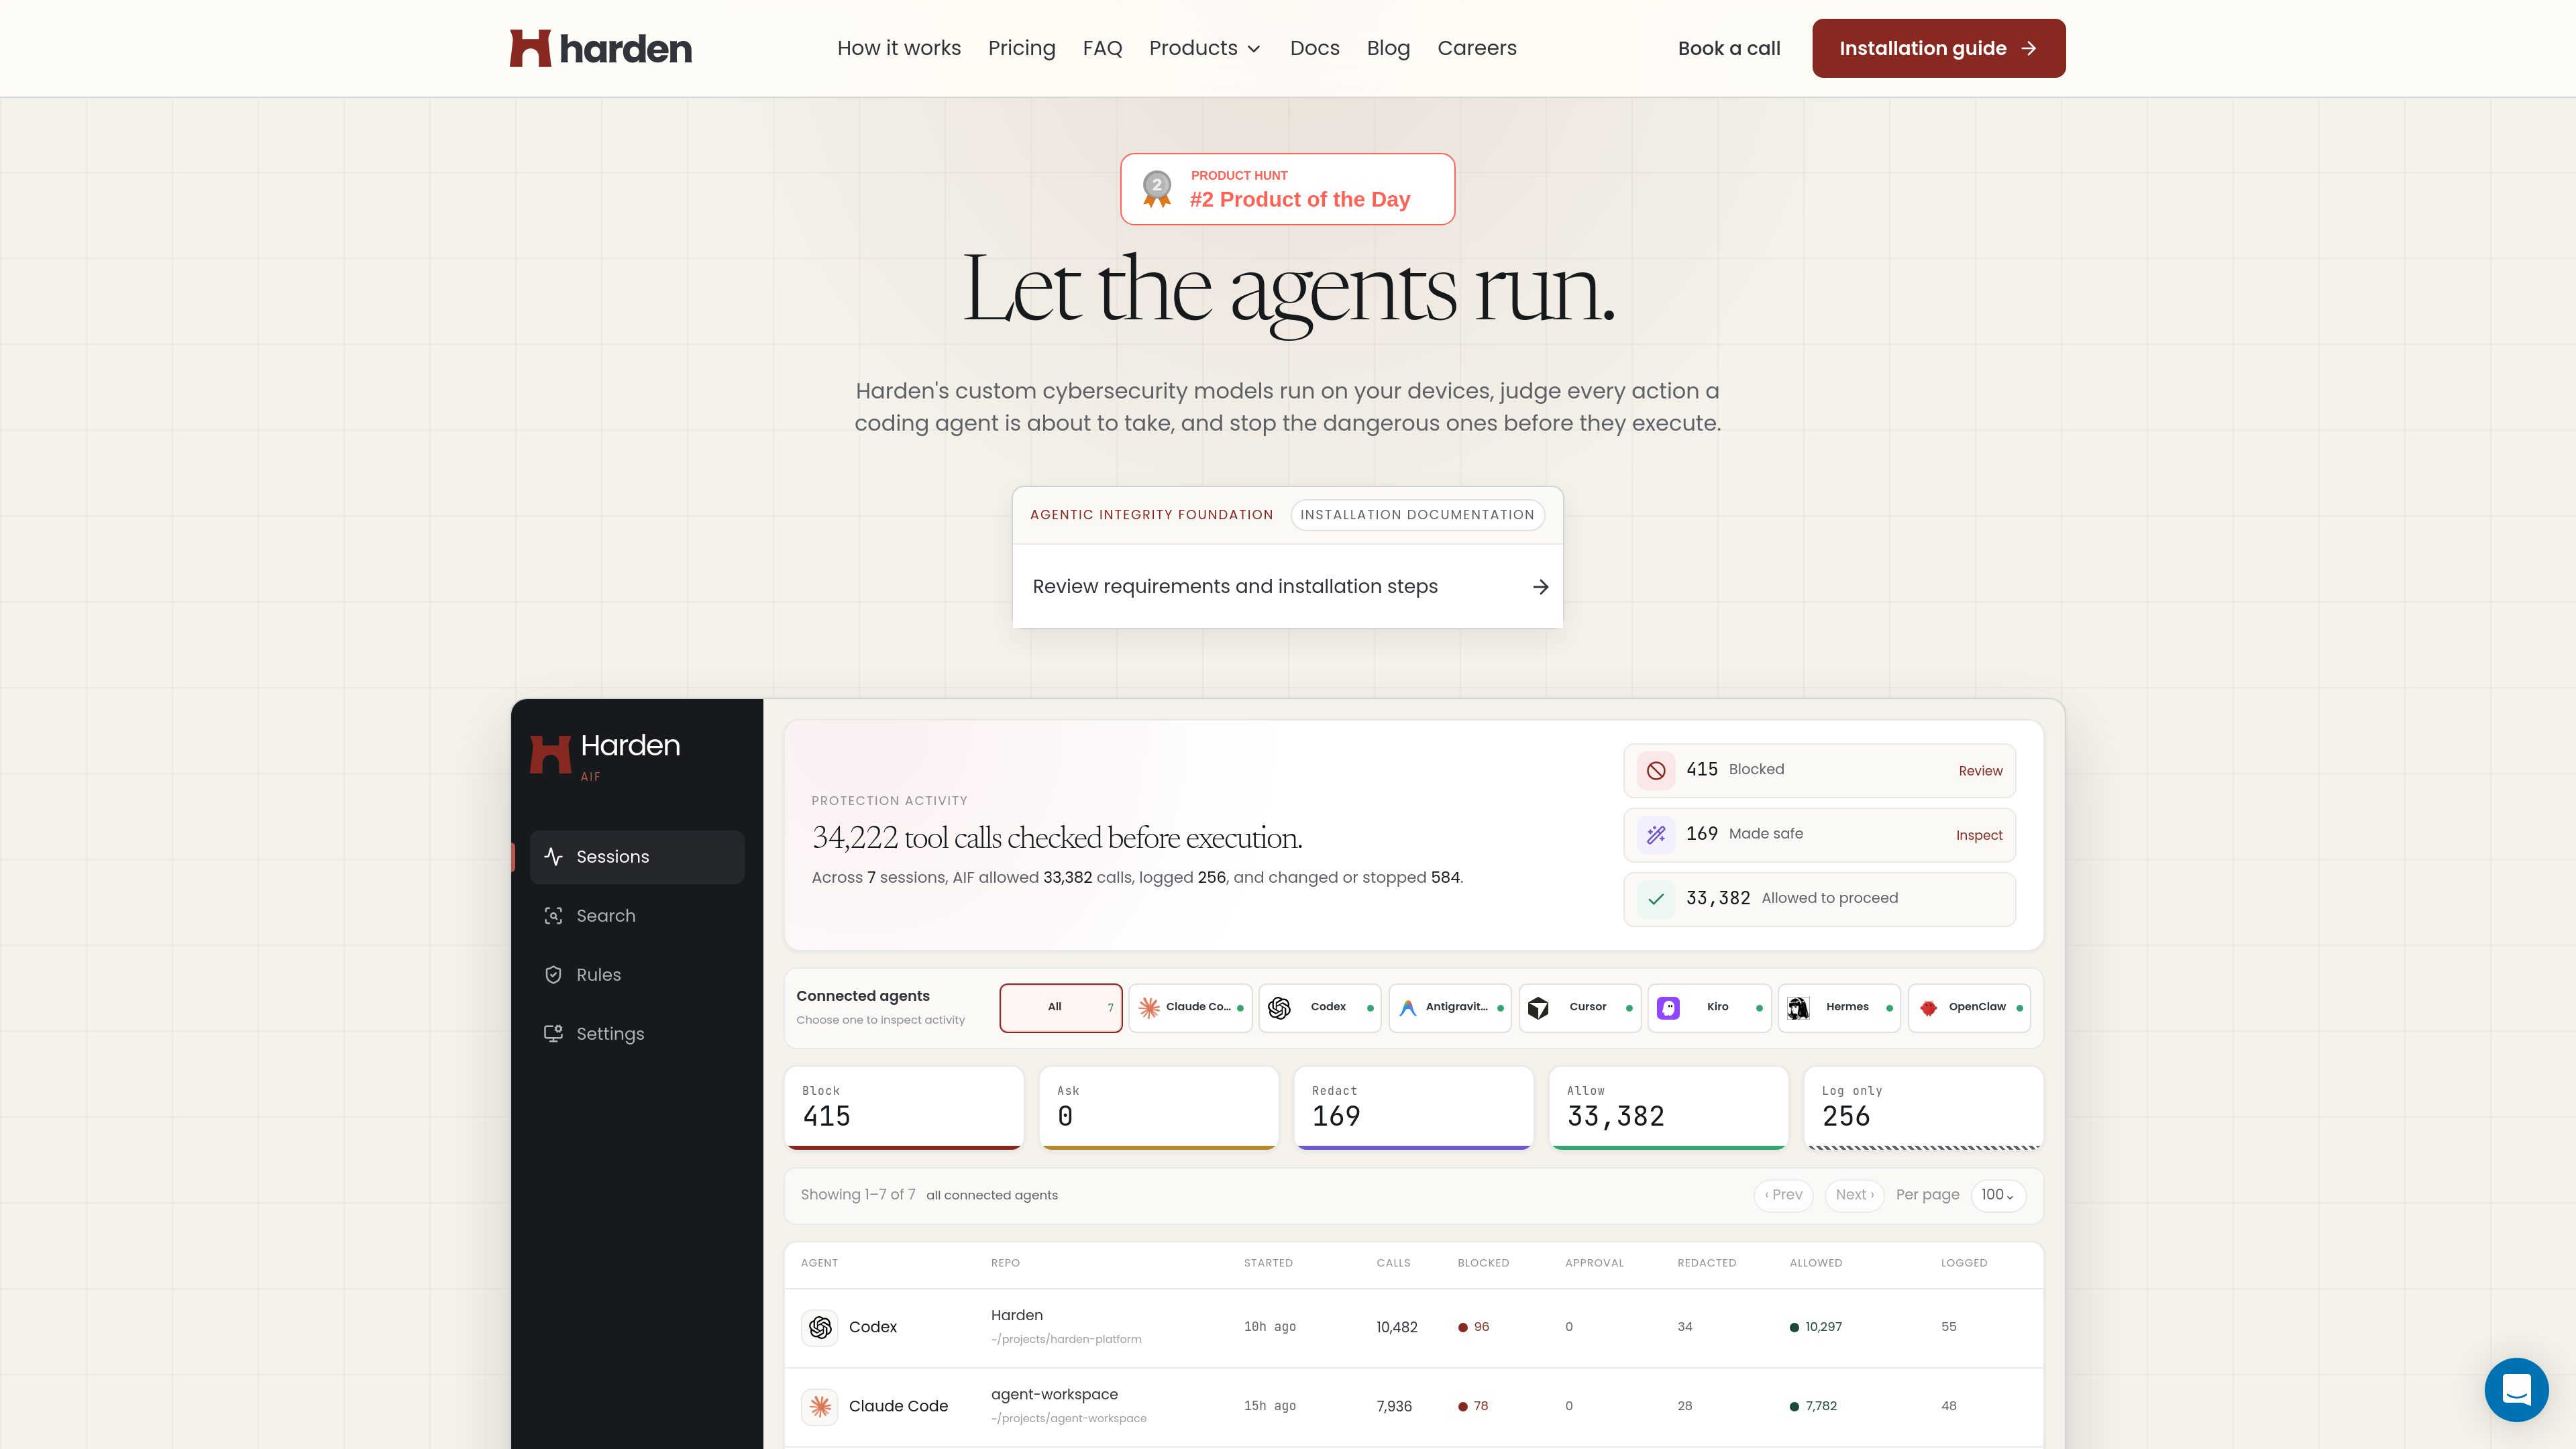
AIF adds a decision layer between a coding agent and the systems it can access. Depending on the action, it can allow the call, request approval, make the action safer, block it, or record it. Its local dashboard shows activity across connected agent sessions, with counts and inspection views for actions that were allowed, blocked, logged, redacted, or changed.
The product is intended for developers and organizations that want coding agents to operate with pre-execution controls rather than relying only on sandboxing or credential gateways. Native hooks are available for listed agents, with an MCP proxy fallback for other tools.
AIF analyzes supported coding-agent tool calls before they run and can allow, ask for approval, make an action safe, block it, or record it.
Cybersecurity-focused models run locally on the developer’s device, while the product keeps decision history in a local store.
When an action is unsafe, AIF can stop it and suggest a safer retry. The site illustrates steering a production namespace operation toward staging.
The dashboard groups activity by connected agent session and exposes counts for allowed, blocked, logged, redacted, and changed calls.
AIF uses native hooks for supported coding agents and provides an MCP proxy fallback for other tools.
Users can install the product, run `aif configure`, and connect their agents without creating an account or providing a credit card.
A developer can use AIF to inspect agent-generated commands that affect deployments, namespaces, or other operational systems before execution, reducing the chance that a destructive production action runs unreviewed.
Teams can use block-and-steer behavior to redirect an unsafe operation toward a permitted alternative, such as retrying against staging instead of production.
Developers using multiple coding agents can inspect connected sessions in one activity view and compare how many calls each session allowed, blocked, logged, or changed.
Individual developers can use the local runtime and local decision store when they need an endpoint control layer without an account. Organizations can discuss an Enterprise air-gap or zero-telemetry mode for stricter deployment requirements.
Install the free product, run `aif configure`, and connect the coding agents you use. The site states that no account or credit card is required for this setup.
The site lists Claude Code, Codex, Antigravity CLI, Cursor, Kiro, Hermes, and OpenClaw. It also describes an MCP proxy fallback for other tools. Compatibility is checked against supported-agent releases.
Yes. The product describes a local-first runtime in which its cybersecurity-focused models run on the developer’s device and decision history is stored locally.
AIF can block the action, ask for approval, make it safe, or record it. Its block-and-steer workflow can also provide a safer retry for the developer to run.
The published requirements list macOS on Apple Silicon and macOS or Linux on x86_64. Windows is not supported yet. The stated requirements are 16 GB of memory minimum, 24 GB recommended, and 15 GB of free disk space.
トラフィックデータは参考情報としてご利用ください。

www.neatproxy.com
Guardrail is a local spend firewall for AI coding agents. It records usage metadata and, on supported proxy integrations, checks budget policies before forwarding requests to providers.

veecle.ai
Chiplab is an MCP platform that lets AI coding agents run firmware against virtual instances of target chips instead of waiting for physical hardware. It provides chip-aware execution and searchable embedded-development knowledge through a single endpoint.

getbb.app
bb is a local-first, open-source IDE for running coding agents in parallel, organizing their work in threads, and extending the workspace with plugins. It is designed for developers and teams that want to coordinate provider-based agents and customize their software workflow.
termaxa.com
A cooperative gate that previews, evaluates, and records shell commands run by AI coding agents.
apra-labs.github.io
apra-fleet runs a fleet of AI agents across multiple machines and provider CLIs. It provides a common execution model for combining Claude, Codex, Copilot, Antigravity, and local models.
arcjet.com
Arcjet is an AI agent runtime security platform for inspecting and enforcing policy on agent actions, prompts, tool calls, and data flows. It also protects web and AI endpoints from bots, prompt injection, sensitive-data leaks, and uncontrolled usage.