
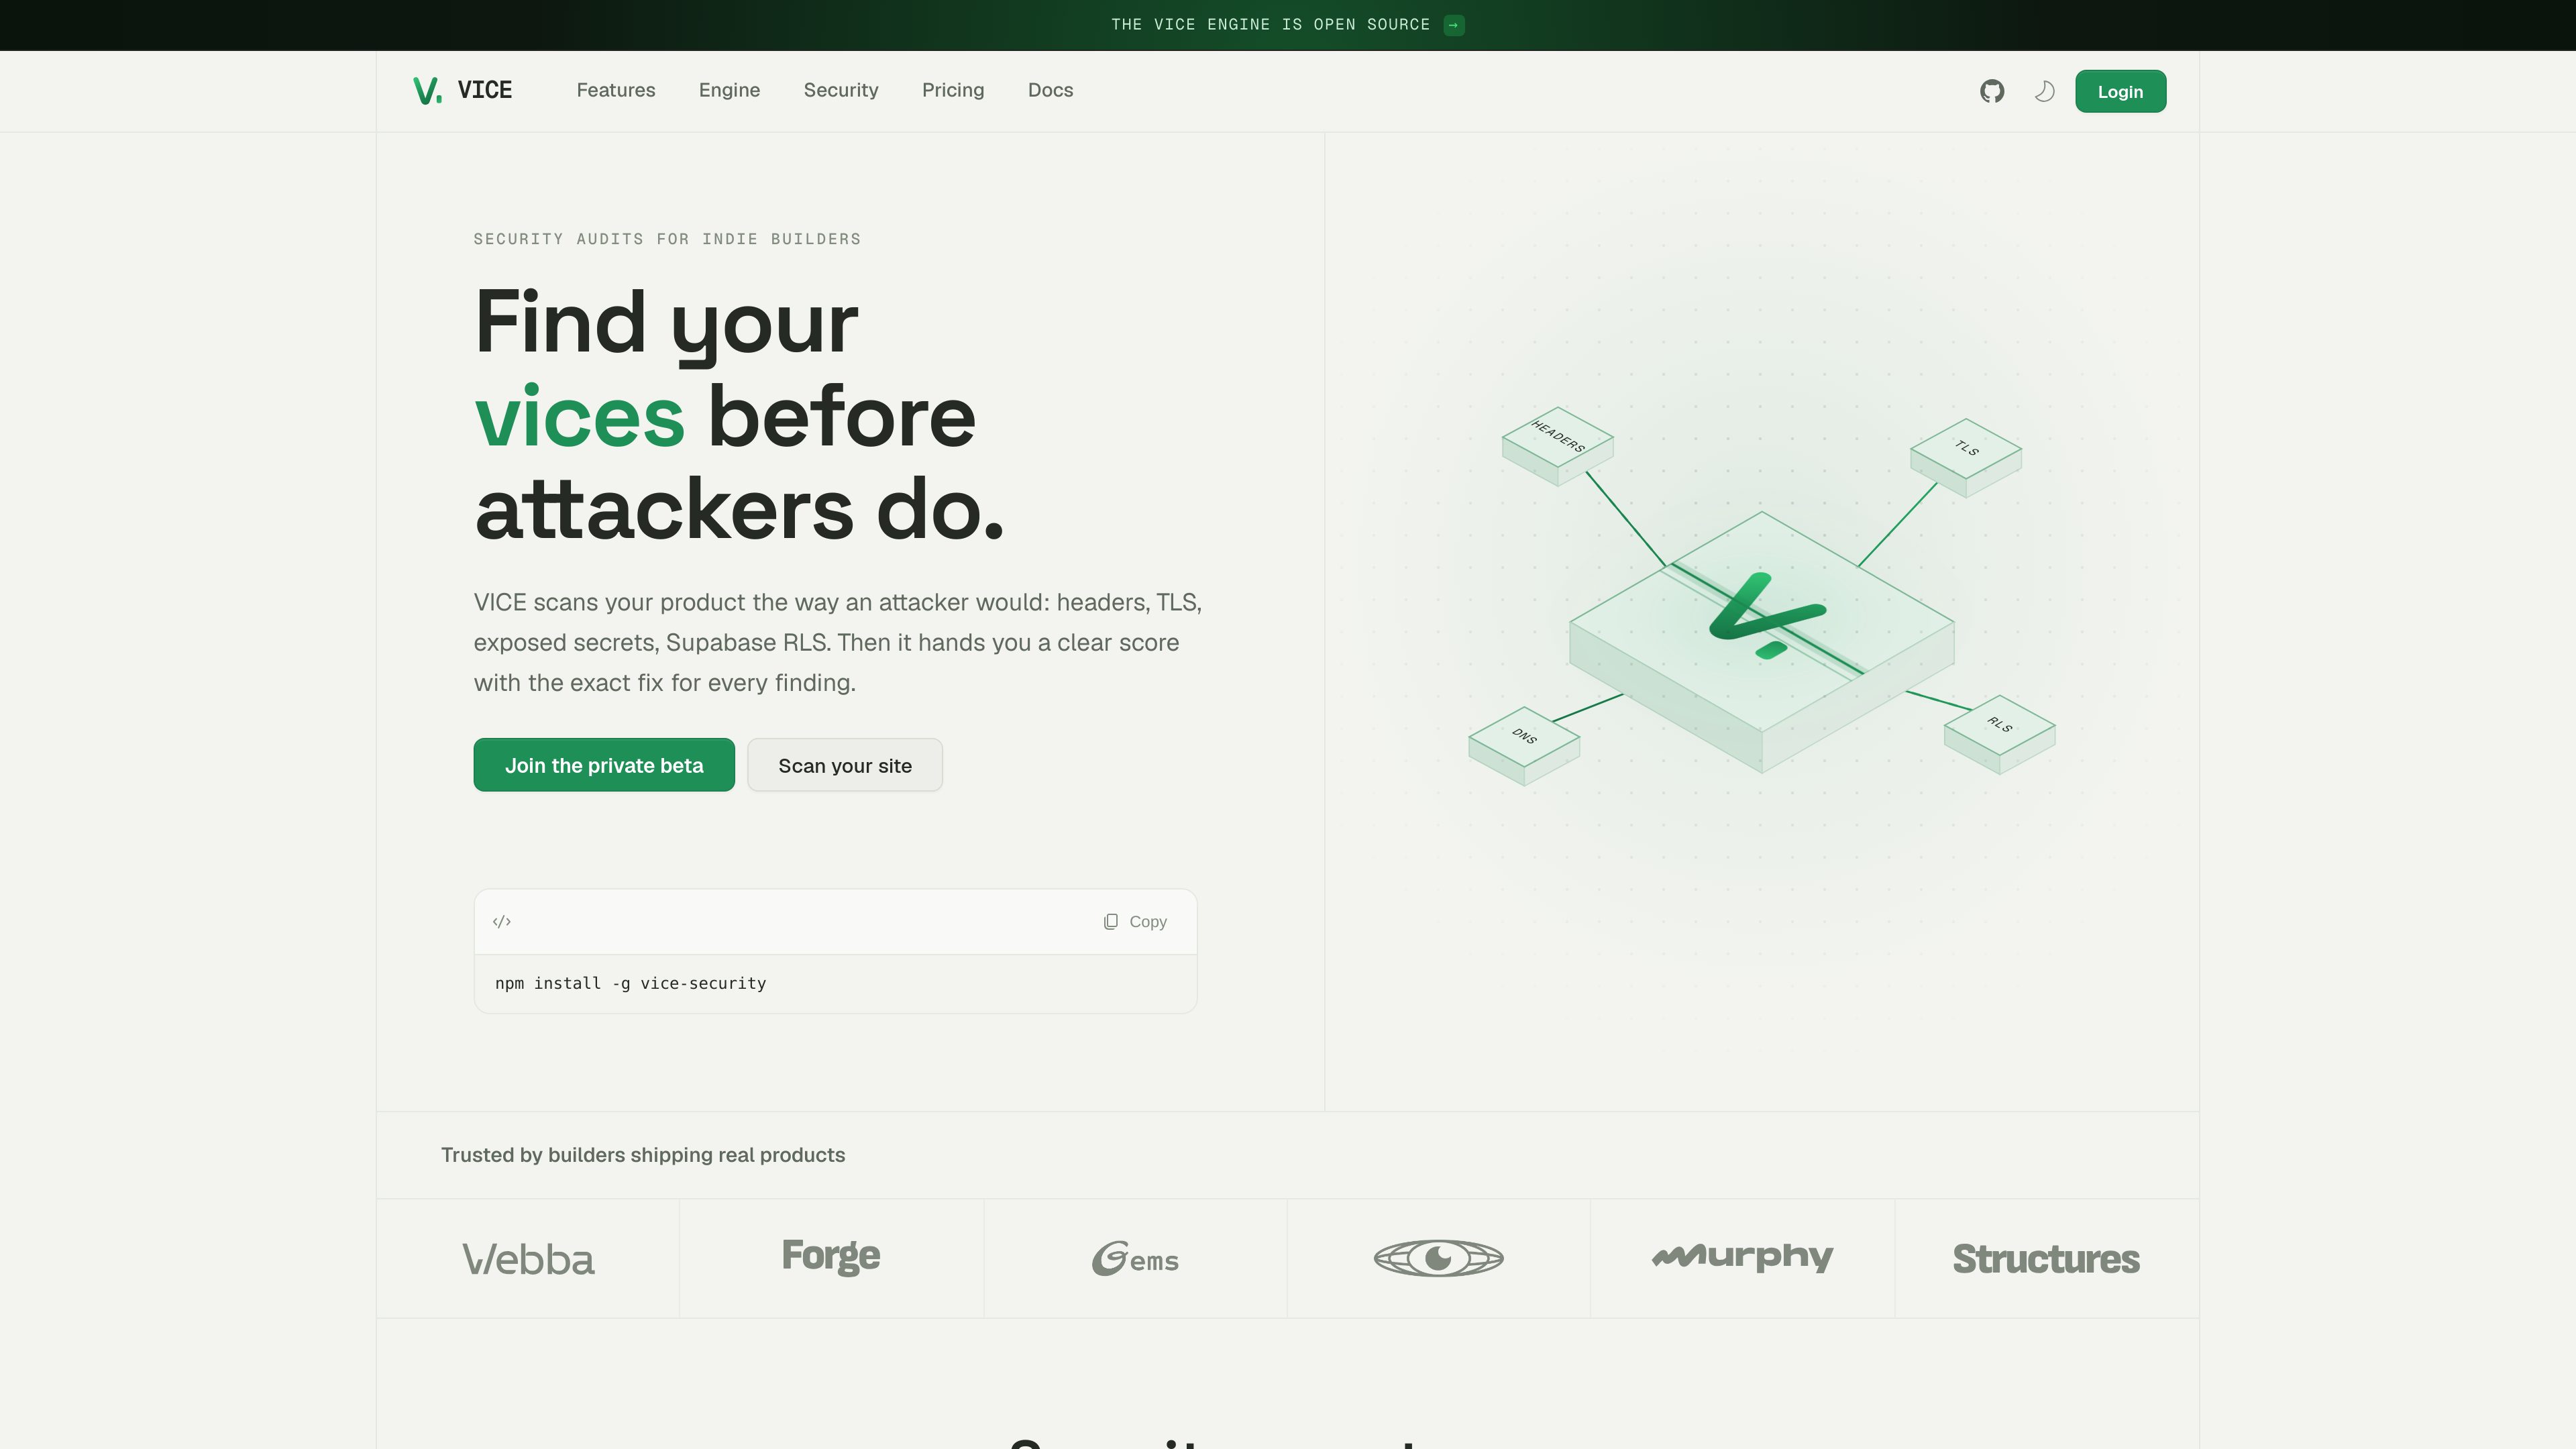
Free public light scans
Run a non-intrusive scan without signing up. The light scan checks public signals like security headers, TLS, robots.txt and security.txt, exposed files, and secrets leaked in public JavaScript.

VICE realiza auditorias de segurança web para desenvolvedores independentes, com verificações rápidas públicas, auditorias completas verificadas, análises aprofundadas de Supabase RLS, correções com AI e verificações de CI.
VICE scans web products for security issues using both public, non-intrusive checks and verified audits tied to a domain you own. The platform focuses on findings with evidence, clear scoring, and remediation context so builders can review what was found and what to do next.
It covers common web exposure checks such as headers, TLS, exposed files, and leaked secrets, plus deeper modules like Supabase Deep Scan, AI/RAG security checks, WordPress checks, scheduled audits, and CI-based audits through GitHub Actions.
Run a non-intrusive scan without signing up. The light scan checks public signals like security headers, TLS, robots.txt and security.txt, exposed files, and secrets leaked in public JavaScript.
Deeper checks unlock after a DNS TXT record proves domain ownership. Verified audits stay scoped to domains you own and are designed to be non-destructive.
VICE can inspect a Supabase project once per domain and check tables, RLS policies, storage bucket exposure, and edge functions for real exposure.
Each finding can include a plain-language explanation and an exact patch. The product keeps raw evidence next to the remediation so you can confirm the issue before applying a fix.
The GitHub Action can run audits on every push and fail the build when a new critical finding appears. Scheduled weekly or monthly runs keep the score fresh and catch regressions.
Each domain has its own workspace, with audits, findings, modules, and history attached to that domain rather than spread across separate projects.
Use the free public scan to validate the basics before signup friction, or buy a single audit credit for a one-off pre-launch review of a project.
For products built on Supabase, save the project once per domain and use the deep scan to look for missing RLS policies, permissive policies, exposed storage buckets, and related exposure.
Run weekly or monthly scheduled audits so the score stays current and new findings are caught before users encounter them.
Add the GitHub Action to your build pipeline so an audit runs on each push and the build can fail when a new critical issue is introduced.
Use the Pro plan structure to manage more than one verified domain, keep score tracking together, and generate shareable white-label reports.
It checks public signals only: security headers, TLS, robots.txt and security.txt, exposed files, and secrets leaked in public JavaScript. It does not use authentication or intrusive probing.
A DNS TXT record proves that you own the domain. Once verified, deeper audits unlock for that domain and remain scoped to it.
Yes. The GitHub Action can run an audit on every push, fail the build when a new critical issue appears, and update the score badge automatically.
You save the Supabase project URL and anon key once per domain, and VICE checks what those public credentials can reach, including RLS gaps, permissive policies, exposed storage buckets, and edge functions.
Yes for the public light scan. The site says no account is needed for the instant public check, while verified audits and connected workflows use logged-in features.
Os dados de tráfego são apenas para referência.
helsing.ai
O site público da Helsing está atualmente bloqueado por uma verificação de segurança da Vercel.

pixso.cn
Ferramenta cloud de colaboração em design de produtos, com criação de UI assistida por AI, quadros brancos, prototipagem e entrega para desenvolvedores.

mentra.glass
Plataforma open source de óculos inteligentes para equipes em campo e desenvolvedores que criam fluxos com câmera, assistentes de IA e apps personalizados com MentraOS.
etok.ai
Tutoriais para desenvolvedores sobre fluxos de trabalho, modelos, configuração e ferramentas CLI de IA
asterisk.so
Plataforma de segurança nativa em IA para detectar, validar e corrigir vulnerabilidades
lopus.ai
Lopus unifica dados empresariais para análises de RevOps e BizOps