
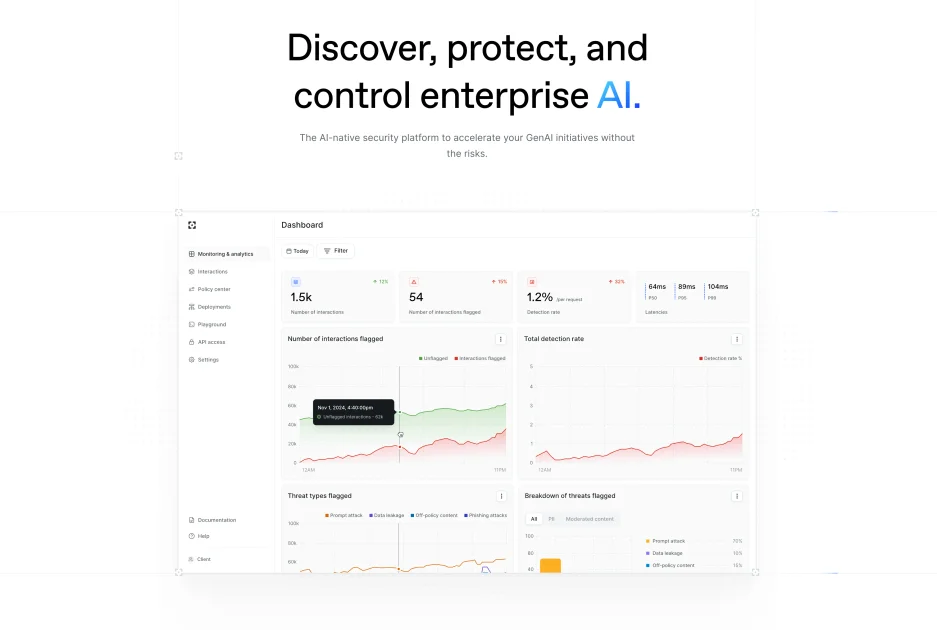
Workforce AI security
Discovers shadow AI use across applications and browsers, protects sensitive data in prompts, and applies policy controls by user, app, and action.

AI-native security for protecting enterprise GenAI applications, agents, and users.
Lakera is an AI-native security platform for organizations building and using generative AI. It helps teams control what AI systems can access and do by detecting threats, protecting data, and applying security policies across employee workflows and AI applications. The platform covers workforce AI security, AI agent security, and AI red teaming, with API-first and cloud-native deployment options.
Choose the employee, application, or agent workflow you need to protect. For the Guard API component, connect application messages to a project and configure its policy and mode. Inspect detection results and test relevant attacks before relying on a blocking configuration; these controls do not guarantee that every attack or data leak will be prevented.
Discovers shadow AI use across applications and browsers, protects sensitive data in prompts, and applies policy controls by user, app, and action.
Screens AI application interactions at runtime for prompt attacks, suspicious content, and data leakage. Detection and blocking depend on the configured policy and project mode.
Supports risk-based GenAI red teaming with vulnerability management, collaborative remediation guidance, and direct and indirect attack simulations.
Uses context-aware detection to identify prompt injections, jailbreaks, and other AI attacks. Guard API screening returns a flag and can provide detailed detector results for policy review.
Provides centralized policy controls, API-first architecture, cloud-native deployment, and enterprise integrations. Deployment and configuration differ across the employee, application, and agent workflows.
Supports model-agnostic protection for chatbots and audio bots, with multilingual and multimodal coverage. Evaluate detection behavior on the models, languages, and content used in your application.
Security and IT teams can discover unsanctioned AI use across apps and browsers, then apply user- and action-specific controls to reduce data exposure.
Product and engineering teams can add runtime threat detection, prompt attack prevention, and data leakage protection to chatbots and other GenAI applications.
Teams deploying agents can simulate direct and indirect attacks, track vulnerabilities, and coordinate remediation as agent behavior and threats evolve.
Use API-first protection and centralized policies across GenAI applications, then evaluate the integration and policy behavior for each application rather than assuming every deployment needs no changes.
Lakera secures employee interactions with AI, AI-powered applications, agents, and related data flows. Its stated protections include prompt attacks, jailbreaks, and data leakage.
Lakera provides API-first, cloud-native workflows, with SaaS deployment and enterprise integrations. Guard API documentation also covers self-hosting. Choose and configure the deployment for the specific security workflow rather than treating all modules as identical.
Yes. AI Agent Security covers agent discovery, access and risk assessment, and runtime controls for tool-connected systems. Its application and Guard API workflows also screen chatbot interactions. Configure the relevant policies and test the resulting behavior.
Lakera supports model-agnostic protection for chatbots and audio bots, with multilingual and multimodal coverage. That scope does not promise equal detection quality for every language, modality, or model; evaluate your actual application inputs.
Os dados de tráfego são apenas para referência.
| abr. | 274828 |
|---|---|
| mai. | 305851 |
| jun. | 259130 |