
AI development controls
Provides governance and preventative guardrails for AI tools, prompts, and generated code, including controls intended to block risky activity before code is committed.

Agentic development security platform for controlling, contextualizing, and remediating software risk from prompt to runtime.
Cycode is an Agentic Development Security Platform that helps security and development teams manage software risk across the agentic development lifecycle, from AI prompts and generated code through production. It combines preventative controls, code-to-runtime context, and agent-orchestrated remediation in one platform. The platform brings together AI, application, secrets, and software supply chain security so teams can identify exploitable risk, prioritize issues using ownership and exposure context, and create fixes that are ready for review before vulnerabilities reach production.
Provides governance and preventative guardrails for AI tools, prompts, and generated code, including controls intended to block risky activity before code is committed.
Connects signals across the agentic development lifecycle, application security testing, software supply chain security, and application security posture management to provide code-to-runtime context.
Combines SAST, SCA, infrastructure-as-code, container, secrets, and CI/CD pipeline scanning in a single application security experience.
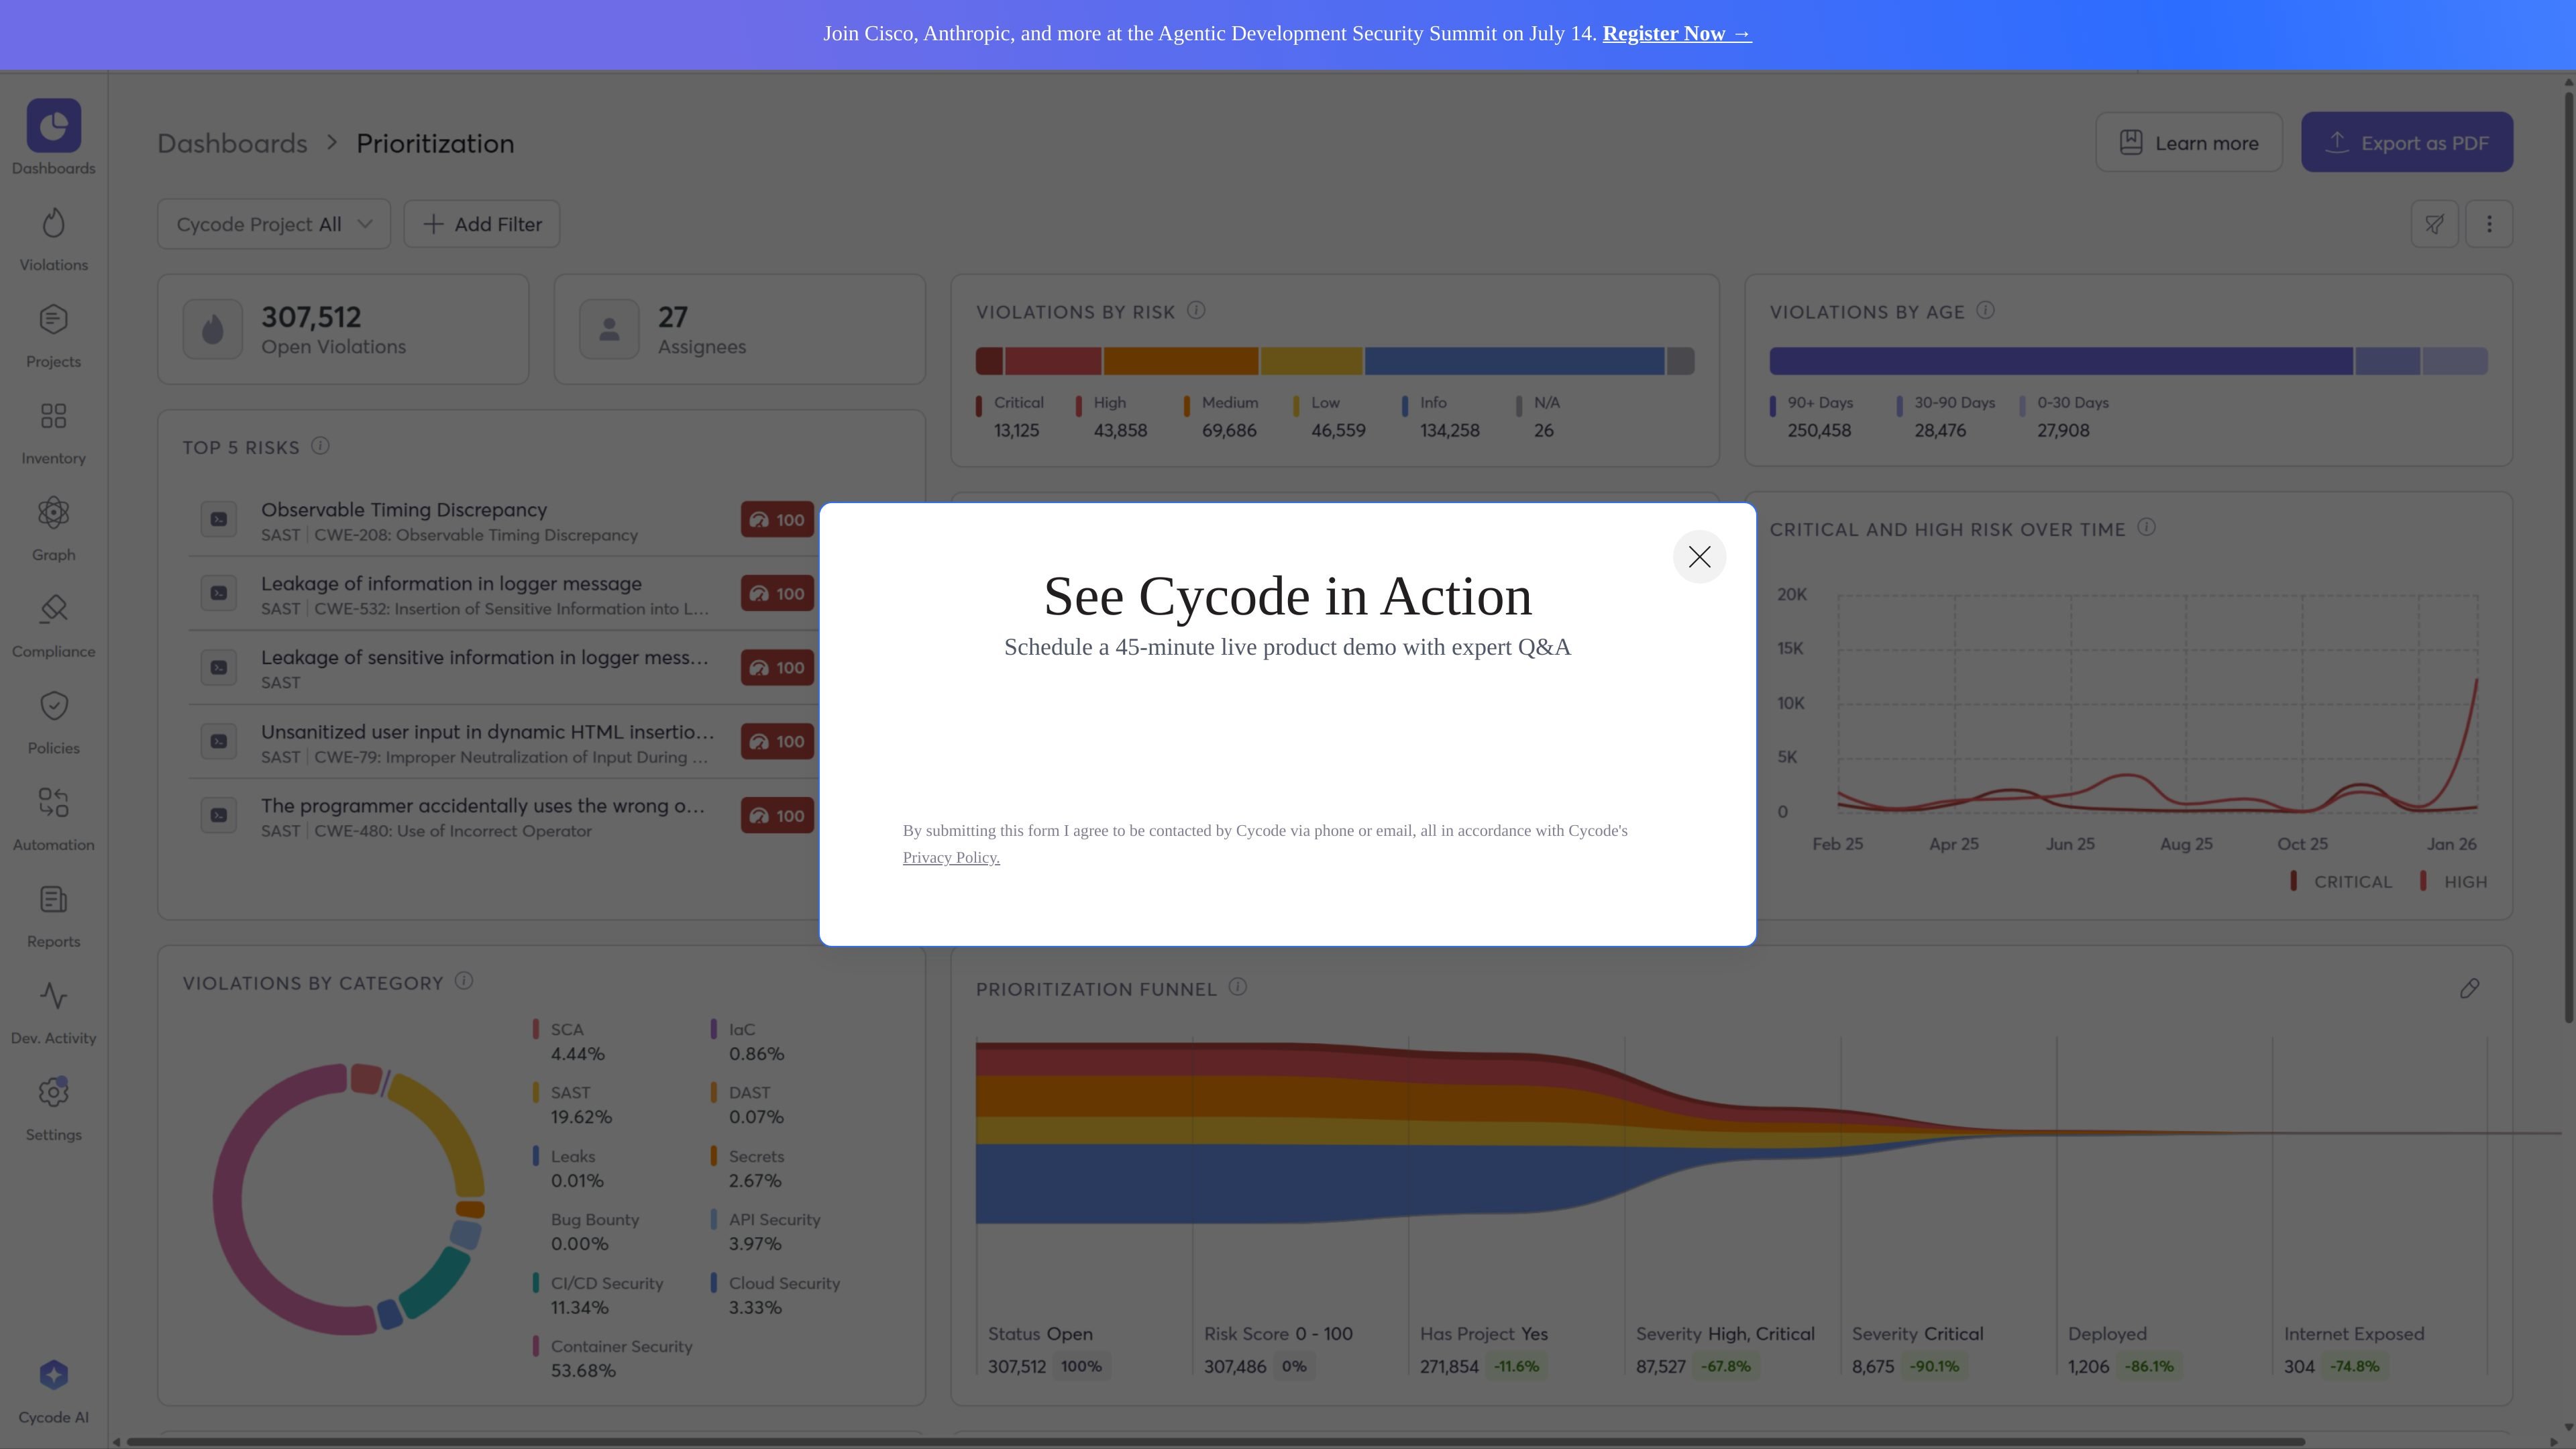
Uses factors such as reachability, asset exposure, ownership, exploitability, and blast radius to help teams focus on risks that require action.
Coordinates purpose-built agents that can confirm exploitability, assess change impact, generate fixes, open pull requests, and retain an audit trail with reasoning.
Connects with Git, IDE, and CI/CD workflows to surface weaknesses, vulnerabilities, misconfigurations, and remediation guidance where development work takes place.
Security teams can apply policies and guardrails to AI-driven development, review AI-generated code, and extend visibility to AI tools and related risks before they enter the delivery workflow.
Application security teams can correlate findings with reachability, exposure, ownership, and runtime context to reduce noise and direct remediation toward risks with meaningful impact.
Engineering organizations can scan secrets, source repositories, dependencies, containers, and CI/CD pipelines to identify weaknesses across the software factory.
Organizations can consolidate SAST, SCA, infrastructure-as-code, container, secrets, and pipeline scanning while maintaining a shared view of application risk.
Security and development teams can use Maestro agents to investigate findings, trace blast radius, generate pull-request-ready fixes, and document the resulting decisions.
Cycode covers AI-driven development, source code, dependencies, secrets, containers, infrastructure-as-code, CI/CD pipelines, and application risk from code through runtime.
Its risk intelligence capabilities consider context such as exploitability, reachability, asset exposure, ownership, runtime context, and blast radius to help teams focus on actionable risk.
Maestro is Cycode's agent orchestration capability. It coordinates agents for tasks such as exploitability confirmation, change-impact analysis, natural-language graph queries, and generation of pull-request-ready fixes.
The platform offers Git, IDE, and CI/CD integrations that surface security findings and guidance within existing development workflows, including code review and pull requests.
The pricing page describes a model based on what an organization protects from code to cloud and states that there are no per-seat penalties. Pricing details are provided through Cycode's pricing and sales flows.
Traffic data is for reference only.
