Docker MCP Enterprise Gateway logo

Docker MCP Enterprise Gateway

Freemium
訪問

Docker MCP Enterprise Gateway governs how MCP-compatible clients access approved servers and tools. It applies identity-aware policy, supplies credentials from an approved secret store, and records tool-call decisions for enterprise teams.

Docker MCP Enterprise Gatewayとは?

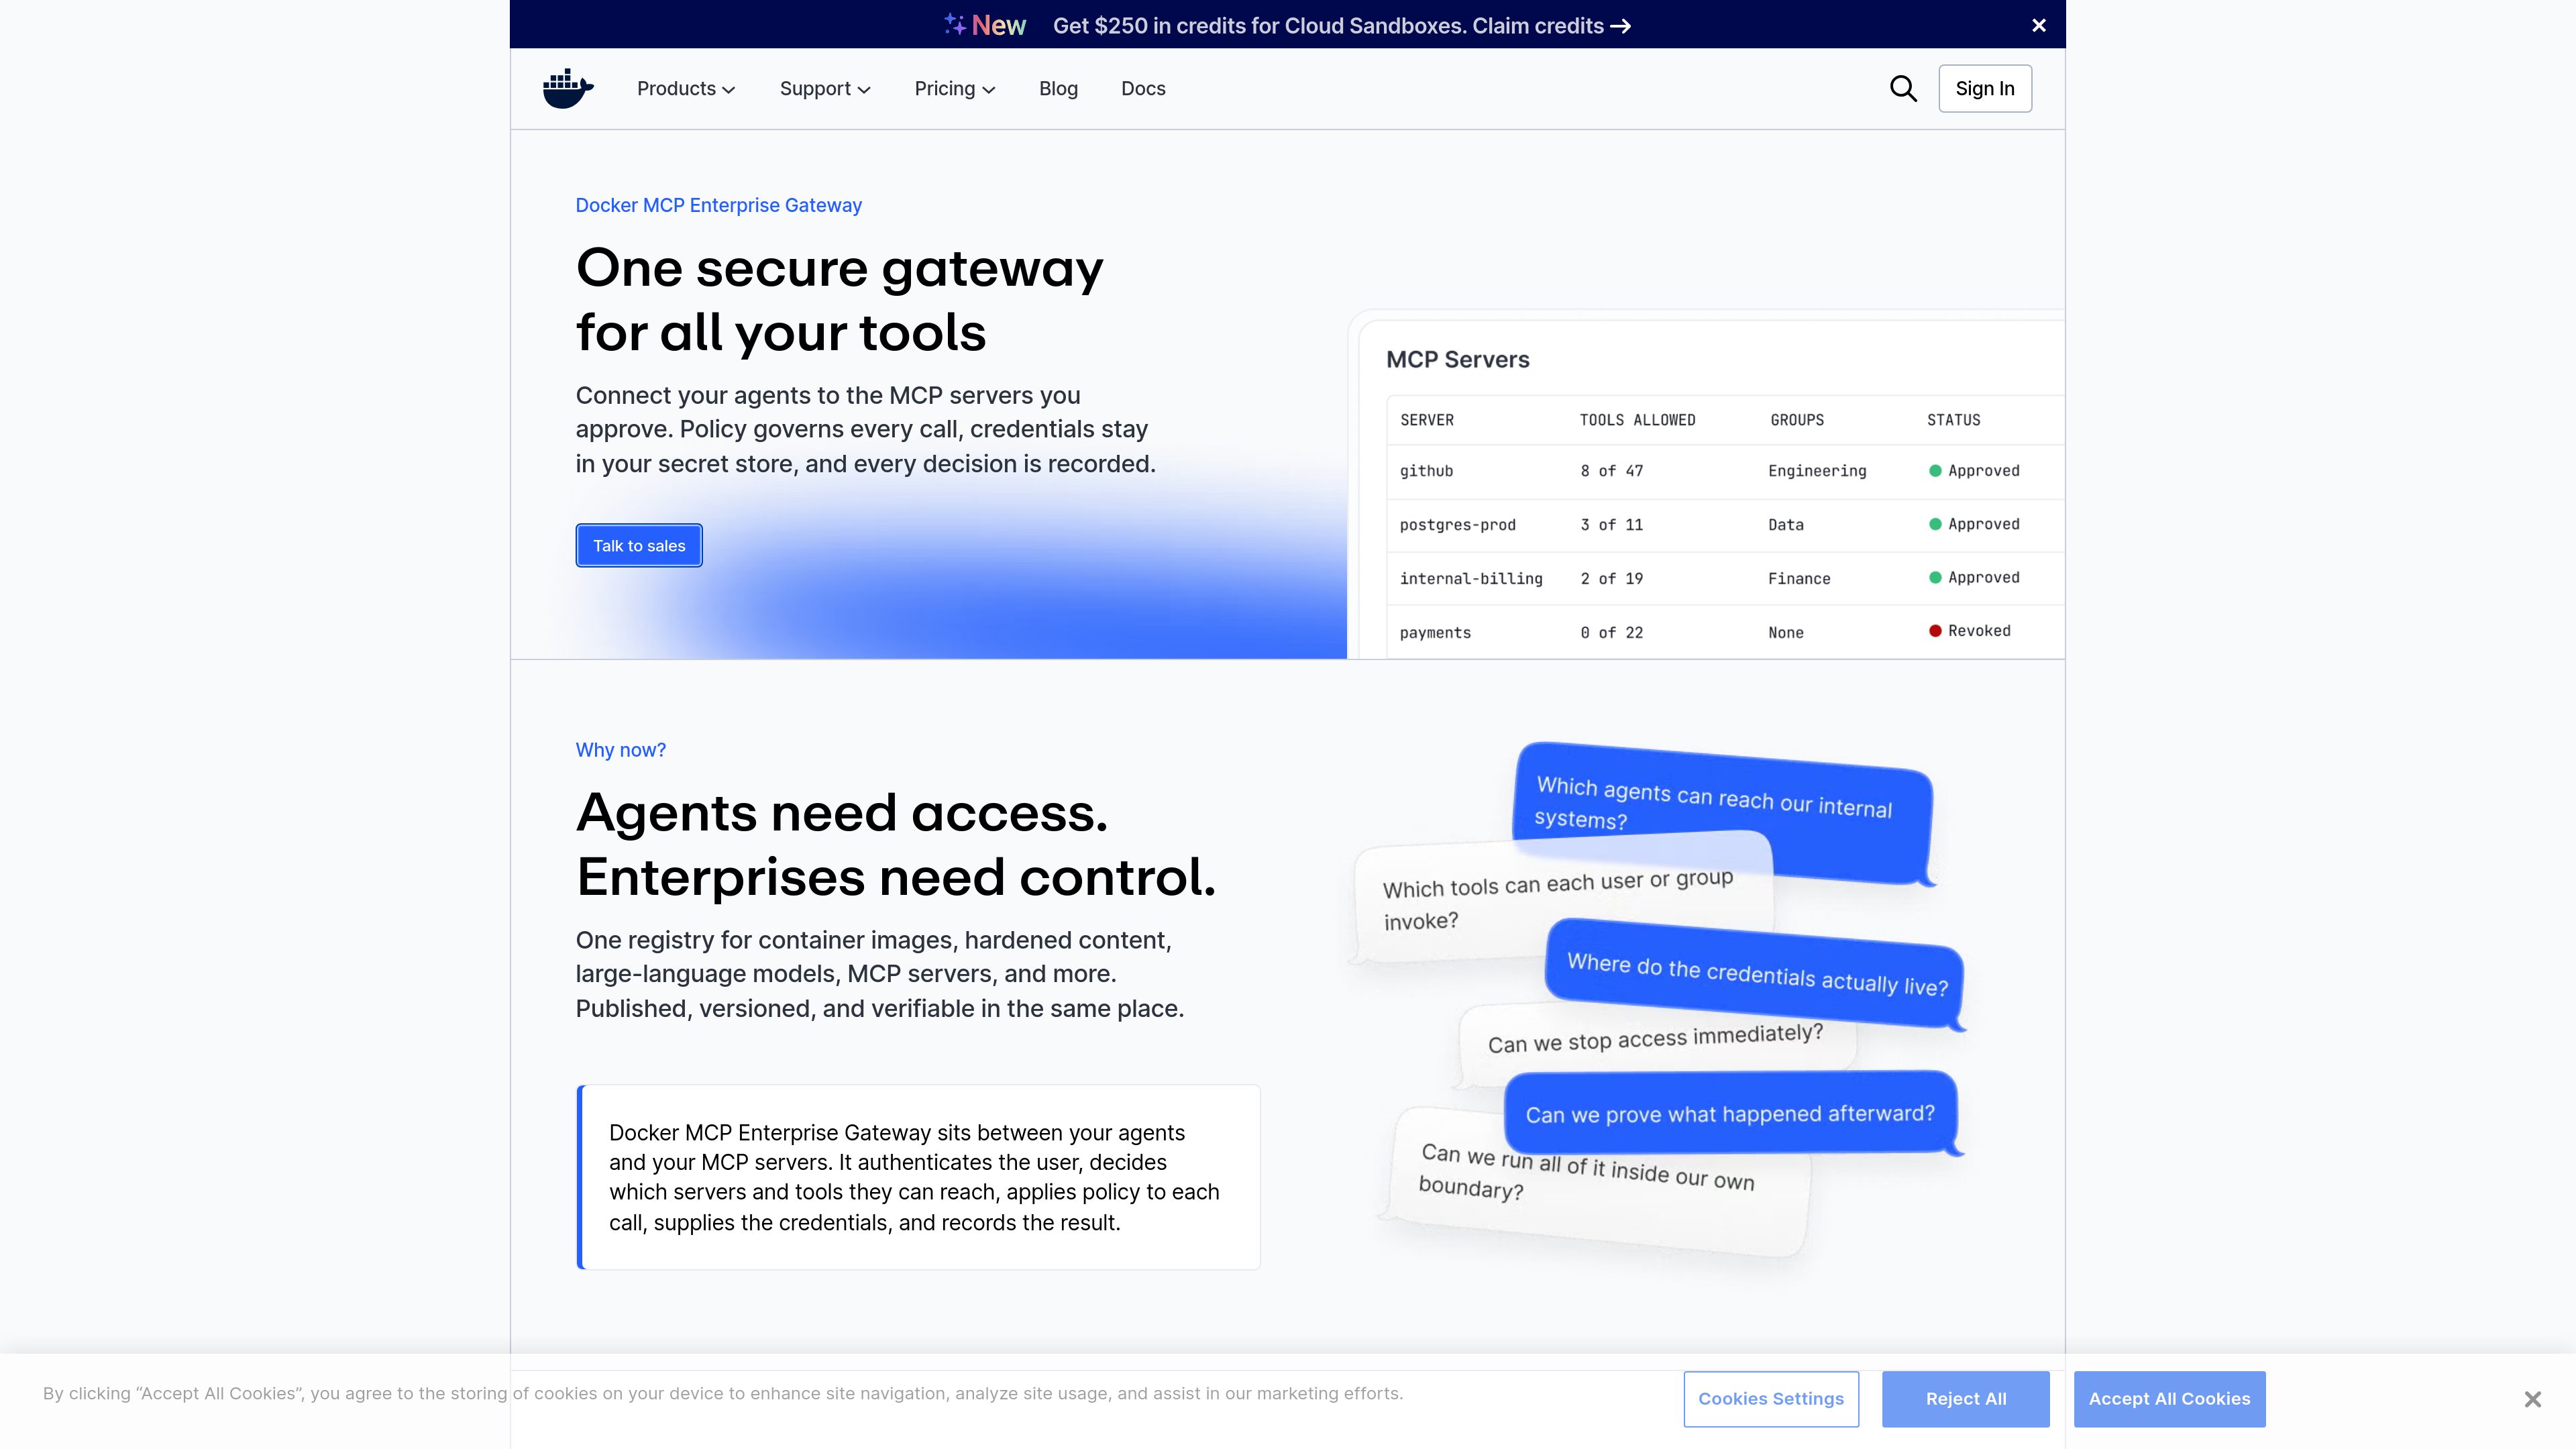
Docker MCP Enterprise Gateway is an enterprise gateway between MCP-speaking clients and MCP servers. It authenticates the user, determines which servers and tools are available to their groups, evaluates policy for each call, supplies credentials from an approved secret store, routes the request, and records the decision.

It is designed to centralize governance across remote services, containerized servers, and internal servers built by an organization. Administrators manage approved servers and tool access centrally, while developers connect their client to a gateway endpoint.

Docker MCP Enterprise Gatewayでできること

Identity-aware access and call policy

The gateway resolves access using the user’s identity and groups, then evaluates rules for the specific call. Rules can allow or deny access by server, tool, transport, and call; unapproved servers are denied by default.

Central server catalog and tool scoping

Administrators add and publish servers for selected groups and expose only the tools those groups need. Developers connect their client once, and catalog or policy changes take effect without individual client reconfiguration.

Credential injection at call time

Credentials are retrieved from the organization’s approved secret store when a tool runs, rather than being distributed through client configuration files.

Structured audit events and SIEM streaming

Each policy evaluation produces a structured event associated with the user and agent. Events can be streamed to the organization’s SIEM pipeline.

Multiple server types and deployment options

The gateway handles remote services over HTTP or SSE, containerized servers, and internally built servers. Containerized servers run in isolated containers. Deployment options listed include a Docker-operated instance in a customer cloud account or VPC and an air-gapped appliance on private Kubernetes.

Dynamic MCP tool discovery

Agents can discover and invoke tools as needed instead of loading every tool definition up front, reducing the amount of tool catalog context loaded for each request.

利用シーン

“Standardize access across coding agents”

A platform team can replace separate MCP configurations with a centrally approved catalog and group-based access, allowing developers using different agent harnesses to follow the same governance rules.

“Bring internal services to agents without distributing secrets”

Teams can connect internally built MCP servers and have the gateway provide credentials at call time, avoiding long-lived credentials in client configuration files.

“Review and investigate tool activity”

Security teams can use identity-linked events for individual tool-call evaluations and stream those records into an existing SIEM pipeline.

“Run governed MCP in restricted environments”

Organizations that require an air-gapped deployment can run the appliance on private Kubernetes, loading catalogs, server images, and policy from within the network without an outbound connection.

よくある質問

Which clients can connect?

The gateway supports clients that speak MCP. The product page names Claude Code, Cursor, VS Code, Codex, ChatGPT Enterprise, and agents built in-house.

What server types does it support?

It can connect to remote services over HTTP or SSE, containerized servers, and internal servers built by an organization. Containerized servers run in isolated containers.

Where are credentials stored and handled?

Credentials remain in the organization’s approved secret store. The gateway supplies them when a tool runs, rather than distributing long-lived credentials through client configuration files.

Can it operate without an outbound network connection?

Yes. The air-gapped appliance runs on private Kubernetes and loads catalogs, server images, and policy from inside the network.

How does it work with Docker Sandboxes?

Docker Sandboxes governs the agent’s execution environment, including its network, files, and MCP servers. The gateway governs which servers and tools a client can call. Either can be used independently, or both can operate under central policy.

クイック情報

Category
Enterprise MCP gateway
Primary users
Enterprise platform, security, and development teams
Client compatibility
MCP-speaking clients, including Claude Code, Cursor, VS Code, Codex, and ChatGPT Enterprise
Server types
Remote HTTP or SSE services, containerized servers, and internally built servers
Deployment
Customer cloud account or VPC; air-gapped private Kubernetes appliance
Pricing
Product-specific pricing is not stated on the product page

Docker MCP Enterprise Gatewayの代替品

Obot logo

Obot

obot.ai

Obot is an open-source enterprise AI control plane and MCP gateway for deploying, governing, and auditing AI agents, MCP servers, and Skills. It helps organizations centralize access policies, discovery, authentication, and activity records across AI tooling.

Glama logo

Glama

glama.ai

Glama is a registry and infrastructure platform for discovering, evaluating, and connecting to Model Context Protocol (MCP) servers, connectors, clients, and tools. It supports browsing open-source and remote MCP entries, with hosted access and gateway features described on the site.

0mcp logo

0mcp

0mcp.io

0mcp converts selected operations from an OpenAPI-described API into a hosted Model Context Protocol (MCP) server. It helps SaaS, platform, and internal teams make approved API actions available to MCP-compatible AI clients without implementing and operating the protocol layer themselves.

Dezycro logo

Dezycro

app.dezycro.ai

Dezycro is an operations layer for AI coding agents that provides product context, steers work, verifies behavior against requirements, and records decisions. It is designed for developers, product teams, and organizations that want to use agents without giving Dezycro access to source code.

treg.to logo

treg.to

treg.to

treg.to is an API gateway and MCP server for calling tools and data providers through one endpoint and credential. It helps agents and developers use cataloged SEO, enrichment, advertising, social, scraping, and other data tools without managing separate provider keys for every metered call.

Agent Router logo
Agent Router

theagentrouter.ai

Agent Router is an open-source Go project for managing unified access to generative AI services through Envoy Gateway. It is intended for teams that want a gateway-based control point for AI service traffic and related agent or MCP workloads.