
Continuous asset discovery and mapping
Maps internal, external, cloud, and third-party exposure, including unknown assets such as subdomains and APIs; the platform describes its map as continuously updated.

Continuous AI-assisted penetration testing and exposure validation for security teams.
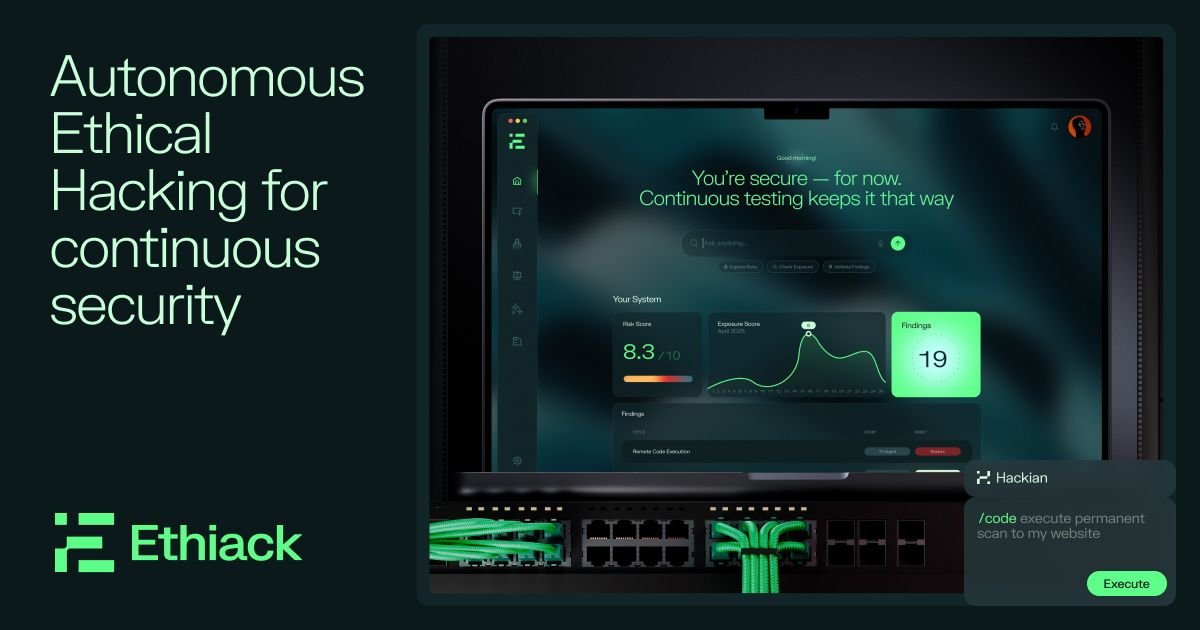
Ethiack is an offensive security platform for continuous attack-surface testing and exposure validation. Its Hackian agentic AI engine maps assets, runs attack scenarios, and attempts to exploit vulnerabilities so teams can distinguish confirmed, actionable risks from unvalidated scanner findings. Confirmed issues include proof-of-exploit and remediation guidance. The platform also supports on-demand penetration tests, ongoing testing, risk-based vulnerability management, and compliance reporting mapped to named frameworks.
Maps internal, external, cloud, and third-party exposure, including unknown assets such as subdomains and APIs; the platform describes its map as continuously updated.
Hackian executes attack scenarios and can chain attack paths, with testing described as continuous and event-driven around code pushes, infrastructure changes, or new knowledge.
Attempts exploitation to validate findings and provides proof-of-exploit for confirmed risks, helping teams assess which vulnerabilities are actionable.
Presents validated risks with impact and mitigation steps so teams can decide what to address first rather than relying only on generic severity scores.
Generates audit-oriented reports and maps validated risks to frameworks including NIS2, DORA, ISO 27001, SOC 2, and PCI DSS.
Offers on-demand web application and API pentesting, as well as continuous platform testing; the pricing page describes reports, retesting, and security testing across assets.
Security teams can use continuous discovery to identify known and previously unknown external assets, including subdomains, APIs, and third-party exposure, then review the evolving attack-surface map.
Teams with a large volume of scanner alerts can use exploitation validation and proof to focus investigation and remediation on confirmed risks.
Organizations can trigger testing around code pushes or infrastructure changes to check for exploitable exposure as their environment changes.
Compliance and security teams can generate reports on demand and use vulnerability evidence mapped to frameworks such as ISO 27001, SOC 2, PCI DSS, NIS2, and DORA.
Organizations needing a time-bounded assessment can request an on-demand web application or API penetration test with a compliance-oriented report and retesting.
The platform describes testing across internal, external, cloud, and third-party assets. The on-demand pentest offer specifically lists web applications and APIs; broader coverage depends on the selected plan.
Hackian attempts exploitation and supplies proof-of-exploit for confirmed risks, alongside prioritization and remediation guidance.
Yes. Ethiack describes continuous testing and event-driven testing associated with code pushes, infrastructure changes, or new knowledge, in addition to on-demand pentests.
The site lists NIS2, DORA, ISO 27001, SOC 2, and PCI DSS as frameworks for mapping validated risks and generating compliance-oriented reports.
The pricing page lists AI and ethical-hacker testing, web application and API testing, black- or grey-box testing, an audit-ready report, remediation advice, and unlimited retesting.
トラフィックデータは参考情報としてご利用ください。

saucelabs.com
Sauce Labsは、Web・モバイルアプリ向けの継続的テストクラウドで、ブラウザ、デバイス、ビジュアル、AI支援テストに対応します。

www.replay.io
Replay QA is an agentic web application testing platform with an automated Security Scan for penetration testing. It explores live apps, tests authenticated journeys, captures runtime evidence, and produces reports that teams can use to remediate security and other software defects.

escape.tech
AI-powered discovery, application testing, and pentesting for security teams

testim.io
Record application flows, add checks and run end-to-end tests. Testim combines AI-assisted element locators with visual test editing and team workflows for web, mobile and Salesforce testing.

reflect.run
Web・モバイル・APIに対応するノーコードAIテスト。

qodex.ai
プルリクエストとデプロイで実シナリオを実行する継続的テスト基盤