
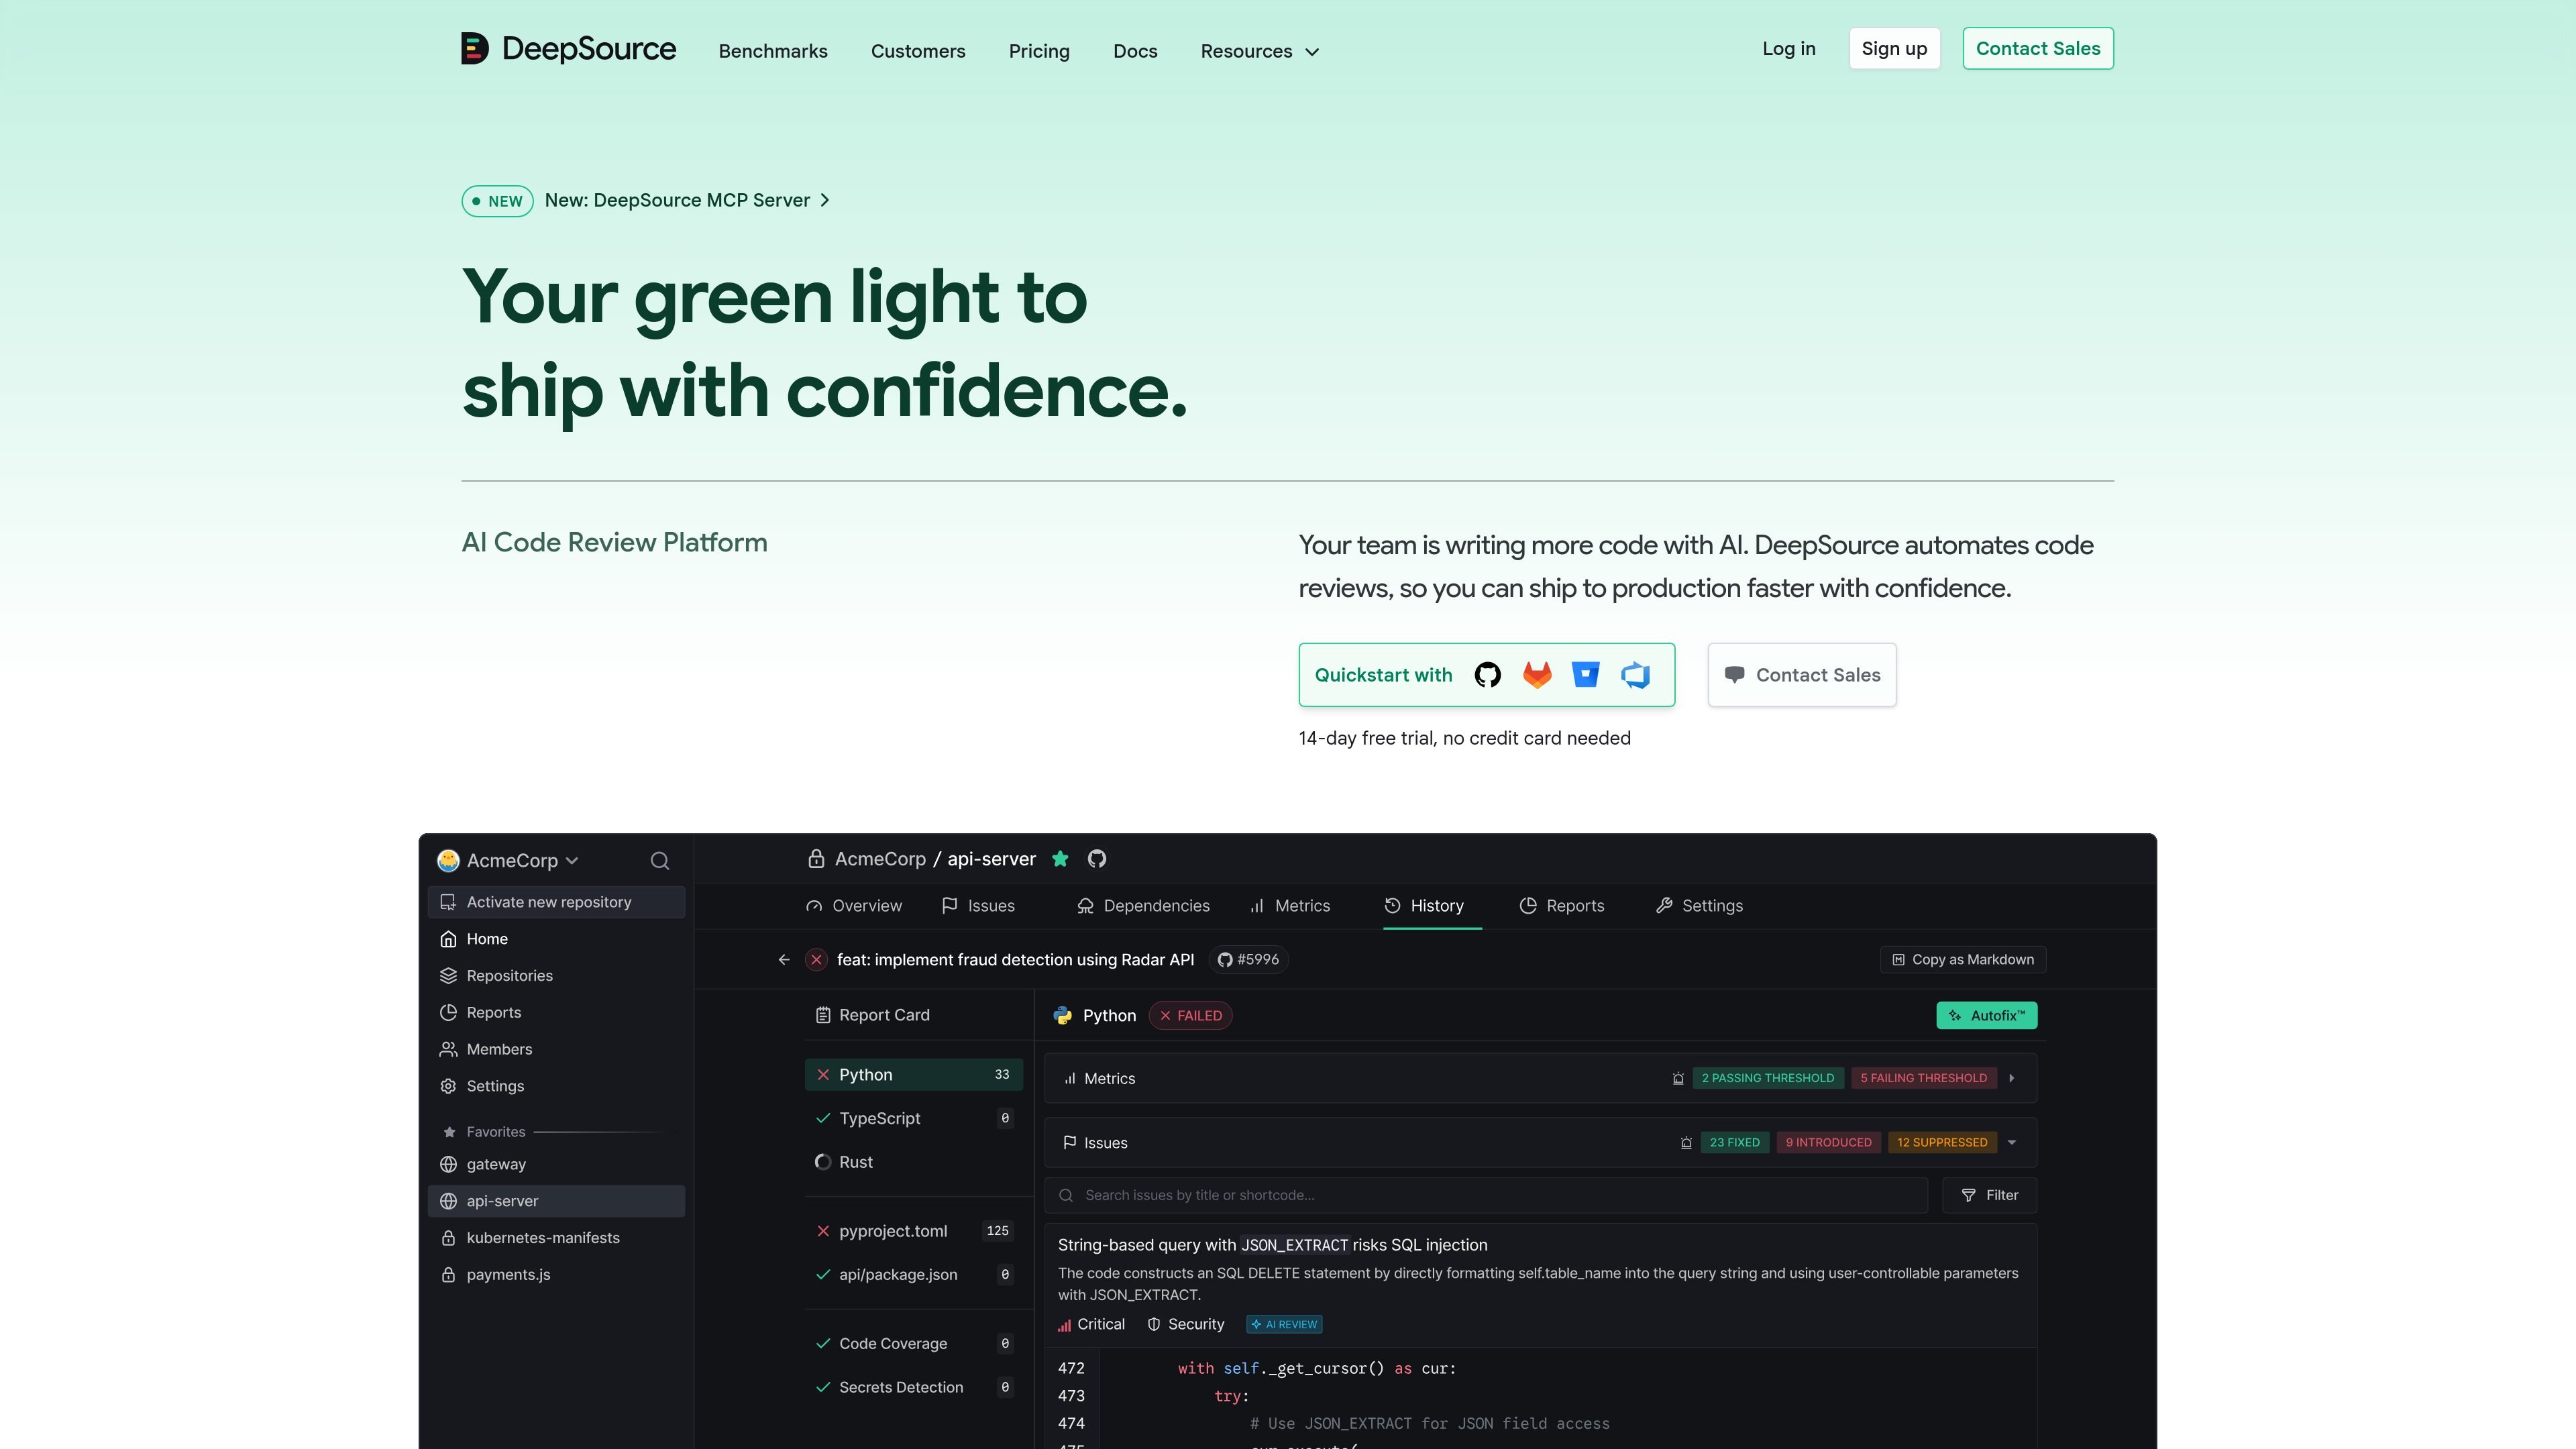
Pull request review
Combines more than 5,000 deterministic rules with an AI review agent to comment on bugs, anti-patterns, and security vulnerabilities in pull requests.

AI-assisted code review and static analysis for software teams.
DeepSource is a code review and application security platform for reviewing pull requests and analyzing codebases. It combines static analysis with AI review to identify bugs, security vulnerabilities, anti-patterns, and code-quality issues, then provides structured feedback in the pull request workflow. Teams can also use it to scan dependencies, track code coverage, detect secrets, and apply quality or security gates before merging.
Combines more than 5,000 deterministic rules with an AI review agent to comment on bugs, anti-patterns, and security vulnerabilities in pull requests.
Provides AI-generated remediation for detected issues, with a diff users can inspect before accepting a change.
Scans open-source dependencies for known vulnerabilities and license compliance issues. Reachability analysis traces calls through the repository and dependency code to determine whether vulnerable code is used.
Includes static analysis, SAST, infrastructure-as-code review, secrets detection, and code coverage tracking; teams can set thresholds and pull request gates.
Provides structured pull request reports, including security, reliability, complexity, hygiene, and coverage areas. Integrations and workflow interfaces listed include Slack, Jira, an API, webhooks, and an MCP server.
Runs open-source formatters on commits or pull requests, and can focus reviews on newly introduced issues so existing findings do not dominate branch feedback.
Use pull request comments and quality or security gates to inspect code produced at a higher pace and prevent changes that fail team-defined criteria from merging.
Use reachability information and recommended remediation paths to prioritize dependency findings and evaluate upgrade options beyond simply moving to the latest version.
Run full-codebase reviews to track code health and security hotspots over time, alongside pull request checks for incoming changes.
Monitor coverage and use security reports organized around frameworks such as OWASP Top 10 and CWE/SANS Top 25 to identify areas needing attention.
The pricing page offers a 14-day free trial and says no credit card is required to start.
Yes. It analyzes pull requests using deterministic rules and an AI review agent, then presents findings as structured feedback and review comments.
Autofix AI can generate remediation patches. The product page says users can inspect the proposed diff before accepting the fix.
Yes. Its SCA capabilities include vulnerability scanning, reachability analysis, and license compliance checks.
The Enterprise plan lists BYOK for AI Review with keys from Anthropic Claude, OpenAI, or Google Gemini; inference runs on the customer's infrastructure.
I dati sul traffico sono solo a scopo di riferimento.
polylane.com
Polylane is an AI operations platform that connects cloud resources, code, and observability data to detect incidents, investigate causes, review production impact, and prepare fixes. It is designed for engineering and DevOps teams that want automated incident response and production change analysis.
hyrax.dev
Hyrax is an AI codebase architecture and engineering review platform for teams working through GitHub. It maps repository structure, evaluates code across six engineering dimensions, and proposes verified changes as pull requests for developers to review and merge.

coderabbit.ai
Code review con IA per pull request, IDE e flussi CLI

graphite.dev
Graphite è una piattaforma di code review connessa a GitHub per pull request impilate, review assistite dall’AI e flussi di merge. Gestisci pull request, feedback e CI in un unico sistema.

gitar.ai
Gitar is an AI-powered code review and pull request automation tool for teams that need to verify changes before merging. It reviews code, diagnoses CI failures, applies fixes under configurable rules, and checks that the pipeline passes.

pullrequest.com
Code review e controlli di sicurezza on-demand con AI ed esperti.