
AI code review with full context
Reviews pull requests with full codebase context, inline comments, AI learnings, pull request summaries, quality gates, and steps to reproduce, so findings are tied to the broader codebase rather than isolated diffs.

Revue de code par IA, analyse de sécurité et tests d’intrusion agentiques
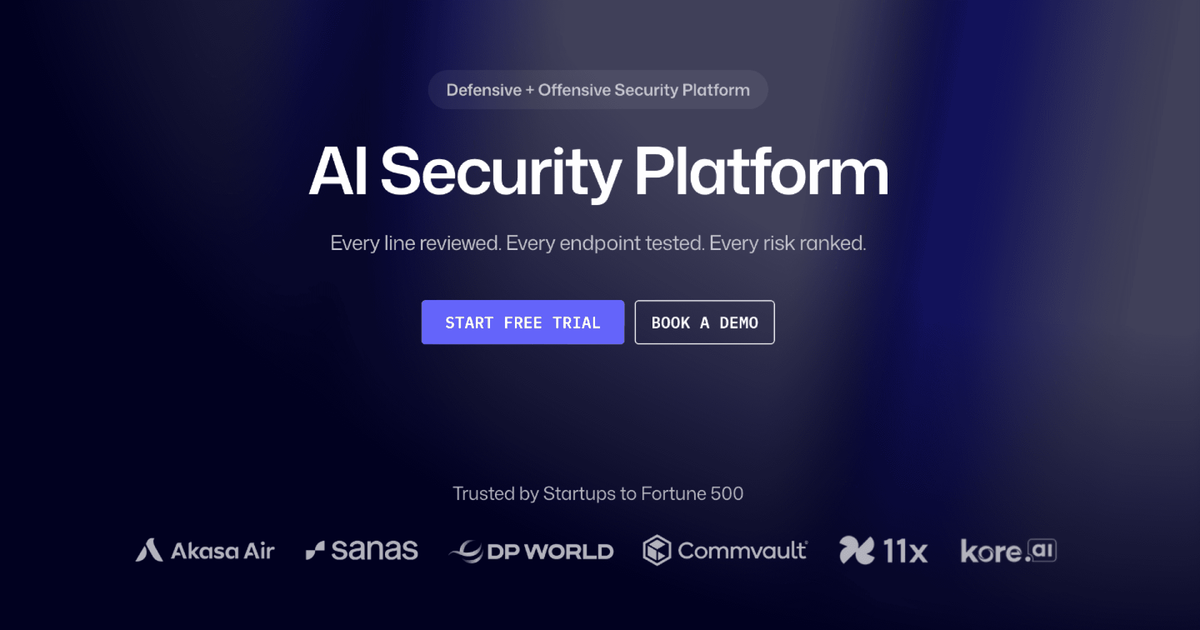
CodeAnt AI is a defensive and offensive security platform that combines AI code review, code security scanning, and agentic penetration testing in one product. The site positions it for teams that want to catch issues in code review and then assess the same application from an attacker’s point of view before release.
The platform’s code review workflow focuses on pull requests, inline fixes, PR summaries, quality gates, and IDE-assisted remediation. Its security side extends into SAST, SCA, secrets, IaC, SBOM, and AI pentesting with black box, white box, and gray box testing, passive reconnaissance, and a 48-hour report path on the pentest page.
Reviews pull requests with full codebase context, inline comments, AI learnings, pull request summaries, quality gates, and steps to reproduce, so findings are tied to the broader codebase rather than isolated diffs.
Surfaces security issues in the editor and supports one-click fixes in IDE workflows such as VS Code, Cursor, and IntelliJ, reducing the need to switch tools during review.
Covers SAST, SCA, secrets, IaC, and SBOM scanning in one code security platform, giving teams a broader static security view beyond pull request review alone.
Runs AI penetration testing in black box, white box, and gray box modes using 500+ exploit agents, with passive recon and attack-chain analysis to build evidence for findings.
Maps exposed attack surface details such as subdomains, open ports, exposed configs, and known CVEs before active testing begins, helping frame the pentest from an external attacker’s perspective.
Connects with common delivery and communication tools shown on the site, including GitHub, GitLab, Bitbucket, Azure DevOps, Jira, and Slack.
Engineering teams can use the pull request review flow to catch issues before merge, get inline feedback, and apply one-click fixes directly in the editor.
Security and platform teams can run broader code scanning for SAST, SCA, secrets, IaC, and SBOM checks to keep build-time security findings in one place.
Teams preparing for a release or assessment can run AI pentesting to map attack surface, explore exploit chains, and receive a report within the published 48-hour window.
Developers working in the editor can use IDE and CLI support to see security issues earlier in the workflow instead of waiting for review comments alone.
Organizations with mixed tools can connect repository, issue-tracking, and collaboration workflows through the integrations shown on the site, including GitHub, GitLab, Bitbucket, Azure DevOps, Jira, and Slack.
The site presents CodeAnt AI as a platform for AI code review, code security scanning, and AI penetration testing. It is aimed at teams that want security checks in the development workflow and a separate pentest report for applications.
The pricing page shows a 14-day free trial with no credit card required for the defensive product path, and a separate free pentest flow is promoted on the site. The enterprise plan is handled through contact sales.
The site lists IDE and CLI support, plus GitHub, GitLab, Bitbucket, Azure DevOps, Jira, Slack, VS Code, Cursor, Windsurf, and IntelliJ across the product pages.
The pricing page includes a Premium plan at $24 per user per month and an Enterprise plan with contact sales. The site also mentions an open source discount and startup discount.
The source text says code review features focus on pull requests, inline review, quality gates, AI learnings, and one-click fixes in the IDE, while pentesting produces a report in 48 hours.
Les données de trafic sont fournies à titre indicatif uniquement.
codity.ai
Codity est une plateforme de revue de code basée sur l’IA qui analyse l’ensemble du contexte du dépôt derrière chaque pull request. Elle aide les équipes d’ingénierie à examiner les changements, à détecter les problèmes de sécurité, à cartographier l’architecture et à suivre les données analytiques des développeurs sur les fournisseurs Git connectés.

hacktron.ai
Revue de code et sécurité applicative par IA pour détecter les vulnérabilités exploitables dans les pull requests

penligent.ai
Penligent est une plateforme de tests d’intrusion assistés par l’AI pour les équipes de sécurité, les pentesters et les red teams. Elle automatise la découverte, la validation, la reproduction d’exploits et les rapports fondés sur des preuves pour les applications web, les API, la logique métier et les agents AI.

comate.baidu.com
Assistant de programmation IA de Baidu pour générer du code, des tests, des commentaires et répondre aux questions dans plus de 100 langages et IDE

www.qodo.ai
Revue et gouvernance du code par IA avec contexte du dépôt
greptile.com
Revue de code IA avec contexte du dépôt pour GitHub et GitLab